200,000 WordPress Sites Affected by Unauthenticated Critical Vulnerabilities in Anti-Spam by CleanTalk WordPress Plugin

On October 30th, 2024, we received a submission for an Authorization Bypass via Reverse DNS Spoofing vulnerability in Anti-Spam by CleanTalk, a WordPress plugin with more than 200,000 active installations. This vulnerability makes it possible for an unauthenticated attacker to install and activate arbitrary plugins on a vulnerable site, which can be leveraged to achieve remote code execution. A few days later on November 4th, our Threat Intelligence Team discovered another vulnerability in the same functionality that could be leveraged to perform the same actions.

Props to mikemyers who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $4,095.00 for this discovery.

Paid Wordfence users received a firewall rule to protect against any exploits targeting the first vulnerability, Authorization Bypass via Reverse DNS Spoofing, on October 30, 2024. Sites using the free version of Wordfence will receive the same protection 30 days later on November 29, 2024.

Paid Wordfence users received a firewall rule to protect against any exploits targeting the second vulnerability, Authorization Bypass due to Missing Empty Value Check, on November 4, 2024. Sites using the free version of Wordfence will receive the same protection 30 days later on December 4, 2024.

Wordfence contacted the CleanTalk team on October 30, 2024, and received a response on the same day. After providing full disclosure details, the developer released the first patch on November 1, 2024, and the second patch on November 14, 2024. We would like to commend the CleanTalk team for their prompt response and timely patch.

We urge users to update their sites with the latest patched version of Anti-Spam by CleanTalk, version 6.45 at the time of this writing, as soon as possible. All clients of ProtectYourWP.com were updated within 24 hrs of the patch releases.

Source and more details: https://www.wordfence.com/blog/2024/11/200000-wordpress-sites-affected-by-unauthenticated-critical-vulnerabilities-in-anti-spam-by-cleantalk-wordpress-plugin

Worst passwords of 2024 prove we still suck at digital security

It’s 2024 and people are still using “123456.”

NordPass has released its sixth annual study on the 200 most common passwords in the world. Unfortunately, it seems as though the sixth time is still not the charm, with the list still topped by many of the same easily-cracked suspects as last year.

“After analyzing 6 years’ worth of data, we can say there hasn’t been much improvement in people’s password habits,” wrote NordPass. It’s easy to imagine an air of resignation surrounding that statement.

This year NordPass’ study was conducted in collaboration with NordStellar, and used a 2.5TB database of information gathered from publicly available resources — including some found on the dark web. Passwords used had been exposed via malware or in data leaks, with the complete study using information from people across 44 countries.

According to NordPass’ research, 2024’s top 10 most used passwords globally are:

  1. 123456
  2. 123456789
  3. 12345678
  4. password
  5. qwerty123
  6. qwerty1
  7. 111111
  8. 12345
  9. secret
  10. 123123

NordPass estimates that it would take a hacker less than one second to crack each of these passwords. This is the fifth year that “123456” has topped the list, having only been beaten out once since NordPass began its annual study.

The list looks slightly different when strictly looking at passwords for U.S. accounts, though there’s still a lot of overlap. While the global list favours number-based passwords, presumably as they’re used across different languages, 2024’s 10 most popular passwords in the U.S. has more English-based entries:

  1. password
  2. qwerty123
  3. qwerty1
  4. 123456789
  5. password1
  6. 12345678
  7. 12345
  8. abc123

These too would take less than a second to crack.

Corporate America’s most popular password is ‘password’

This year, NordPass also made a separate list of passwords used for corporate accounts. Most passwords used in the study were leaked alongside a corresponding email address, enabling NordPass to distinguish between work and personal accounts by looking at the domain name.

Sadly, it looks as though those hours of mandatory corporate privacy training we’ve all endured have borne little fruit, with people still using the same or similar weak passwords as they do in their private lives.

The 10 most popular passwords people used at work in 2024 are:

  1. 123456 
  2. 123456789
  3. 12345678
  4. secret
  5. password
  6. qwerty123
  7. qwerty1
  8. 111111
  9. 123123
  10. 1234567890

In the U.S. specifically, 2024’s most popular corporate passwords are:

  1. password
  2. 123456
  3. qwerty123
  4. qwerty1
  5. aaron431
  6. password1
  7. welcome
  8. 12345678
  9. Password1
  10. abc123

“aaron431” is an unusual outlier compared to its compatriots, having no blatantly obvious rhyme or reason. However, it has been recognised as a popular password in several industries for years. Some have speculated that “aaron431” is the default password for a widely used program, and that people just haven’t bothered changing it. NordPass estimates it would take about five minutes for a hacker to crack it.

If you’re guilty of using any of these popular passwords, now would be a good time to consider changing them and getting a password manager. Even if you don’t use any of the entries on these lists, a password manager will still go a long way in helping you keep your passwords strong and your data secure.

Source: https://mashable.com/article/worst-passwords-2024-nordpass

4,000,000 WordPress Sites Using Really Simple Security Free and Pro Versions Affected by Critical Authentication Bypass Vulnerability

Introductory Note: This is one of the more serious vulnerabilities that we have reported on in the 12 year history of Wordfence as a security provider for WordPress. This vulnerability affects Really Simple Security, formerly known as Really Simple SSL, installed on over 4 million websites, and allows an attacker to remotely gain full administrative access to a site running the plugin.

The vulnerability is scriptable, meaning that it can be turned into a large scale automated attack, targeting WordPress websites. The vendor worked with the WordPress plugins team to force-update all sites running this plugin before we published this post.

You Can Help by creating as much awareness around this issue in the community as possible, ensuring that any laggard and unmaintained sites update to the patched version. We encourage hosting providers to force-update their customers and perform scans on their hosting filesystems to ensure no customer is running an unpatched version of this plugin.

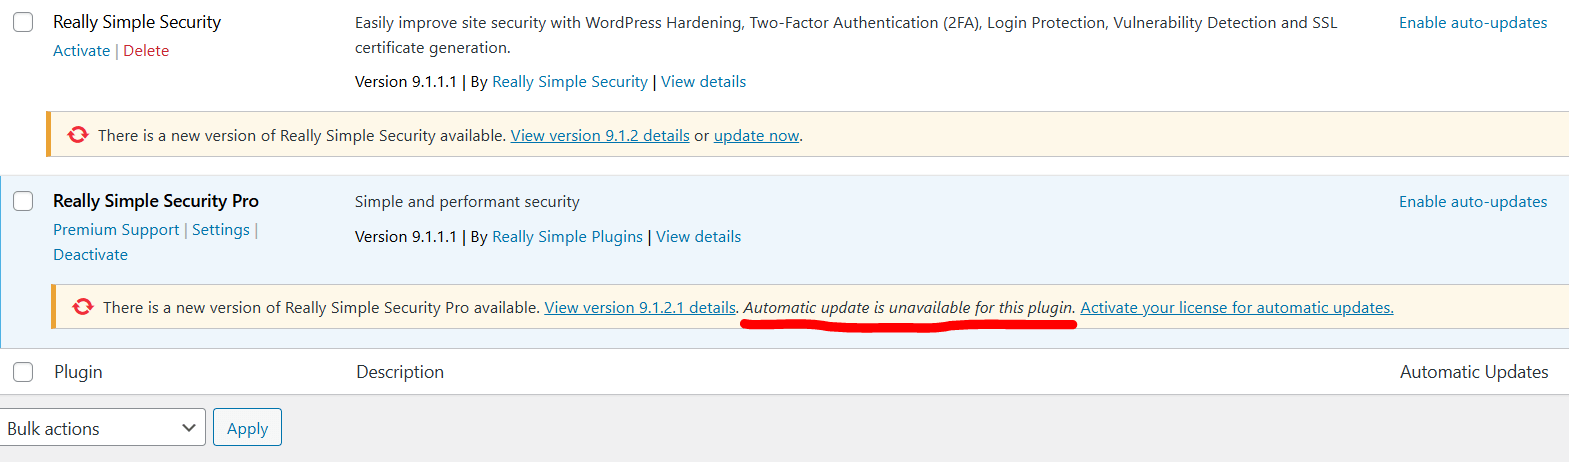
It’s important to note that the Pro versions of this plugin are also affected by this vulnerability and sites running the premium versions should verify that they have automatically updated, so please do help get the word out. It appears that sites without a valid license may not have auto-updates functioning.

The Details

On November 6th, 2024, the Wordfence Threat Intelligence team identified and began the responsible disclosure process for an Authentication Bypass vulnerability in the Really Simple Security plugin, and in the Really Simple Security Pro and Pro Multisite plugins, which are actively installed on more than 4,000,000 WordPress websites. The vulnerability makes it possible for an attacker to remotely gain access to any account on the site, including the administrator account, when the two-factor authentication feature is enabled.

Paid Wordfence users received a firewall rule to protect against any exploits targeting this vulnerability on November 6, 2024. Sites using the free version of Wordfence will receive the same protection 30 days later on December 6, 2024.

Wordfence contacted the Really Simple Plugins team on November 6, 2024, and received a response on November 7, 2024. After providing full disclosure details, the developer released the patch for the Pro plugins on November 12, 2024, and for the Free plugin on November 14, 2024.

Due to the critical severity of this vulnerability (CVSS score 9.8 Critical), the plugin vendor worked with the WordPress.org plugins team to push a forced security update to the patched version, 9.1.2, for anyone running a vulnerable version of the plugin. This means most sites should already be patched or will be patched soon, however, we urge users to verify that their sites were updated to the latest patched version of Really Simple Security, version 9.1.2 at the time of this writing, as soon as possible if running version 9.0.0 or newer. A thread in the WordPress.org forum for the plugin indicates that the forced updates began this morning and may continue over the next few days.

Source and more details: https://www.wordfence.com/blog/2024/11/really-simple-security-vulnerability

See also: https://www.techradar.com/pro/security/millions-of-wordpress-sites-could-be-at-risk-from-one-of-the-most-serious-plugin-flaws-ever-found

7,000 WordPress Sites Affected by Unauthenticated Critical Vulnerabilities in LatePoint WordPress Plugin

On September 17, 2024, the Wordfence Threat Intelligence team identified and began the responsible disclosure process for two critical vulnerabilities in the LatePoint plugin, which is estimated to be actively installed on more than 7,000 WordPress websites.

The Unauthenticated Arbitrary User Password Change vulnerability makes it possible for an unauthenticated attacker to change the password of any user, including an administrator, which allows them to take over the account and the website. The Authentication Bypass vulnerability makes it possible for an attacker to gain access to any account on the site, including any administrator accounts.

Paid Wordfence users received firewall rules to protect against any exploits targeting these vulnerabilities on September 17, 2024. Sites using the free version of Wordfence receive the same protection 30 days later on October 17, 2024.

Wordfence contacted the LatePoint team on September 17, 2024, and received a response the same day. After providing full disclosure details, the developer released the first patch on September 20, 2024, and the second patch on September 24, 2024. We would like to commend the LatePoint team for their prompt response and timely patch.

We urge users to update their sites with the latest patched version of LatePoint, version 5.0.13 at the time of this writing, as soon as possible.

Source and more details: https://www.wordfence.com/blog/2024/10/7000-wordpress-sites-affected-by-unauthenticated-critical-vulnerabilities-in-latepoint-wordpress-plugin

28,000 WordPress Sites Affected by Arbitrary File Read and Deletion Vulnerability in WPLMS WordPress Theme

On October 19th, 2024, Wordfence received a submission for an Arbitrary File Read and Deletion vulnerability in WPLMS, a WordPress premium theme with more than 28,000 sales. This vulnerability makes it possible for unauthenticated threat actors to read and delete arbitrary files, including the wp-config.php file, which can make site takeover and remote code execution possible.

Props to Foxyyy who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $900.00 for this discovery.

Paid Wordfence users received a firewall rule to protect against any exploits targeting this vulnerability on October 28, 2024. Sites using the free version of Wordfence will receive the same protection 30 days later on November 27, 2024.

Wordfence contacted the VibeThemes team on October 28, 2024, and on November 4, 2024, and received a response on November 5, 2024. After providing full disclosure details, the developer released a patch on November 8, 2024. We would like to commend the VibeThemes team for their prompt response and timely patch.

We urge users to update their sites with the latest patched version of WPLMS, version 4.963 at the time of this writing, as soon as possible.

Source and more details: https://www.wordfence.com/blog/2024/11/28000-wordpress-sites-affected-by-arbitrary-file-read-and-deletion-vulnerability-in-wplms-wordpress-theme

Google issues ‘severe’ Android alert – how to check if your device is affected

If you have an Android smartphone, you need to make sure you do one thing – and right now.

Google recently identified 51 bugs that could expose devices to cybercriminal attacks.

The company this week issued an ‘update now warning’ for millions of Pixel and Samsung users to install the new software to patch out these vulnerabilities.

Two of the flaws are known as ‘zero days’ – when hackers discover a glitch before developers, so have limited time to exploit it before it’s patched.

In this case, hackers can use these zero days to slip spyware into phones so they can monitor people’s activities.

‘The most severe of these issues is a high-security vulnerability in the System component that could lead to remote code execution with no additional execution privileges needed,’ Google warned.

We’ll spare you the technical jargon, but one zero day, CVE-2024-43093, can allow cybercriminals to peek into Android phones’ sensitive data or perform unauthorised actions.

This glitch, according to Google, is a ‘privilege escalation flaw’ impacting the Google Play system.

The other zero day, called CVE-2024-43047, affects a microprocessor chip in Android phones that processes digital signals.

The flaw enables hackers to corrupt phone memory and gain unauthorised access. America’s Cyber Defence Agency has mandated all federal employees update their phones to fix the bug.

Source: https://metro.co.uk/2024/11/07/google-issues-severe-android-alert-check-device-affected-21949655/

Fake “Fix It” Pop-Ups Target WordPress Sites via Malicious Plugin to Download Trojan

In a recent investigation by Sucuri Security a new malware campaign was discovered targeting WordPress sites through a fake plugin, universal-popup-plugin-v133, which delivers deceptive browser fix pop-ups. This malware leverages social engineering tactics to deceive visitors into downloading malicious files, compromising their systems.

Type of website impacted and the scope of infection

Sucuri reported a similar fake browser update in a recent June article. The current version of this malware affects WordPress sites, and Sucuri saw a similar case in August, 2024 which is now detected by their SiteCheck tool as malware.fake_update.7.

As of October 18th, 31 sites were known to be infected with this malware.

The malware is a Trojan that downloads from a compromised WordPress site after users are tricked into running it via fake pop-ups, where it then executes potentially harmful software on the user’s system.

How the malware works

Once installed on a compromised WordPress site, the fake plugin universal-popup-plugin-vXXX generates pop-ups that detect the user’s browser and regional language, making the attack appear more personalized and legitimate.

The Malicious Plugin Code

The plugin’s index.php file contains a malicious code that loads the JavaScript responsible for generating the fake pop-up. This code includes a JavaScript file named assets/popup.js which triggers the malicious pop-up on the frontend of the site.

The file assets/popup.js contains obfuscated code, which when decoded appends an iframe to the body of the webpage, loading the popup.html file from the plugin’s assets directory, which displays the fake browser update message.

When a user visits an infected site, they are shown an error message pop-up saying:

“Aw, Snap! Something went wrong while displaying this webpage.”

This fake error mimics legitimate browser messages, tricking users into believing that something is wrong with their browser.

The pop-up instructs the user to “install the root certificate” by clicking on a fake button labeled How to Fix. Upon clicking this button, a new pop-up appears with detailed instructions for running malicious commands on PowerShell.

The second pop-up provides the instructions to run a set of commands on your Windows PowerShell Admin that are copied on the user’s clipboard after they click the copy button. When users follow these instructions, the malicious code is executed in PowerShell, downloading an executable file.

This script hides the downloaded file from Windows Defender by adding it to an exclusion list, downloads the malicious Trojan from the specified URL, and then silently executes it on the user’s machine.

The PowerShell script retrieves an executable file named Setup.exe.

The Setup.exe file downloaded through this malicious campaign has been scanned on VirusTotal and flagged as malicious by 21 security vendors. The file is categorized as Trojan.MSIL, confirming its dangerous nature.

How does it affect the users?

Users who unknowingly execute this PowerShell script end up downloading and running a Trojan, which can have severe consequences, such as data theft, remote control of the machine, and/or further exploitation.

Prevention Tips

As a website owner, it’s important to take a proactive approach to security to mitigate risk from threats:

  1. Employ a “use it or lose it” policy on your website. That means regularly review all plugins and remove any components that you don’t recognize or aren’t in use.
  2. Generate strong and unique passwords for all of your accounts, including admins, FTP, database, and hosting.
  3. Regularly monitor your website and check for suspicious activity or unexpected website admin users.
  4. Consider using 2FA (2-factor authentication) and restricting access to your WordPress admin and sensitive pages to allow access to only trusted IP addresses.
  5. Always keep your website software patched and up-to-date, including your core CMS, plugins, themes, or any other extensible components.
  6. Use a web application firewall to help prevent vulnerability exploits, malicious code, and hack attempts.

[Editor’s note: steps 2,3, 5, and 6 are implemented on all ProtectYourWp client’s sites. 2FA and trusted IP address restrictions are available if you are interested. Contact us for details.]

Source and more details: https://blog.sucuri.net/2024/10/fake-fix-it-pop-ups-target-wordpress-sites-via-malicious-plugin-to-download-trojan.html

10,000 WordPress Sites Affected by Arbitrary File Upload Vulnerability in AI Power: Complete AI Pack WordPress Plugin

On October 23rd, 2024, Wordfence received a submission for an Arbitrary File Upload vulnerability in AI Power: Complete AI Pack, a WordPress plugin with more than 10,000 active installations. This vulnerability makes it possible for an unauthenticated attacker to upload arbitrary files to a vulnerable site and achieve remote code execution.

Props to vgo0 who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $650.00 for this discovery.

All Wordfence customers are protected against any exploits targeting this vulnerability by the Wordfence firewall’s built-in Malicious File Upload protection.

Wordfence contacted the AI Power team on October 25, 2024, and received a response on the same day. After providing full disclosure details, the developer released a patch on October 26, 2024. We would like to commend the AI Power team for their prompt response and timely patch.

We urge users to update their sites with the latest patched version of AI Power: Complete AI Pack, version 1.8.90 at the time of this writing, as soon as possible.

Source and more details: https://www.wordfence.com/blog/2024/10/10000-wordpress-sites-affected-by-arbitrary-file-upload-vulnerability-in-ai-power-complete-ai-pack-wordpress-plugin