
The Wordfence Threat Intelligence Team recently identified an interesting malware family on May 16, 2025 during a site clean. This malware family shared a codebase but varied in features across different versions, including credit card skimming and WordPress credential theft. Most surprisingly, one variant incorporated a live backend system hosted directly on infected websites for attacker use – a previously unseen method – packaged and disguised as a rogue WordPress plugin.
Further research uncovered evidence of this campaign in the Threat Intelligence platform dating back to September 2023, indicating a prolonged operation targeting multiple entities. Analysis of the malware’s growing codebase of more than 20 samples provided unique insights into the evolution of this framework.
Several malware detection signatures were developed and released after undergoing the Wordfence Q&A process between May 17 and June 15, 2025. All paid Wordfence customers received these signatures immediately, along with paid Wordfence CLI Users. Users of the free versions of Wordfence and Wordfence CLI receive the same signatures after the standard 30-day delay.
As part of their product lineup, Wordfence offers security monitoring and malware removal services. In the event of a security incident, their incident response team will investigate the root cause, find and remove malware from your site, and help with other complications that may arise as a result of an infection. During the cleanup, malware samples are added to their Threat Intelligence database, which contains over 4.4 million unique malicious samples. The Wordfence plugin and Wordfence CLI scanner detect over 99% of these samples and indicators of compromise, when using the premium signature set. Wordfence CLI can scan your site even if WordPress is no longer functional and is an excellent layer of security to implement at the server-level, part of their mission to secure the web by Defense in Depth.
Malware Analysis: Shared Features
All of the malware samples analyzed employ identical obfuscation techniques and often incorporate anti-analysis measures to evade detection. Common anti-analysis features observed include developer tools detection and console rebinding. Other shared features are found in most samples, suggesting an ongoing development effort over the years.
Developer Tools Detection and Analysis Evasion
To evade analysis, malware often employs a technique to detect if a browser’s developer tools (like Firefox Developer Tools or Chrome DevTools) are active: if detected, the malware – when properly implemented – will often alter its behavior to avoid detection in the console.
The code continuously checks the difference between window.outerWidth / outerHeight and window.innerWidth / innerHeight and dispatches a custom devtoolschange event with the details. A significant difference may indicate the developer tools are open. In most samples the data collection and exfiltration logic is designed to check the developer tools status before proceeding.
Further investigation unveiled even more advanced anti-analysis techniques in certain samples, like infinite loops and debugger traps.
The code is designed to effectively block analysis, either by creating and executing a function containing an infinite while(true) loop intended to freeze or crash a browser tab or the developer tools, or programmatically inserting debugger statements that will pause execution if developer tools are open.
Some malware samples also included functionality to prevent the use of typical browser debugging shortcuts. For instance the code deactivates right-click context menus, the F12 key (commonly used to access browser debug tools), Ctrl + Shift + I / J (methods to open developer tools or the browser console), and Ctrl + U (for viewing page source).
Console Rebinding
Later iterations of this malware incorporate a sophisticated mechanism for dynamically rebinding console methods within the browser environment: this advanced anti-analysis technique is specifically designed to obstruct reverse engineering efforts and slow debugging processes.
Targeted Execution
All of the malware variants Wordfence analyzed include checks to limit their activity to specific website areas. For example, they avoid running in the WordPress admin panel to prevent detection, or ensure they operate only on checkout pages. Some variants use cookies to recognize and evade site administrators and users who have already had their information stolen.
Recent variants of this malware also include a list of disallowed email address and domain names which is later checked against billing data, likely to avoid targeting specific accounts, and again in order to evade detection.
Form Manipulation
Most of the malware variants use techniques like form manipulation, injection, overlays, or hijacking to steal payment and billing information. These methods varied based on the website and integrated payment gateways; sometimes multiple approaches are combined. The prevalent technique involved directly intercepting payment and billing data from HTML forms.
Another common implementation consists in a Base64 encoded string containing the HTML code to resemble a fake payment form, which is then appended to the legitimate WooCommerce payment box.
In some cases Wordfence observed a form overlay technique similar to the one found in a sophisticated & stealthy formjacking malware recently analyzed, even though this malware family differs in several ways – most notably a different approach to persistence and resilience – while still repurposing legitimate web technologies for uses that directly undermine security and privacy, albeit in a different way.
For instance the malware makes use of localStorage to store configuration data within a victim’s browser. This technique allows the malware to persist and maintain its presence across browsing sessions, even without directly manipulating cookies.
Other variants opted for a direct manipulation of the generated HTML code, in some cases even adding pseudo-validation in order to provide visual feedback, making the tampered form appear legitimate.
One sample inspected also included a surprisingly complete fake human verification challenge, dynamically injected as a fullscreen and multi-language screen, intended to serve both as a user deception device and as an anti-bot filter.
This includes incredibly advanced features for malware, like text localized in multiple languages, CSS support for RTL languages and dark mode, interactive elements like animations and spinning SVGs, and a definite Cloudflare brand impersonation, revealing a complexity rarely encountered before.
Data Exfiltration
Almost all of the malware variants use the same method to exfiltrate billing and payment data using custom encoding. Once collected, all data is concatenated into a single string then Base64 encoded and further encoded via a custom scheme, alternating a “percent” character.
In most cases the stolen data is encoded and appended as a query parameter to a fake image URL hosted on an attacker controlled server, triggering an HTTP GET request to exfiltrate the data.
Furthermore, the server, path, and query parameters varied across analyzed samples, complicating detection efforts.
In one case Wordfence also found a notable post-skim action. After successful exfiltration, the script hides the injected form and significantly manipulates an error message code to display a fake payment gateway error. This is a highly deceptive social engineering tactic, designed to explain the failed transaction to the end user delaying suspicion about the data theft.
Non-Skimming Variants
Wordfence analysis involved a detailed examination of several malware samples, revealing some diversity in their underlying logic and intended functionality while still retaining most of the shared features. Even though most samples exhibited characteristics consistent with credit card skimming operations, their investigation uncovered three distinct variants.
These variants appear to be specifically engineered for a range of different malicious activities, including manipulation of Google Ads for fraudulent purposes, theft of WordPress login credentials, and distribution of further malware payloads to the end users, effectively denominating this malware family as a framework.
The malware variant specializing in malicious advertising kept most of its original functionalities but replaced the formjacking and data theft components. Instead, it was designed to selectively show ads if a user arrived from a known search engine or social media platform and was on a mobile device.
A different version of the malware targeted WordPress login credentials and other user data. It employed the same data theft and exfiltration techniques seen in previously analyzed samples.
This malware framework was also used to dynamically replace links on infected websites with attacker-controlled ones. This allowed for the further spread of malware by distributing malicious versions of the originally linked content to users.
User Tracking And Profiling
Certain malware samples, primarily designed for malicious advertising, utilized sophisticated tracking and profiling methods. These techniques gathered information about the user’s browser, operating system, and device type, and also categorized them based on traffic sources like search engines, social media, email, mobile apps, and referrals. To increase effectiveness and avoid serving ads to search engine bots a mechanism was implemented to identify and filter out automated tools, allowing for the collection of statistics specifically from genuine users.
Wordfence also observed a refined target reconnaissance routine aimed at targeted payload delivery, an evolution of previously observed similar code. All the information is encoded and appended as parameters to the remote payload URL, allowing attackers to receive detailed contextual information about the target, likely in order to deliver the most appropriate payload via a dynamic script inclusion.
Logging and Telemetry
Some malware samples use a direct Telegram channel for immediate and secret exfiltration of sensitive data from compromised systems in real time. This includes personal information like system and browser details. The malware also monitors and transmits user actions and identifies the compromised website or the site active during the attack, allowing attackers to understand the breach context and refine their targeting.
Malware Evolution: A Rogue WordPress Plugin
The exploration of these sophisticated malware features has been insightful, with most functionality aligning with expectations. However, certain samples displayed unique characteristics, indicating sustained and distinctive development efforts.
The initial sample was bundled with a deceptive fake WordPress plugin. This unconventional tactic of pairing skimming malware with a plugin, contrary to typical attacker strategies aimed at evading detection, immediately drew the Wordfence analyst’s attention.
The plugin presents itself as well structured, following common development best practices such as separated folders for administrative and public facing code. However – unlike a recently analyzed malware masquerading as a legitimate WordPress plugin – a quick inspection would reveal most files to be just empty scaffolding. Clearly the fake plugin was not affiliated in any way with WordPress or WooCommerce, even though it’s a fairly common tactic used by attackers to deceive their victims.
Both the code features and style indeed suggests the plugin template was likely generated by AI (Wordfence were able to track down some code features from publicly available code snippets). However some characteristics would catch the eye, like the misspelling of “WordPress” in the plugin name or the vague plugin description:
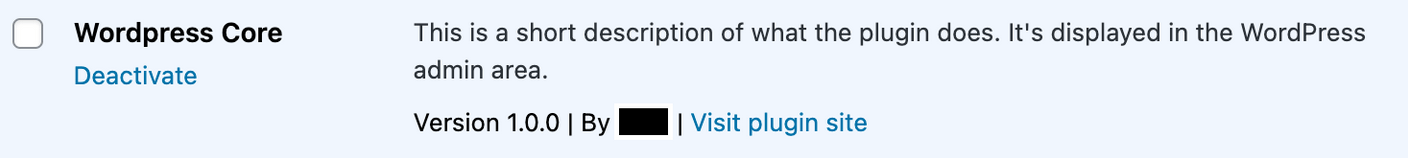
The actual credit card skimmer is found in wordpress-core-public.js. It is designed to directly skim data from existing, legitimate form fields on the page and it is highly selective about where and when it executes, targeting only the checkout page and avoiding administrative users as discussed before.
In addition to the credit card skimmer, the plugin contained PHP files that allow it to act as a server-side building block to complement this attack, effectively converting the compromised website into a custom interface available to the attackers.
The code found in the register-messages-posttype.php file creates a “messages” custom post type, which is used as backend infrastructure for collecting and managing the stolen data, and provides a custom link into the “My Account” view for convenience, which would allow users of any level access to the store orders despite the lack of capabilities.
Furthermore, the malicious code found in wordpress-core.php extends the skimming attack to the website backend, in order to ensure that the fraudulent transactions remain undetected and unprocessed as long as possible. This is achieved by leveraging the available hooks woocommerce_thankyou and wp_footer with routines to periodically scan the database for orders in progress and update their status to “wc-completed” in an attempt to evade or at least delay detection.
This rogue WordPress plugin represents a significant escalation for credit card skimmers. While the JavaScript code is responsible for capturing payment data and billing information, the PHP counterparts act as a backend directly on the compromised website.
Indicators of Compromise
The analyzed malware samples employed significant obfuscation, using a widely recognized algorithm, to evade detection; the same obfuscation technique is also frequently used by commercial plugins and themes to protect their intellectual property.
While common, this practice presents a challenge for malware analysts in developing reliable signatures for known threats. This may lead to occasional false positive detections for legitimate premium software, and complicates the listing of indicators of compromise.
- advertising-cdn\.com
- api-service-188910982\.website
- blastergallery\.com
- chaolingtech\.com
- contentsdeliverystat\.com
- deliveryrange\.pro
- emojiselect\.info
- graphiccloudcontent\.com
- imageresizefix\.com
- imagifytext\.com
- internetmemoryservice\.com
- staticdelivery\.net
- vectorimagefabric\.com
- vectorizegraphic\.com
- api.telegram\.org/bot7468776395[…]chat_id=-4672047987
- ca-pub-9514222065914327
Conclusion
In today’s blog post Wordfence highlighted an interesting malware family targeting various systems with diverse capabilities, including stealing credit card information and WordPress credentials. Additionally, Wordfence detailed a novel bundle of credit card skimmers and malicious WordPress plugins which combines malicious actions with features developed for the attacker’s convenience.
Wordfence paid customers received malware signatures to detect these infected plugins between May 17 and June 15, 2025. Wordfence free users and Wordfence CLI free users receive signatures after a 30 day delay.
Source and more details (including code snippets): https://www.wordfence.com/blog/2025/06/a-deep-dive-into-a-modular-malware-family/