Fake LastPass, Bitwarden breach alerts lead to PC hijacks

An ongoing phishing campaign is targeting LastPass and Bitwarden users with fake emails claiming that the companies were hacked, urging them to download a supposedly more secure desktop version of the password manager.

The messages direct recipients to download a binary that BleepingComputer has discovered installs Syncro, a remote monitoring and management (RMM) tool used by managed service providers (MSP) to streamline IT operations.

The threat actors are using the Syncro MSP program to deploy the ScreenConnect remote support and access software.

‘Vulnerable’ old .EXE installs

In a threat alert this week, LastPass makes it clear that the company did not suffer any cybersecurity incident and that the messages are a social engineering effort by a threat actor.

“To be clear, LastPass has NOT been hacked, and this is an attempt on the part of a malicious actor to draw attention and generate urgency in the mind of the recipient, a common tactic for social engineering and phishing emails,” LastPass says.

According to the company, the campaign started over the weekend, presumably to take advantage of the reduced staffing over the Columbus Day holiday weekend and delay detection.

The phishing emails are well crafted and urge recipients to install a more secure desktop app that LastPass developed as an MSI replacement for the “outdated .exe format” that had weakenesses that allowed access to vault information.

“Attackers exploited weaknesses in older .exe installations, which could, under certain conditions, allow unauthorized access to cached vault data,” reads the fake security alert from the threat actor.
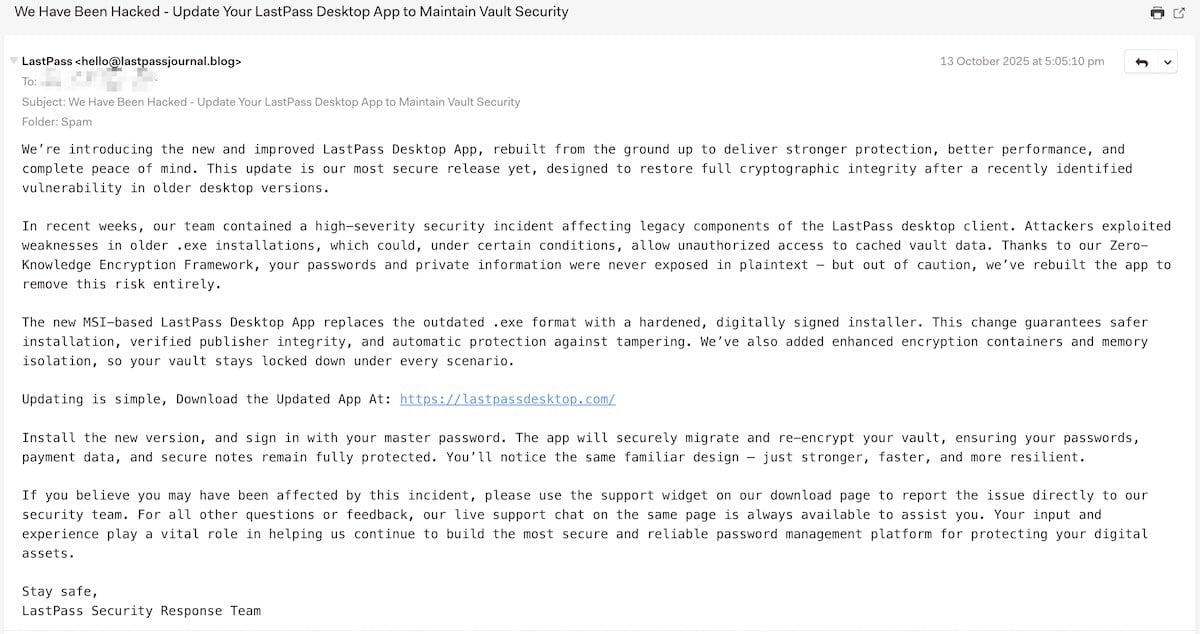
Phishing email impersonating LastPass
Source: BleepingComputer

LastPass notes that the fake messages come from ‘hello@lastpasspulse[.]blog’ but BleepingComputer also saw emails delivered from ‘hello@lastpasjournal[.]blog’.

Bitwarden users also targeted

The phishing emails also impersonate Bitwarden and share the same writing style and lure in an attempt to create a sense of urgency and convince recipients to follow the download link to an improved deskop application.

Yesterday, BleepingComputer received a notice from ‘hello@bitwardenbroadcast.blog’ describing a similar security incident that prompted the release of a secure client app that users need to install.
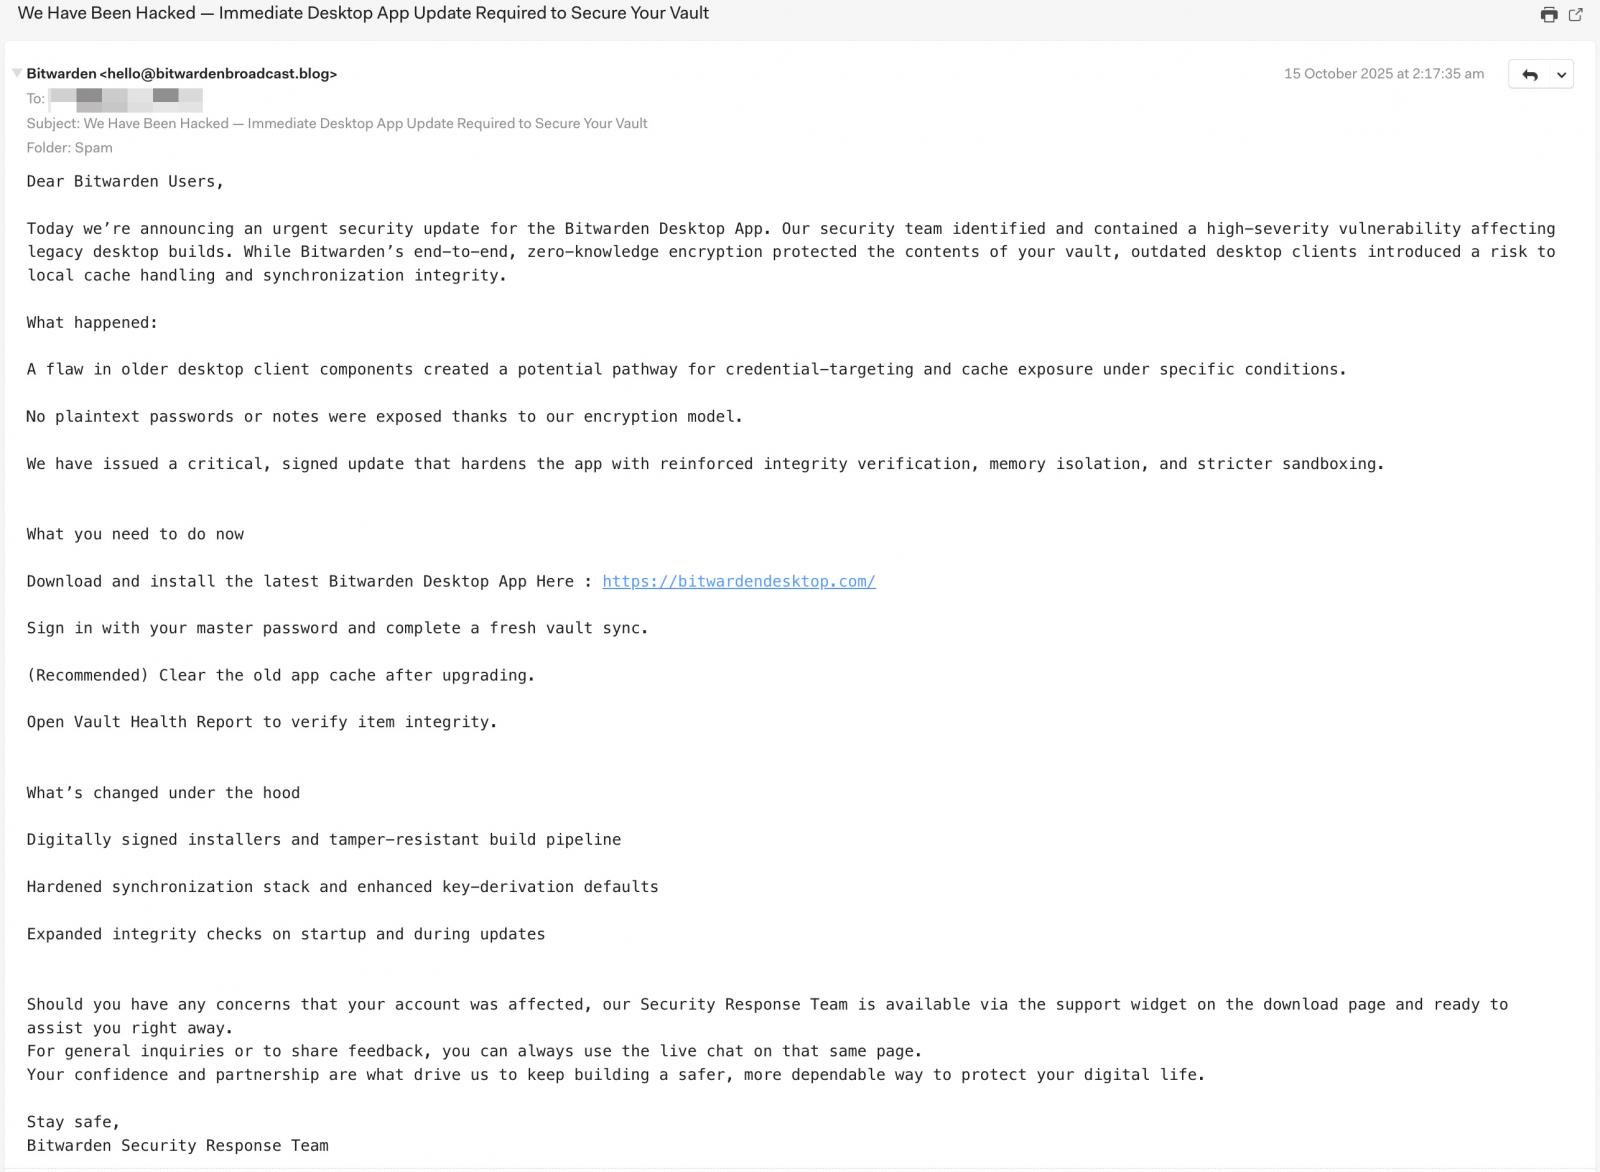
Bitwarden phishing email
Phishing email impersonating Bitwarden
Source: BleepingComputer

At the time of writing, Cloudflare is blocking access to the landing pages included in the fraudulent emails and is marking them as phishing attempts.

Legitmate tools for remote access

BleepingComputer retrieved the binary samples distributed in the phishing emails targeting LastPass and Bitwarden users and found that they are functionally the same.

The malware installs the Syncro MSP platform agent with parameters that hide its system tray icon in an effort to keep the user unaware of the new tool.

Based on our observations, Syncro’s single purpose appears to be to deploy the ScreenConnect support tool as a “bring-your-own” installer, which gives the threat actor remote access to the endpoint.

The Syncro agent is configured with very few options, suggesting that the threat actor limited to just the functionality they needed.

The configuration files shows that the agent checks in with the server every 90 seconds. It does not have enabled the built-in remote access and doesn’t deploy the  remote support utilities Splashtop, which is bundled with the Syncro platform, or TeamViewer, for which an integration exists.

Furthermore, the extracted configuration did not contain policies to deploy security solutions on the compromised endpoint, and disabled the Emsisoft, Webroot, and Bitdefender agents.

Once ScreenConnect is installed on a device, the threat actors can remotely connect to a target’s computer and deploy further malware payloads, steal data, and potentially access the password vaults of users through saved credentials.

Phishing for 1Password accounts

Last week, another campaign targeted 1Password users with emails falsely warning that their accounts had been compromised. The indicators for that activity, from the wording in the message and landing URL, to the sender address (watchtower@eightninety[.]com) were different.
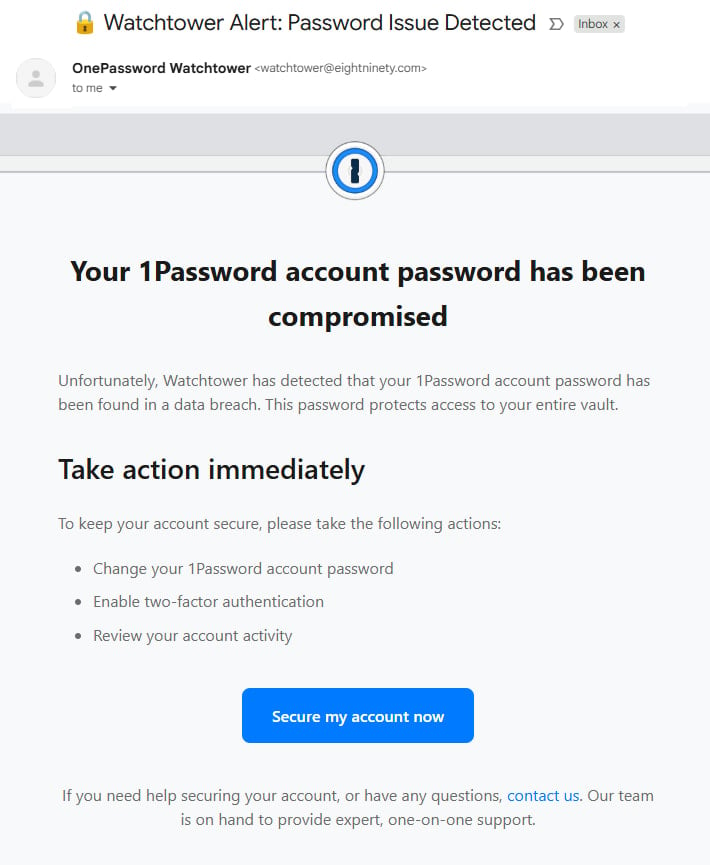
The 1Password-themed phish
Source: Malwarebytes

Researchers at cybersecurity company Malwarebytes say that users clicking on an embedded button were taken to a phishing page (onepass-word[.]com) via a Mandrillapp redirection.

The attacks targeting 1Password were first reported by Brett Christensen (Hoax-Slayer) on September 25.
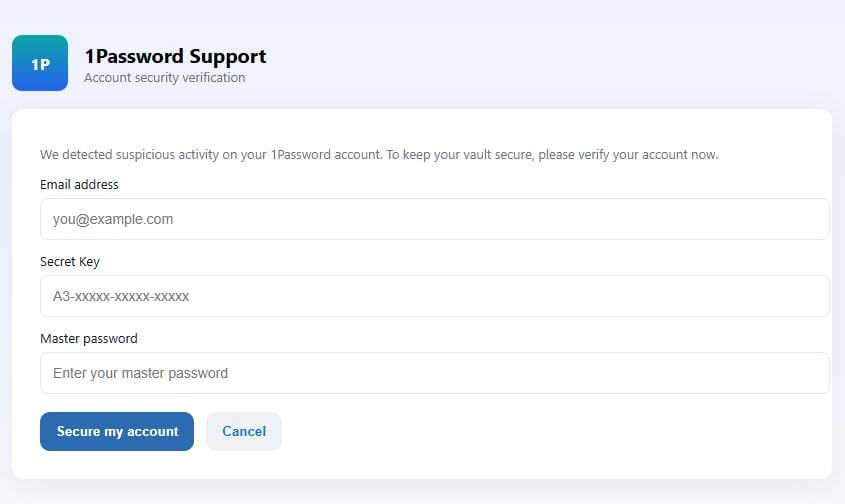
The landing page asking for the master password
Source: Malwarebytes

Users of password management tools should ignore such alerts and always login to the provider’s official website to check for any security alerts pending review.

Important security incidents like those claimed in the emails are also broadly communicated across the companies’ blogs and via press releases, so double-checking on official channels is always a good practice.

It is also worth remembering that companies won’t ever ask for the master password to your vaults.

Update 10/16 – Syncro sent the below statement to BleepingComputer regarding the phishing campaign:

“We identified the malicious accounts and have shut down the installs to ensure that no further agents can be installed. The Syncro platform itself was not compromised but rather a malicious actor posing as an MSP that created this account and then used it for nefarious purposes.” – A Syncro spokesperson

Source and more details: https://www.bleepingcomputer.com/news/security/fake-lastpass-bitwarden-breach-alerts-lead-to-pc-hijacks/
Weak Password Let Ransomware Gang Destroy 158-Year-Old Company

A single compromised password brought down KNP Logistics, putting 730 employees out of work and highlighting the devastating impact of cyber attacks on British businesses.

One password is believed to have been all it took for a ransomware gang to destroy a 158-year-old company and put 700 people out of work.

KNP Logistics, a Northamptonshire transport company with roots dating back to 1865, became the latest victim of the Akira ransomware group in June 2024, joining tens of thousands of UK businesses that have fallen prey to such attacks.

The devastating breach began when hackers managed to gain entry to KNP’s computer systems by guessing an employee’s password. Once inside, the Akira gang deployed ransomware that encrypted the company’s essential data and locked down its internal systems, demanding an estimated £5 million ransom.

The attack crippled KNP’s ability to operate, access financial records, and secure crucial new funding, ultimately forcing the 158-year-old firm into administration.

KNP director Paul Abbott revealed the human cost of the cyber attack, admitting he hasn’t told the employee whose compromised password likely led to the company’s destruction. “Would you want to know if it was you?” he asks, highlighting the psychological burden these incidents place on workers.

The collapse of KNP is part of a broader wave of ransomware attacks targeting UK businesses. Major retailers including Marks & Spencer, Co-op, and Harrods have all been hit by cyber criminals in recent months, reads the BBC report.

M&S suffered massive disruption after hackers deployed DragonForce ransomware, resulting in estimated weekly losses of £40 million. Meanwhile, Co-op confirmed that all 6.5 million of its members had their personal data stolen in a separate attack.

Richard Horne, CEO of the National Cyber Security Centre (NCSC), warns that organizations must urgently strengthen their defenses. “We need organisations to take steps to secure their systems, to secure their businesses,” he said, as the NCSC battles international ransomware gangs.

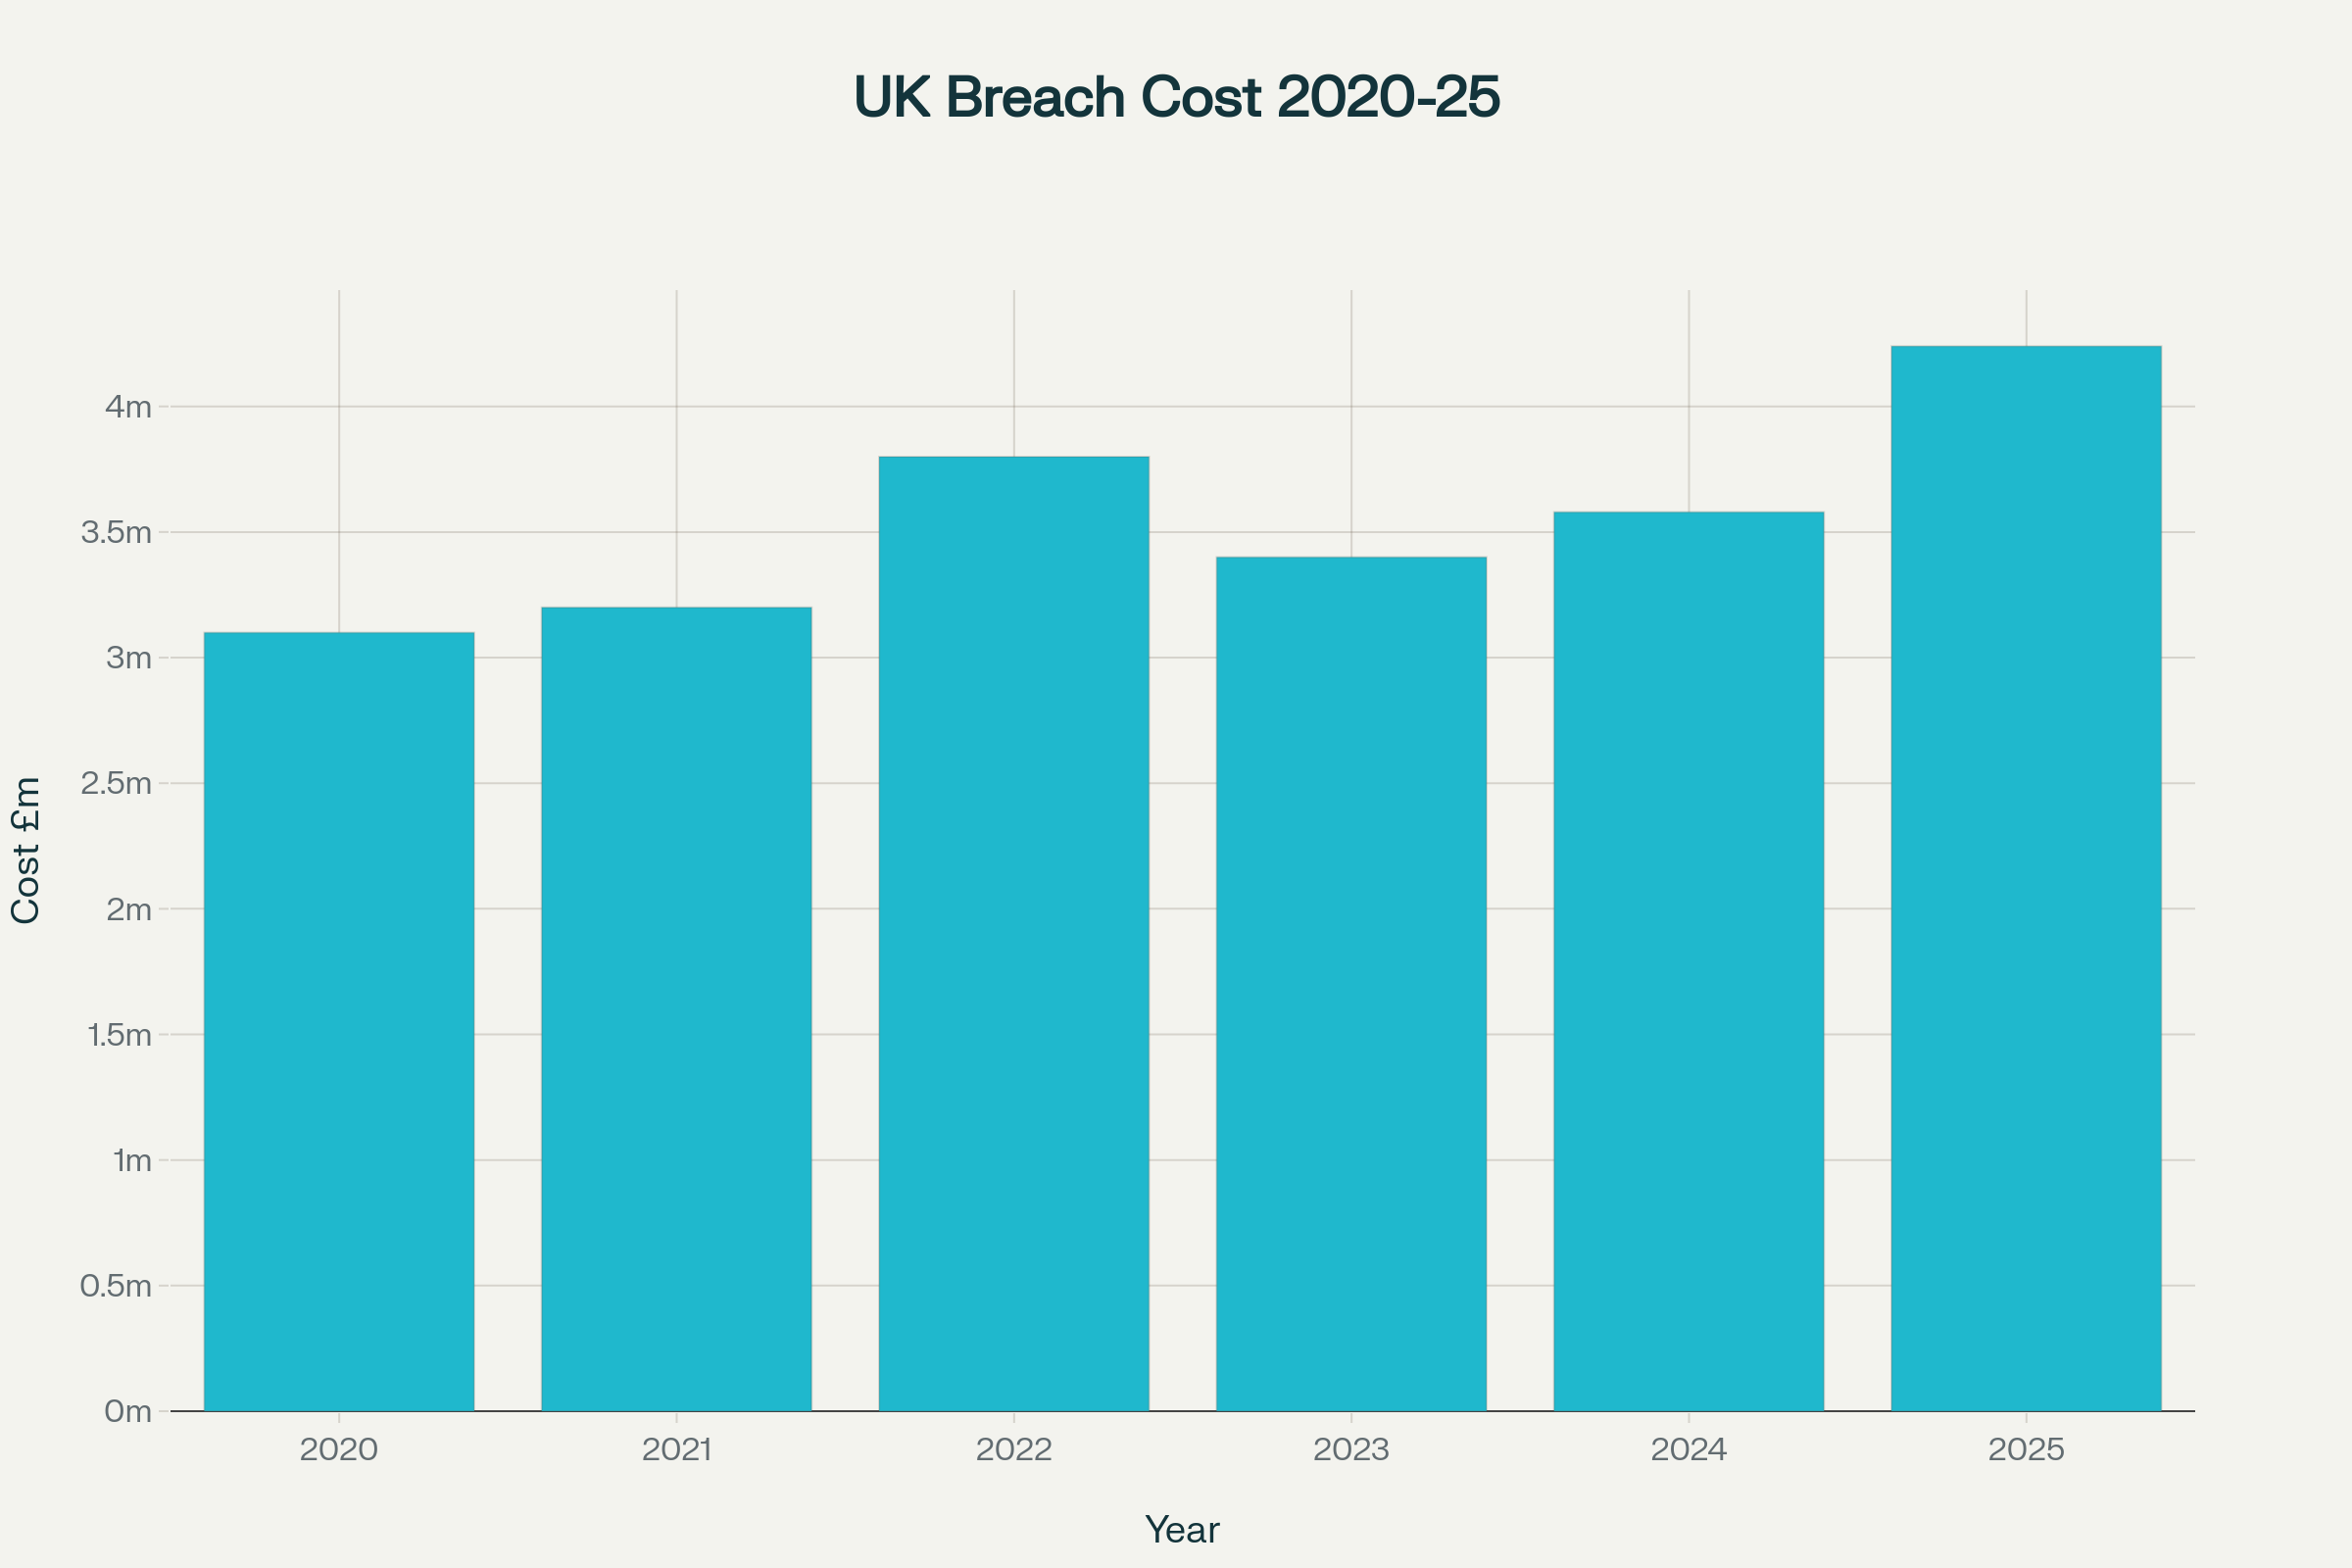
The financial impact of such attacks is escalating dramatically. Research shows that over 80% of data breaches are linked to compromised credentials, with the average cost of a UK cyber breach rising to £3.58 million between 2023 and 2024. For smaller businesses like KNP, these costs can prove fatal.

Rising costs of cyber breaches for UK businesses, showing the escalating financial impact of ransomware and cyber attacks from 2020-2025

Small and medium-sized enterprises (SMEs) are particularly vulnerable, with 56% of all ransomware attacks in 2024 targeting businesses with fewer than 50 employees.

The Akira group, which emerged in March 2023, has specifically focused on SMEs across the UK and US, earning an estimated $42 million from over 250 attacks in its first year.

Cybersecurity experts emphasize that basic password hygiene remains the first line of defense. Studies reveal that hacking tools can crack 96% of common passwords in less than a second, while employees frequently reuse passwords across multiple accounts.

As UK authorities arrested four suspects connected to recent retail cyber attacks, the message is clear: no business, regardless of size or history, is immune from the ransomware threat.

Source: https://cybersecuritynews.com/weak-password-destroy-158-year-old-company/

Massive botnet that appeared overnight is delivering record-size DDoSes

Eleven11bot infects video recorders, with the largest concentration of them in the US.

A newly discovered network botnet comprising an estimated 30,000 webcams and video recorders—with the largest concentration in the US—has been delivering what is likely to be the biggest denial-of-service attack ever seen, a security researcher inside Nokia said.

The botnet, tracked under the name Eleven11bot, first came to light in late February when researchers inside Nokia’s Deepfield Emergency Response Team observed large numbers of geographically dispersed IP addresses delivering “hyper-volumetric attacks.” Eleven11bot has been delivering large-scale attacks ever since.

Volumetric DDoSes shut down services by consuming all available bandwidth either inside the targeted network or its connection to the Internet. This approach works differently than exhaustion DDoSes, which over-exert the computing resources of a server. Hypervolumetric attacks are volumetric DDoses that deliver staggering amounts of data, typically measured in the terabits per second.

Johnny-come-lately botnet sets a new record

At 30,000 devices, the Eleven11bot was already exceptionally large (although some botnets exceed well over 100,000 devices). Most of the IP addresses participating, Nokia researcher Jérôme Meyer told me, had never been seen engaging in DDoS attacks.

Besides a 30,000-node botnet seeming to appear overnight, another salient feature of Eleven11bot is the record-size volume of data it sends its targets. The largest one Nokia has seen from Eleven11bot so far occurred on February 27 and peaked at about 6.5 terabits per second. The previous record for a volumetric attack was reported in January at 5.6 Tbps.

“Eleven11bot has targeted diverse sectors, including communications service providers and gaming hosting infrastructure, leveraging a variety of attack vectors,” Meyer wrote. While in some cases the attacks are based on the volume of data, others focus on flooding a connection with more data packets than a connection can handle, with numbers ranging from a “few hundred thousand to several hundred million packets per second.” Service degradation caused in some attacks has lasted multiple days, with some remaining ongoing as of the time this post went live.

A breakdown showed that the largest concentration of IP addresses, at 24.4 percent, was located in the US. Taiwan was next at 17.7 percent, and the UK at 6.5 percent.

In an online interview, Meyer made the following points:

  • This botnet is much larger than what we’re used to seeing in DDoS attacks (the only precedent I have in mind is an attack from 2022 right after the Ukraine invasion, at ~60k bots, but not public).
  • The vast majority of its IPs were not involved in DDoS attacks prior to last week.
  • Most of the IPs are security cameras (Censys thinks Hisilicon, I saw multiple sources talk to a Hikvision NVR too so that is a possibility but not my area of expertise).
  • partly because the botnet is larger than average, the attack size is also larger than average.

According to a post updated on Wednesday from security firm Greynoise, Eleven11bot is most likely a variant of Mirai, a family of malware for infecting webcams and other Internet of Things devices. Mirai debuted in 2016, when tens of thousands of IoT devices infected by it delivered what at the time were record-setting DDoSes of about 1 Tbps and took down security news site KrebsOnSecurity for almost a week. Shortly after that, Mirai developers published their source code in a move that made it easy for copycats everywhere to deliver the same massive attacks. Greynoise said that the variant driving Eleven11bot is using a single new exploit to infect TVT-NVMS 9000 digital video recorders that run on HiSilicon chips.

There have been conflicting reports on the number of devices comprising Eleven11bot. Following Nokia’s report last Saturday of roughly 30,000 devices, the nonprofit Shadowserver Foundation said Tuesday that the true size was more than 86,000. Then in Wednesday’s update, Greynoise said that based on data from fellow security firm Censys, both numbers were inflated and the true number was likely fewer than 5,000.

The upward revision from Shadowserver was likely the result of the belief that all infected devices displayed unique device information. That suspicion now appears to be incorrect. Instead, Meyer believes the information seen on infected devices is displayed on all such hardware, whether infected or not. Researchers from Greynoise and Censys weren’t immediately available to explain how they arrived at the much lower estimate of fewer than 5,000.

Meyer said that he has consistently observed as many as 20,000 to 30,000 IP addresses participating in follow-on attacks, although many attacks come from much smaller subsets. He said that he has since sent a list of all 30,000 or so IP addresses he has observed to Censys and plans to also send them to Shadowserver soon in hopes of getting consensus on the true size.

“I am still confident on the estimated count as this is what we keep seeing in attacks and after human review of the source IPs,” he wrote.

Mirai-based botnets employ various methods for infecting their targets. One common method is to attempt to log in to device administrator accounts using username/password pairs commonly set as defaults by manufacturers. Mirai botnets have also been known to exploit vulnerabilities that bypass security settings.

In any case, anyone running any sort of IoT devices should position them behind a router or other form of firewall so they’re not visible from outside a local network. Remote administration from outside the Internet should be enabled only when needed. Users should also ensure each device is protected by a strong unique password. Last, devices should be updated as soon as security patches become available.

Source: https://arstechnica.com/security/2025/03/massive-botnet-that-appeared-overnight-is-delivering-record-size-ddoses/

390,000 WordPress accounts stolen from hackers in supply chain attack

A threat actor tracked as MUT-1244 has stolen over 390,000 WordPress credentials in a large-scale, year-long campaign targeting other threat actors using a trojanized WordPress credentials checker.

Researchers at Datadog Security Labs, who spotted the attacks, say that SSH private keys and AWS access keys were also stolen from the compromised systems of hundreds of other victims, believed to include red teamers, penetration testers, security researchers, as well as malicious actors.

The victims were infected using the same second-stage payload pushed via dozens of trojanized GitHub repositories delivering malicious proof-of-concept (PoC) exploits that targeted known security flaws, along with a phishing campaign prompting targets to install a fake kernel upgrade camouflaged as a CPU microcode update.

While the phishing emails tricked victims into executing commands that installed the malware, the fake repositories duped security professionals and threat actors seeking exploit code for specific vulnerabilities.

Threat actors have used fake proof-of-concept exploits in the past to target researchers, hoping to steal valuable research or gain access to the networks of cybersecurity firms.

“Due to their naming, several of these repositories are automatically included in legitimate sources, such as Feedly Threat Intelligence or Vulnmon, as proof-of-concept repositories for these vulnerabilities,” the researchers said.” This increases their look of legitimacy and the likelihood that someone will run them.”

The payloads were dropped via GitHub repos using multiple methods, including backdoored configure compilation files, malicious PDF files, Python droppers, and malicious npm packages included in the projects’ dependencies.

As Datadog Security Labs found, this campaign overlaps with one highlighted in a November Checkmarkx report about a year-long supply-chain attack in which the “hpc20235/yawp” GitHub project was trojanized using malicious code in the “0xengine/xmlrpc” npm package to steal data and mine Monero cryptocurrency.

Malware deployed in these attacks includes a cryptocurrency miner and a backdoor that helped MUT-1244 collect and exfiltrate private SSH keys, AWS credentials, environment variables, and key directory contents such as “~/.aws.” 

The second-stage payload, hosted on a separate platform, allowed the attackers to exfiltrate data to file-sharing services like Dropbox and file.io, with the investigators finding hardcoded credentials for these platforms within the payload, giving the attackers easy access to the stolen info.

“MUT-1244 was able to gain access to over 390,000 credentials, believed to be WordPress ones. We assess with high confidence that before these credentials were exfiltrated to Dropbox, they were in the hands of offensive actors, who likely acquired them through illicit means,” Datadog Security Labs researchers said.

“These actors were then compromised through the yawpp tool they used to check the validity of these credentials. Since MUT-1244 advertised yawpp as a “credentials checker” for WordPress, it’s no surprise that an attacker with a set of stolen credentials (which are often purchased from underground markets as a way to speed up threat actor operations) would use yawpp to validate them.”

The attackers successfully exploited trust within the cybersecurity community to compromise dozens of machines belonging to both white hat and black hat hackers after the targets unknowingly executed the threat actor’s malware, leading to data theft that included SSH keys, AWS access tokens, and command histories.

Datadog Security Labs estimates that hundreds of systems remain compromised, and others are still getting infected as part of this ongoing campaign.

Source: https://www.bleepingcomputer.com/news/security/390-000-wordpress-accounts-stolen-from-hackers-in-supply-chain-attack/

How Infostealers Pillaged the World’s Passwords


Infostealer malware is swiping millions of passwords, cookies, and search histories. It’s a gold mine for hackers—and a disaster for anyone who becomes a target.

For the past two months, cybercriminals have advertised for sale hundreds of millions of customer records from major companies like Ticketmaster, Santander Bank, and AT&T. And while massive data breaches have been a fact of life for more than a decade now, these recent examples are significant, because they are all connected. Each victim company was a customer of the cloud data storage firm Snowflake and was compromised not through a sophisticated hack, but because attackers had login credentials for each victim company’s Snowflake accounts—a data-stealing spree that impacted at least 165 Snowflake customers.

Attackers didn’t grab this trove of logins by directly breaching Snowflake or through a targeted supply chain attack. Instead, they found the credentials in a hodgepodge of stolen data grabbed haphazardly by “infostealer” malware.

After years of operation, infostealers are having a moment. The malware, which often finds its way onto people’s machines through downloads of pirated software, can steal usernames and passwords, cookies, search history, financial information, and more from web browsers. This data collected by infostealers is increasingly being used by all kinds of hackers to compromise companies—and cybersecurity experts warn of more high-profile data breaches to come.

“We’ve seen nation-states leverage infostealers, we’ve seen criminals leverage infostealers, and we’ve seen teenage hacking crews leverage infostealers,” says Charles Carmakal, chief technology officer of Google-owned cybersecurity firm Mandiant. Russia’s APT29 hackers and cybercriminal gangs such as Lapsus$ and Scattered Spider are among the many hackers using infostealers. Just days after the global CrowdStrike outage, hackers created a new infostealer in an attempt to capitalize on the chaos.

Infostealers are defined less by their technical capabilities and more by their role in the malicious hacker ecosystem. Of course, to minimally qualify, they must be designed to steal information. But what separates infostealers from spyware or other malware used in espionage or targeted data breaches is that infostealers are spread opportunistically and indiscriminately. They grab data from the browsers of whatever computers they end up infecting. Then the attackers who run them compile and organize this chaotic and largely random assemblage of data—often on a marketplace or in a public forum like a Telegram channel. It is only then that infostealer operators or their customers comb their haul for valuable credentials and access tokens amidst the massive amount of junk. Ian Gray, director of analysis and research at the security firm Flashpoint, says there are likely hundreds of variants of infostealers in circulation.

There are some account access tokens that would have obvious value for many types of cybercriminals. If a data dump included working login credentials for a corporate employee’s enterprise accounts, a ransomware gang, business email compromise scammer, or state-backed actor could use the access as a jumping off point to launch their attacks. But in addition to selling these prized details, infostealer operators maximize the value of the data they collect simply by making their stolen data available. Platforms like Genesis Market, which was taken down by law enforcement last year, and Russian Market, organize infostealer logs and even make them somewhat searchable so hackers who are looking to target more niche organizations or those who don’t have financial motivations can potentially find exactly what they need.

These platforms take cues in how they are designed and marketed from legitimate information and ecommerce services. Many markets and forums charge a subscription fee to access the platform and then have different pricing structures for data depending on how valuable it might be. Currently, Gray says, Russian Market has so much stolen data available from infostealers that it has been charging a low flat rate, typically no more than $10, for any subset of data users want to download.

“Organizations have become very good with their security, and people have also gotten more savvy, so they’re not the best targets now,” for traditional tailored attacks, Gray says. “So attackers need something that’s less targeted and more based on what they can make use of. Infostealers are modular and often sold on a subscription basis, and that evolution probably aligns with the rise of modern subscription services like video streaming.”

Infostealers have been especially effective with the rise of remote work and hybrid work, as companies adapt to allowing employees to access work services from personal devices and personal accounts from work devices. This creates opportunities for infostealers to randomly compromise individuals on, say, their home computers but still end up with corporate access credentials because the person was logged into some of their work systems as well. It also makes it easier for infostealing malware to get around corporate protections, even on enterprise devices, if employees are able to have their personal email or social media accounts open.

“I started paying attention to this once it became an enterprise problem,” Mandiant’s Carmakal says. “And particularly around 2020, because I started seeing more intrusions of enterprises first starting from compromises of home computers—through phishing of people’s Yahoo accounts, Gmail accounts, and Hotmail accounts that were totally unrelated to any enterprise targeting, but to me look very opportunistic.”

Victoria Kivilevich, director of threat research at security firm KELA, says that in some instances criminals can use cybercrime markets to search for the domain of potential targets and see if any credentials are available. Kivilevich says the sale of infostealer data can be considered as the “supply chain” for various types of cyberattacks, including ransomware operators looking for the details of potential victims, those involved in business email compromise, and even initial access brokers who can sell the details along again to other cybercriminals.

On various cybercrime marketplaces and Telegram, Kivilevich says, there have been more than 7,000 compromised credentials linked to Snowflake accounts being shared. In one instance, a criminal has been touting access to 41 companies from the education sector; another cybercriminal claims to be selling access to US companies with revenues between $50 million and $8 billion, according to Kivilevich’s analysis.

“I don’t think there was one company that came to us and had zero accounts compromised by infostealer malware,” Kivilevich says of the threat that infostealer logs provide to businesses, with KELA saying infostealer-related activity jumped in 2023. Irina Nesterovsky, KELA’s chief research officer, says millions of credentials have been collected by infostealing malware in recent years. “This is a real threat,” Nesterovsky says.

Carmakal says there are multiple steps companies and individuals can take to protect themselves from the threat of infostealers and their aftereffects, including using antivirus or EDR products to detect malicious activity. Companies should be strict on enforcing multifactor authentication across their users, he says. “We try to encourage people to not synchronize passwords on their corporate devices with their personal devices,” Carmakal adds.

The use of infostealers has been working so well that it is all but inevitable that cybercriminals will look to replicate the success of compromise sprees like Snowflake and get creative about other enterprise software services that they can use as entry points for access to an array of different customer companies. Carmakal warns that he expects to see this result in more breaches in the coming months. “There’s no ambiguity about this,” he says. “Threat actors will start hunting for infostealer logs, and looking for other SaaS providers, similar to Snowflake, where they log in and steal data, and then extort those companies.”

Source: https://www.wired.com/story/infostealer-malware-password-theft/

The LastPass hack saga just keeps getting worse

Already smarting from a breach that stole customer vaults, LastPass has more bad news.

Already smarting from a breach that put partially encrypted login data into a threat actor’s hands, LastPass on Monday said that the same attacker hacked an employee’s home computer and obtained a decrypted vault available to only a handful of company developers.

Although an initial intrusion into LastPass ended on August 12, officials with the leading password manager said the threat actor “was actively engaged in a new series of reconnaissance, enumeration, and exfiltration activity” from August 12 to August 26. In the process, the unknown threat actor was able to steal valid credentials from a senior DevOps engineer and access the contents of a LastPass data vault. Among other things, the vault gave access to a shared cloud-storage environment that contained the encryption keys for customer vault backups stored in Amazon S3 buckets.

“This was accomplished by targeting the DevOps engineer’s home computer and exploiting a vulnerable third-party media software package, which enabled remote code execution capability and allowed the threat actor to implant keylogger malware,” LastPass officials wrote. “The threat actor was able to capture the employee’s master password as it was entered, after the employee authenticated with MFA, and gain access to the DevOps engineer’s LastPass corporate vault.”

The hacked DevOps engineer was one of only four LastPass employees with access to the corporate vault. Once in possession of the decrypted vault, the threat actor exported the entries, including the “decryption keys needed to access the AWS S3 LastPass production backups, other cloud-based storage resources, and some related critical database backups.”

Monday’s update comes two months after LastPass issued a previous bombshell update that for the first time said that, contrary to previous assertions, the attackers had obtained customer vault data containing both encrypted and plaintext data. LastPass said then that the threat actor had also obtained a cloud storage access key and dual storage container decryption keys, allowing for the copying of customer vault backup data from the encrypted storage container.

The backup data contained both unencrypted data, such as website URLs, as well as website usernames and passwords, secure notes, and form-filled data, which had an additional layer of encryption using 256-bit AES. The new details explain how the threat actor obtained the S3 encryption keys.

Monday’s update said that the tactics, techniques, and procedures used in the first incident were different from those used in the second one and that, as a result, it wasn’t initially clear to investigators that the two were directly related. During the second incident, the threat actor used information obtained during the first one to enumerate and exfiltrate the data stored in the S3 buckets.

“Alerting and logging was enabled during these events, but did not immediately indicate the anomalous behavior that became clearer in retrospect during the investigation,” LastPass officials wrote. “Specifically, the threat actor was able to leverage valid credentials stolen from a senior DevOps engineer to access a shared cloud-storage environment, which initially made it difficult for investigators to differentiate between threat actor activity and ongoing legitimate activity.”

LastPass learned of the second incident from Amazon’s warnings of anomalous behavior when the threat actor tried to use Cloud Identity and Access Management (IAM) roles to perform unauthorized activity.

According to a person briefed on a private report from LastPass who spoke on the condition of anonymity, the media software package that was exploited on the employee’s home computer was Plex. Interestingly, Plex reported its own network intrusion on August 24, just 12 days after the second incident commenced. The breach allowed the threat actor to access a proprietary database and make off with password data, usernames, and emails belonging to some of its 30 million customers. Plex is a major provider of media streaming services that allow users to stream movies and audio, play games, and access their own content hosted on home or on-premises media servers.

It’s not clear if the Plex breach has any connection to the LastPass intrusions. Representatives of LastPass and Plex didn’t respond to emails seeking comment for this story.

The threat actor behind the LastPass breach has proven especially resourceful, and the revelation that it successfully exploited a software vulnerability on the home computer of an employee further reinforces that view. As Ars advised in December, all LastPass users should change their master passwords and all passwords stored in their vaults. While it’s not clear whether the threat actor has access to either, the precautions are warranted.

Sources: https://arstechnica.com/information-technology/2023/02/lastpass-hackers-infected-employees-home-computer-and-stole-corporate-vault/

PSA: Your Site Isn’t Hacked By This Bitcoin Scam, Keep the Money

On January 19th, 2023, a member of the Wordfence Threat Intelligence team received an email from their personal blog, claiming the site had been hacked, and we received two reports from Wordfence users who received the same message. The email claimed that the site had been hacked due to a vulnerability on the site. The email went on to demand about $3,000 worth of Bitcoin to prevent the malicious actor from damaging the site’s reputation. This is of course only a scare tactic, and not a true cause for concern. The site was not actually hacked.

This campaign appears to have begun on or around January 18, 2023, and while our data on it is light, the campaign is ongoing. The messages are being sent by a threat actor or a bot they control to submit the message through a contact form on a website. As we do not have data on emails submitted directly through a contact form, this attack campaign is likely to be significantly more prolific than the numbers we have available.

The message in question, which can be seen below in its email form, is a scare tactic that is used to trick victims into paying to prevent a leak of sensitive data, damage to the website, or whatever other potential consequences the vague threat may conjure up in the site owner’s mind.

From: Manie Hedin hacker@sludgepool.org
Subject: Your Site Has Been Hacked

Message Body:
Your Site Has Been Hacked

PLEASE FORWARD THIS EMAIL TO SOMEONE IN YOUR COMPANY WHO IS ALLOWED TO MAKE IMPORTANT DECISIONS!

We have hacked your website https://.com and extracted your databases.

How did this happen?

Our team has found a vulnerability within your site that we were able to exploit. After finding the vulnerability we were able to get your database credentials and extract your entire database and move the information to an offshore server.

What does this mean?

We will systematically go through a series of steps of totally damaging your reputation. First your database will be leaked or sold to the highest bidder which they will use with whatever their intentions are. Next if there are e-mails found they will be e-mailed that their information has been sold or leaked and your https://.com was at fault thusly damaging your reputation and having angry customers/associates with whatever angry customers/associates do. Lastly any links that you have indexed in the search engines will be de-indexed based off of blackhat techniques that we used in the past to de-index our targets.

How do I stop this?

We are willing to refrain from destroying your site’s reputation for a small fee. The current fee is $3000 in bitcoins (0.14 BTC).

The amount(approximately): $3000 (0.14 BTC)
The Address Part 1: bc1qe4xvhksgapl3p76mm
The Address Part 2: fz7thdnmkeuxry08kjhcn

So, you have to manually copy + paste Part1 and Part2 in one string made of 42 characters with no space between the parts that start with “b” and end with “n” is the actually address where you should send the money to.

Once you have paid we will automatically get informed that it was your payment. Please note that you have to make payment within 72 hours after receiving this message or the database leak, e-mails dispatched, and de-index of your site WILL start!

How do I get Bitcoins?

You can easily buy bitcoins via several websites or even offline from a Bitcoin-ATM.

What if I don’t pay?

If you decide not to pay, we will start the attack at the indicated date and uphold it until you do, there’s no counter measure to this, you will only end up wasting more money trying to find a solution. We will completely destroy your reputation amongst google and your customers.

This is not a hoax, do not reply to this email, don’t try to reason or negotiate, we will not read any replies. Once you have paid we will stop what we were doing and you will never hear from us again!

Please note that Bitcoin is anonymous and no one will find out that you have complied.

While this extortion campaign may not pose any real danger, it is still important to take website security seriously. WordPress core, themes, and plugins need to be updated with the latest security updates to patch known vulnerabilities. Even with everything updated, there may be vulnerabilities that are not publicly known and do not have an available patch. For this reason, a website security solution that includes a web application firewall (WAF) that can block common exploits, such as Wordfence, should be implemented.

Cyber Observables
While this extortion campaign is still in its early stages, there are some observables that can be used to identify and block these extortion attempts.

Email Address
hacker@sludgepool[.]org

Bitcoin Address
bc1qe4xvhksgapl3p76mmfz7thdnmkeuxry08kjhcn

IP Addresses
138.199.18.140
138.199.18.61
212.102.57.5
216.24.216.249
212.102.57.24

Conclusion
In this post, we discussed an emerging extortion campaign where emails are being sent to site owners through contact forms. This campaign does not pose an actual threat to the website, but serves as a reminder to keep websites updated and implement a website security solution.

Source: https://www.wordfence.com/blog/2023/01/psa-your-site-isnt-hacked-by-this-bitcoin-scam-keep-the-money/

Hundreds of WordPress sites infected by recently discovered backdoor

People who use WordPress should check their sites for unpatched plugins.

Malware that exploits unpatched vulnerabilities in 30 different WordPress plugins has infected hundreds if not thousands of sites and may have been in active use for years, according to a writeup published last week.

The Linux-based malware installs a backdoor that causes infected sites to redirect visitors to malicious sites, researchers from security firm Dr.Web said. It’s also able to disable event logging, go into standby mode, and shut itself down. It gets installed by exploiting already-patched vulnerabilities in plugins that website owners use to add functionality like live chat or metrics-reporting to the core WordPress content management system.

“If sites use outdated versions of such add-ons, lacking crucial fixes, the targeted web pages are injected with malicious JavaScripts,” Dr.Web researchers wrote. “As a result, when users click on any area of an attacked page, they are redirected to other sites.”

Searches such as this one indicate that more than 1,300 sites contain the JavaScript that powers the backdoor. It’s possible that some of those sites have removed the malicious code since the last scan. Still, it provides an indication of the reach of the malware.

The plugins exploited include:

WP Live Chat Support Plugin
WordPress – Yuzo Related Posts
Yellow Pencil Visual Theme Customizer Plugin
Easysmtp
WP GDPR Compliance Plugin
Newspaper Theme on WordPress Access Control (vulnerability CVE-2016-10972)
Thim Core
Google Code Inserter
Total Donations Plugin
Post Custom Templates Lite
WP Quick Booking Manager
Facebook Live Chat by Zotabox
Blog Designer WordPress Plugin
WordPress Ultimate FAQ (vulnerabilities CVE-2019-17232 and CVE-2019-17233)
WP-Matomo Integration (WP-Piwik)
WordPress ND Shortcodes For Visual Composer
WP Live Chat
Coming Soon Page and Maintenance Mode
Hybrid
Brizy WordPress Plugin
FV Flowplayer Video Player
WooCommerce
WordPress Coming Soon Page
WordPress theme OneTone
Simple Fields WordPress Plugin
WordPress Delucks SEO plugin
Poll, Survey, Form & Quiz Maker by OpinionStage
Social Metrics Tracker
WPeMatico RSS Feed Fetcher
Rich Reviews plugin

“If one or more vulnerabilities are successfully exploited, the targeted page is injected with a malicious JavaScript that is downloaded from a remote server,” the Dr.Web writeup explained. “With that, the injection is done in such a way that when the infected page is loaded, this JavaScript will be initiated first—regardless of the original contents of the page. At this point, whenever users click anywhere on the infected page, they will be transferred to the website the attackers need users to go to.”

The JavaScript contains links to a variety of malicious domains, including:

lobbydesires[.]com
letsmakeparty3[.]ga
deliverygoodstrategies[.]com
gabriellalovecats[.]com
css[.]digestcolect[.]com
clon[.]collectfasttracks[.]com
Count[.]trackstatisticsss[.]com


The researchers found two versions of the backdoor: Linux.BackDoor.WordPressExploit.1 and Linux.BackDoor.WordPressExploit.2. They said the malware may have been in use for three years.

WordPress plugins have long been a common means for infecting sites. While the security of the main application is fairly robust, many plugins are riddled with vulnerabilities that can lead to infection. Criminals use infected sites to redirect visitors to sites used for phishing, ad fraud, and distributing malware.

People running WordPress sites should ensure that they’re using the most current versions of the main software as well as any plugins. They should prioritize updating any of the plugins listed above.

Source: https://arstechnica.com/information-technology/2023/01/hundreds-of-wordpress-sites-infected-by-recently-discovered-backdoor/

New Linux malware uses 30 plugin exploits to backdoor WordPress sites

A previously unknown Linux malware has been exploiting 30 vulnerabilities in multiple outdated WordPress plugins and themes to inject malicious JavaScript.

According to a report by antivirus vendor Dr. Web, the malware targets both 32-bit and 64-bit Linux systems, giving its operator remote command capabilities.

The main functionality of the trojan is to hack WordPress sites using a set of hardcoded exploits that are run successively, until one of them works.

The targeted plugins and themes are the following:

  • WP Live Chat Support Plugin
  • WordPress – Yuzo Related Posts
  • Yellow Pencil Visual Theme Customizer Plugin
  • Easysmtp
  • WP GDPR Compliance Plugin
  • Newspaper Theme on WordPress Access Control (CVE-2016-10972)
  • Thim Core
  • Google Code Inserter
  • Total Donations Plugin
  • Post Custom Templates Lite
  • WP Quick Booking Manager
  • Faceboor Live Chat by Zotabox
  • Blog Designer WordPress Plugin
  • WordPress Ultimate FAQ (CVE-2019-17232 and CVE-2019-17233)
  • WP-Matomo Integration (WP-Piwik)
  • WordPress ND Shortcodes For Visual Composer
  • WP Live Chat
  • Coming Soon Page and Maintenance Mode
  • Hybrid

If the targeted website runs an outdated and vulnerable version of any of the above, the malware automatically fetches malicious JavaScript from its command and control (C2) server, and injects the script into the website site.

Infected pages act as redirectors to a location of the attacker’s choosing, so the scheme works best on abandoned sites.

These redirections may serve in phishing, malware distribution, and malvertising campaigns to help evade detection and blocking. That said, the operators of the auto-injector might be selling their services to other cybercriminals.

An updated version of the payload that Dr. Web observed in the wild also targets the following WordPress add-ons:

  • Brizy WordPress Plugin
  • FV Flowplayer Video Player
  • WooCommerce
  • WordPress Coming Soon Page
  • WordPress theme OneTone
  • Simple Fields WordPress Plugin
  • WordPress Delucks SEO plugin
  • Poll, Survey, Form & Quiz Maker by OpinionStage
  • Social Metrics Tracker
  • WPeMatico RSS Feed Fetcher
  • Rich Reviews plugin

The new add-ons targeted by the new variant indicate that the development of the backdoor is active at the moment.

Dr. Web also mentions that both variants contain functionality that is currently inactive, which would allow brute-forcing attacks against website administrator accounts.

Defending against this threat requires admins of WordPress websites to update to the latest available version the themes and plugins running on the site and replace those that are no longer developed with alternatives that being supported.

Using strong passwords and activating the two-factor authentication mechanism should help ensure protection against brute-force attacks.

Source: https://www.bleepingcomputer.com/news/security/new-linux-malware-uses-30-plugin-exploits-to-backdoor-wordpress-sites/

New Ransom Payment Schemes Target Executives, Telemedicine

Ransomware groups are constantly devising new methods for infecting victims and convincing them to pay up, but a couple of strategies tested recently seem especially devious. The first centers on targeting healthcare organizations that offer consultations over the Internet and sending them booby-trapped medical records for the “patient.” The other involves carefully editing email inboxes of public company executives to make it appear that some were involved in insider trading.

Alex Holden is founder of Hold Security, a Milwaukee-based cybersecurity firm. Holden’s team gained visibility into discussions among members of two different ransom groups: CLOP (a.k.a. “Cl0p” a.k.a. “TA505“), and a newer ransom group known as Venus.

Last month, the U.S. Department of Health and Human Services (HHS) warned that Venus ransomware attacks were targeting a number of U.S. healthcare organizations. First spotted in mid-August 2022, Venus is known for hacking into victims’ publicly-exposed Remote Desktop services to encrypt Windows devices.

Holden said the internal discussions among the Venus group members indicate this gang has no problem gaining access to victim organizations.

“The Venus group has problems getting paid,” Holden said. “They are targeting a lot of U.S. companies, but nobody wants to pay them.”

Which might explain why their latest scheme centers on trying to frame executives at public companies for insider trading charges. Venus indicated it recently had success with a method that involves carefully editing one or more email inbox files at a victim firm — to insert messages discussing plans to trade large volumes of the company’s stock based on non-public information.

“We imitate correspondence of the [CEO] with a certain insider who shares financial reports of his companies through which your victim allegedly trades in the stock market, which naturally is a criminal offense and — according to US federal laws [includes the possibility of up to] 20 years in prison,” one Venus member wrote to an underling.

“You need to create this file and inject into the machine(s) like this so that metadata would say that they were created on his computer,” they continued. “One of my clients did it, I don’t know how. In addition to pst, you need to decompose several files into different places, so that metadata says the files are native from a certain date and time rather than created yesterday on an unknown machine.”

Holden said it’s not easy to plant emails into an inbox, but it can be done with Microsoft Outlook .pst files, which the attackers may also have access to if they’d already compromised a victim network.

“It’s not going to be forensically solid, but that’s not what they care about,” he said. “It still has the potential to be a huge scandal — at least for a while — when a victim is being threatened with the publication or release of these records.”

The Venus ransom group’s extortion note. Image: Tripwire.com

Holden said the CLOP ransomware gang has a different problem of late: Not enough victims. The intercepted CLOP communication seen by KrebsOnSecurity shows the group bragged about twice having success infiltrating new victims in the healthcare industry by sending them infected files disguised as ultrasound images or other medical documents for a patient seeking a remote consultation.

The CLOP members said one tried-and-true method of infecting healthcare providers involved gathering healthcare insurance and payment data to use in submitting requests for a remote consultation on a patient who has cirrhosis of the liver.

“Basically, they’re counting on doctors or nurses reviewing the patient’s chart and scans just before the appointment,” Holden said. “They initially discussed going in with cardiovascular issues, but decided cirrhosis or fibrosis of the liver would be more likely to be diagnosable remotely from existing test results and scans.”

While CLOP as a money making collective is a fairly young organization, security experts say CLOP members hail from a group of Threat Actors (TA) known as “TA505,” which MITRE’s ATT&CK database says is a financially motivated cybercrime group that has been active since at least 2014. “This group is known for frequently changing malware and driving global trends in criminal malware distribution,” MITRE assessed.

In April, 2021, KrebsOnSecurity detailed how CLOP helped pioneer another innovation aimed at pushing more victims into paying an extortion demand: Emailing the ransomware victim’s customers and partners directly and warning that their data would be leaked to the dark web unless they can convince the victim firm to pay up.

Security firm Tripwire points out that the HHS advisory on Venus says multiple threat actor groups are likely distributing the Venus ransomware. Tripwire’s tips for all organizations on avoiding ransomware attacks include:

  • Making secure offsite backups.
  • Running up-to-date security solutions and ensuring that your computers are protected with the latest security patches against vulnerabilities.
  • Using hard-to-crack unique passwords to protect sensitive data and accounts, as well as enabling multi-factor authentication.
  • Encrypting sensitive data wherever possible.
  • Continuously educating and informing staff about the risks and methods used by cybercriminals to launch attacks and steal data.

While the above tips are important and useful, one critical area of ransomware preparedness overlooked by too many organizations is the need to develop — and then periodically rehearse — a plan for how everyone in the organization should respond in the event of a ransomware or data ransom incident. Drilling this breach response plan is key because it helps expose weaknesses in those plans that could be exploited by the intruders.

As noted in last year’s story Don’t Wanna Pay Ransom Gangs? Test Your Backups, experts say the biggest reason ransomware targets and/or their insurance providers still pay when they already have reliable backups of their systems and data is that nobody at the victim organization bothered to test in advance how long this data restoration process might take.

“Suddenly the victim notices they have a couple of petabytes of data to restore over the Internet, and they realize that even with their fast connections it’s going to take three months to download all these backup files,” said Fabian Wosar, chief technology officer at Emsisoft. “A lot of IT teams never actually make even a back-of-the-napkin calculation of how long it would take them to restore from a data rate perspective.”

Source: https://krebsonsecurity.com/2022/12/new-ransom-payment-schemes-target-executives-telemedicine/